Or Weis
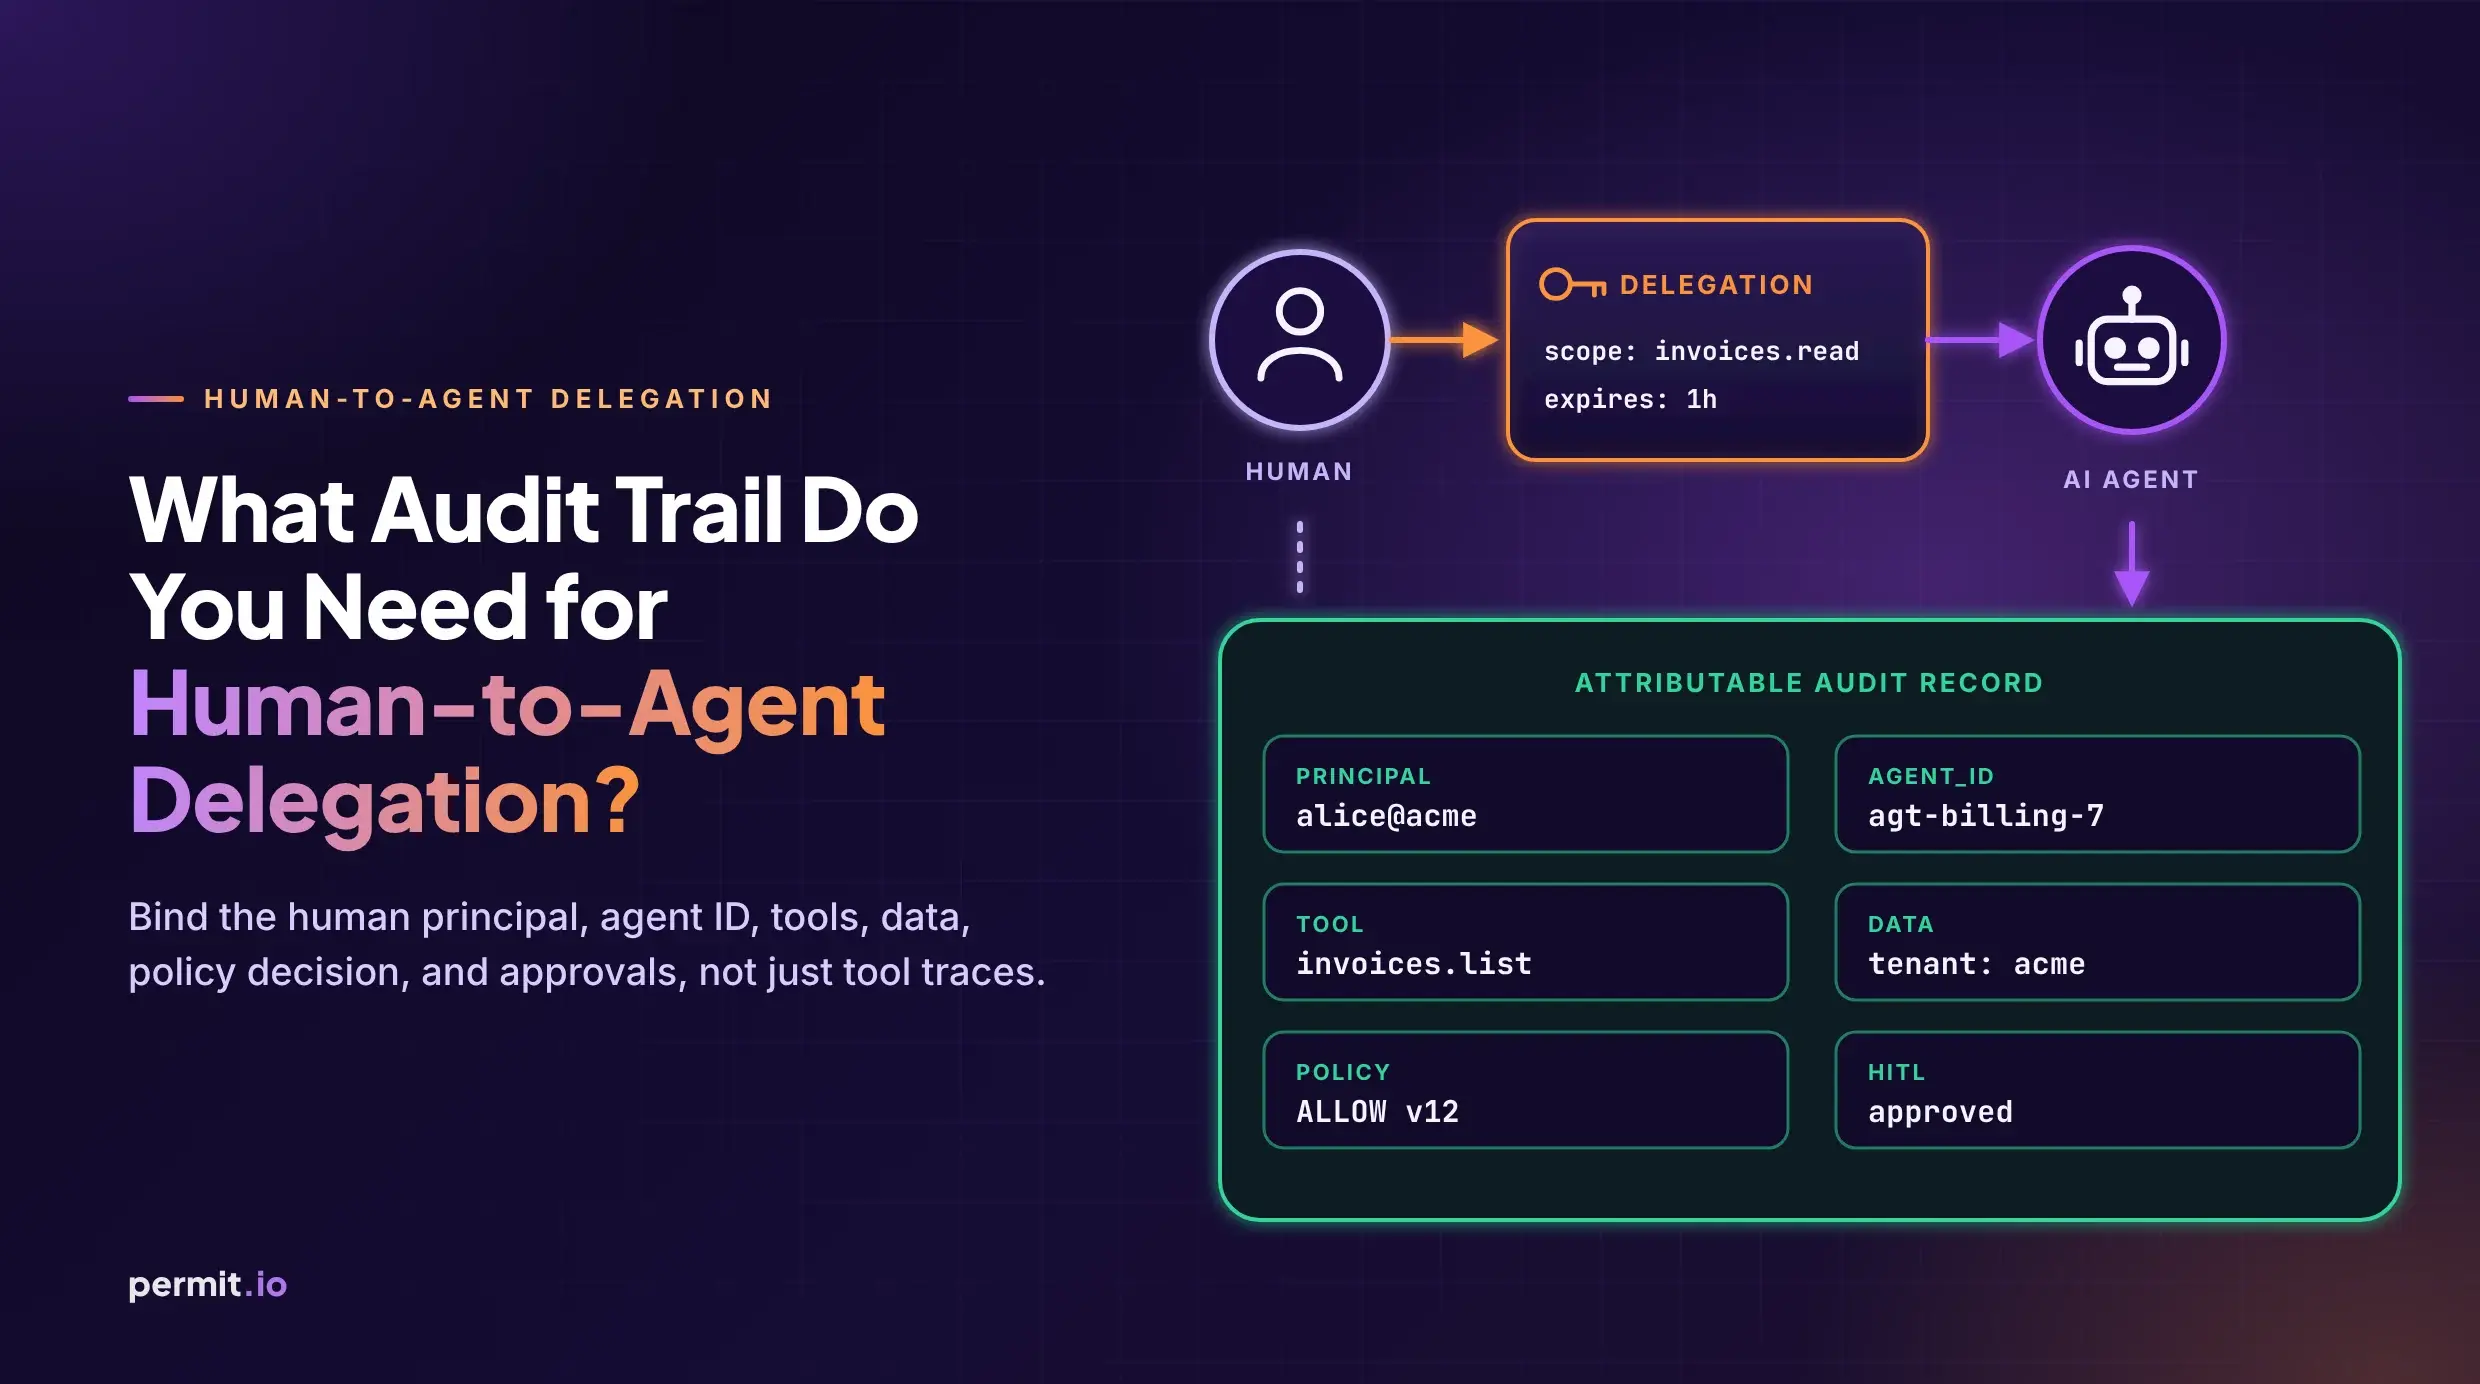
What Audit Trail Do You Need for Human-to-Agent Delegation?
For human-to-agent delegation, bind human principal, agent ID, tools, data, policy decision, and HITL, not just tool traces, into an attributable audit trail.
Read more
Or Weis
For human-to-agent delegation, bind human principal, agent ID, tools, data, policy decision, and HITL, not just tool traces, into an attributable audit trail.
Or Weis
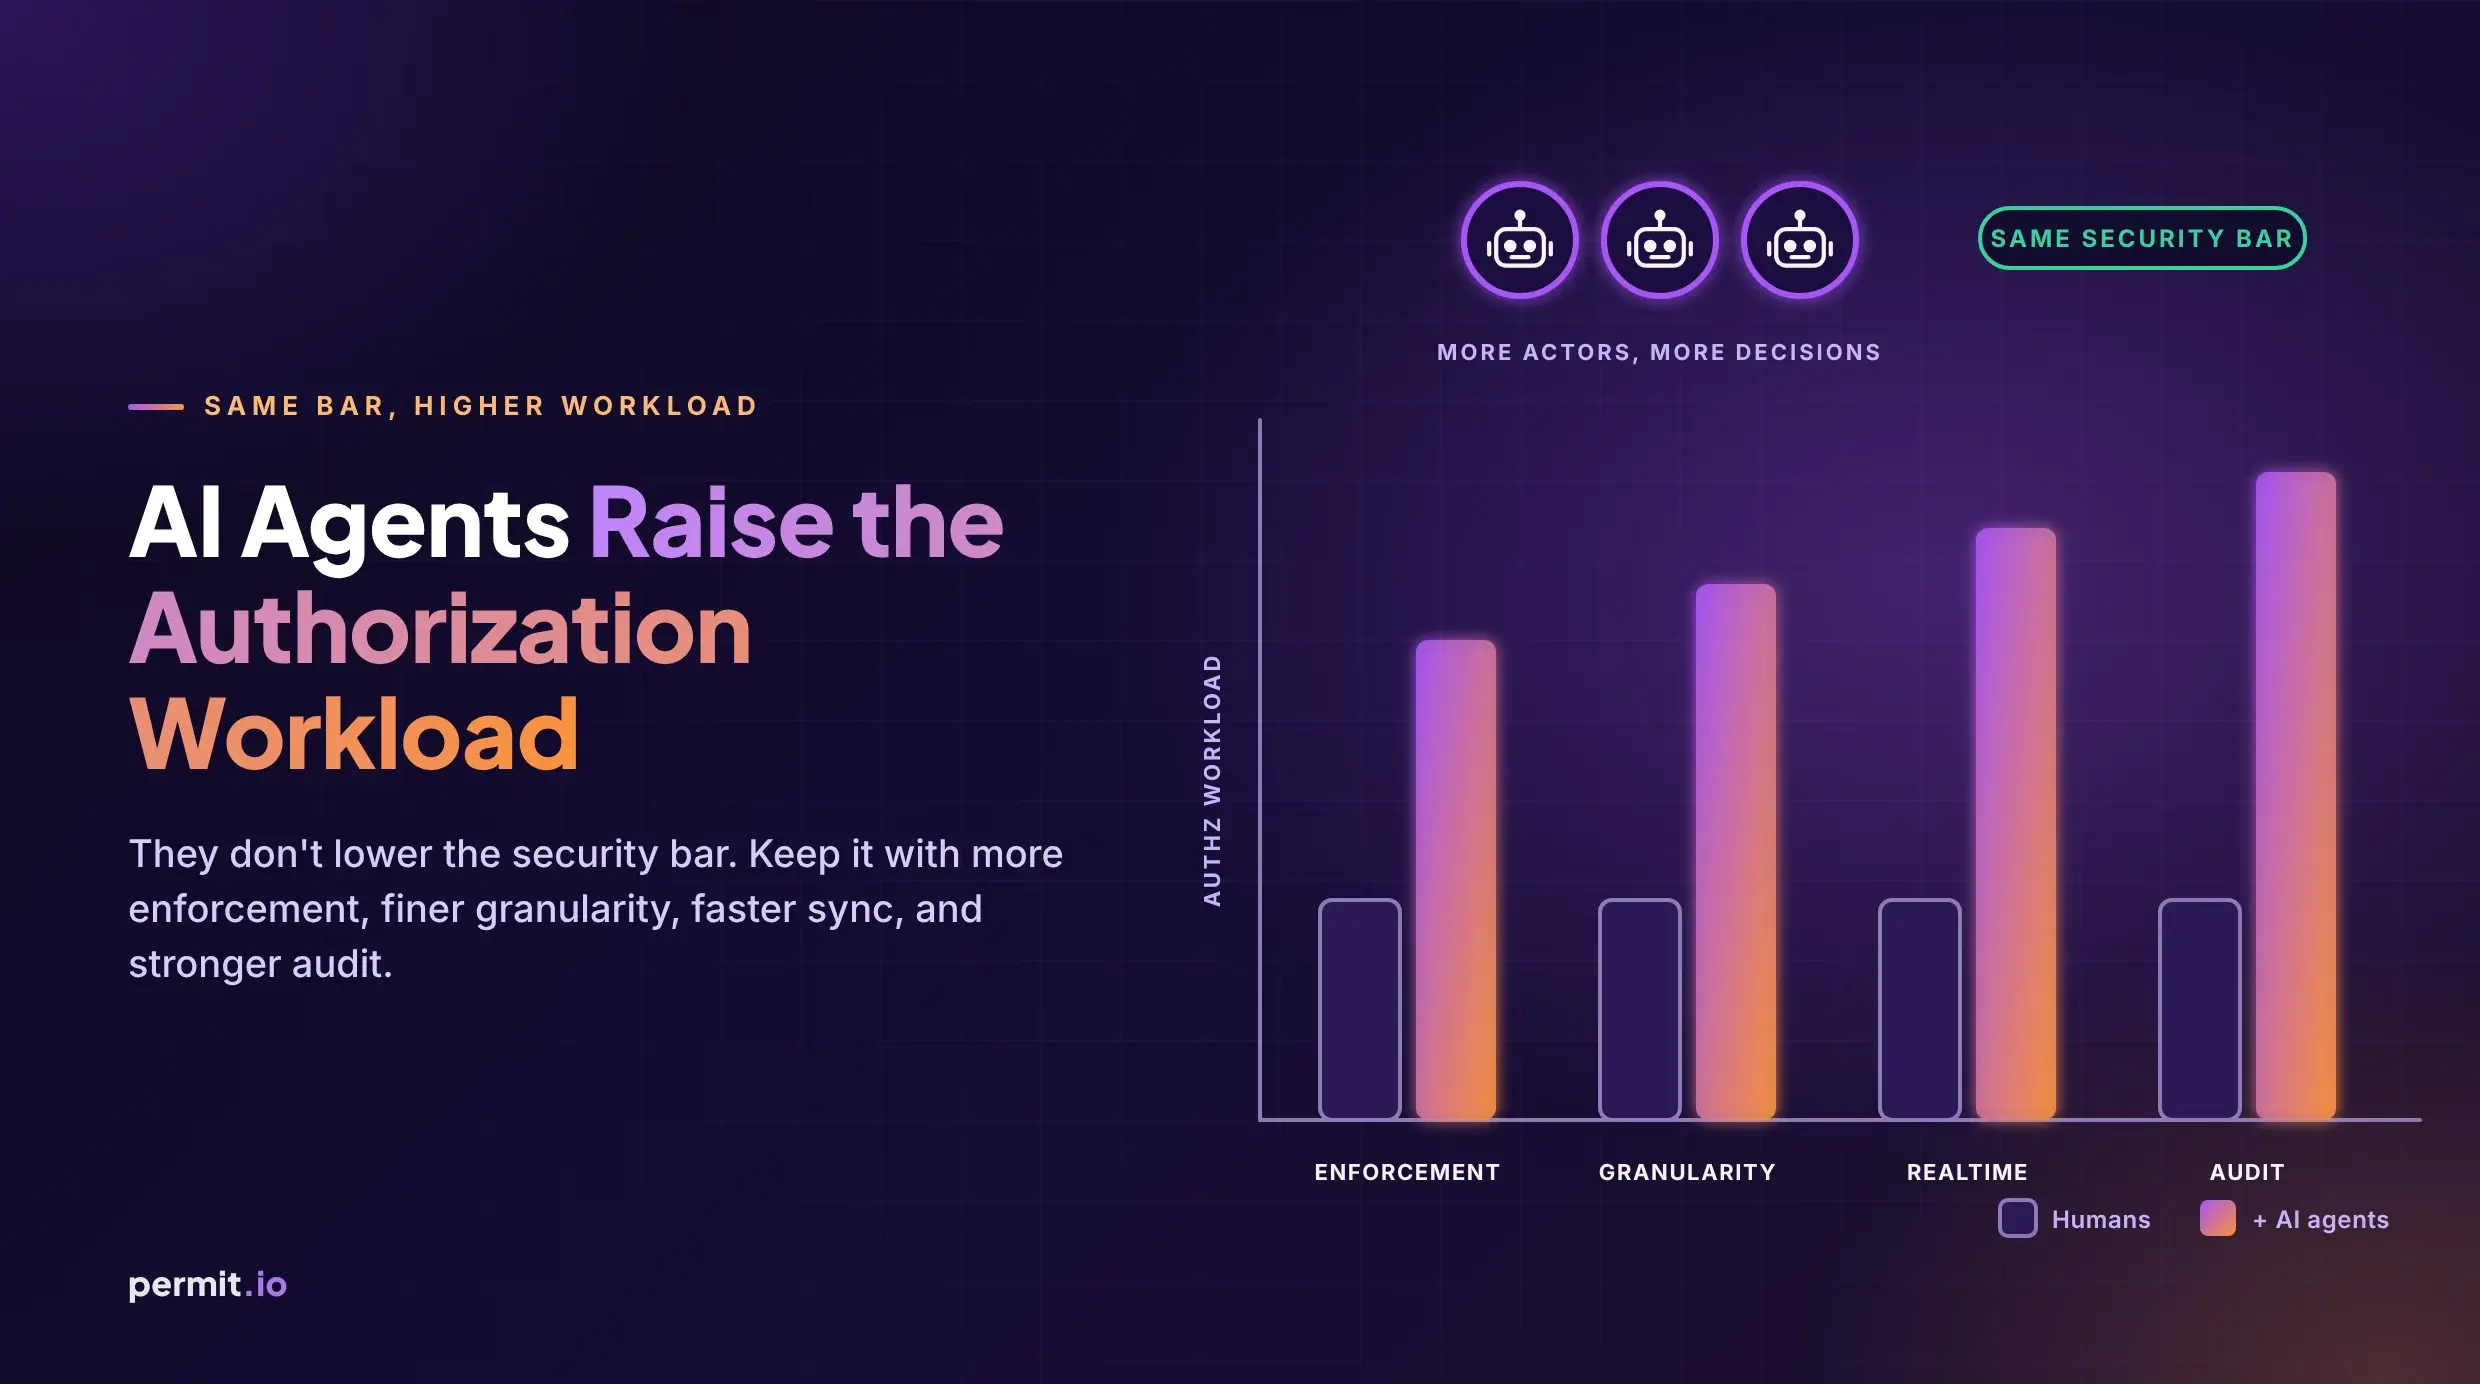
AI agents multiply the places where authorization must run. Delegation becomes a first-class part of the authorization shape: the human, the agent, the scope, the resource, conditions. Extend fine-grained authorization with per-action checks, trust ceilings, drift detection, and decision logs that explain what happened.
Or Weis
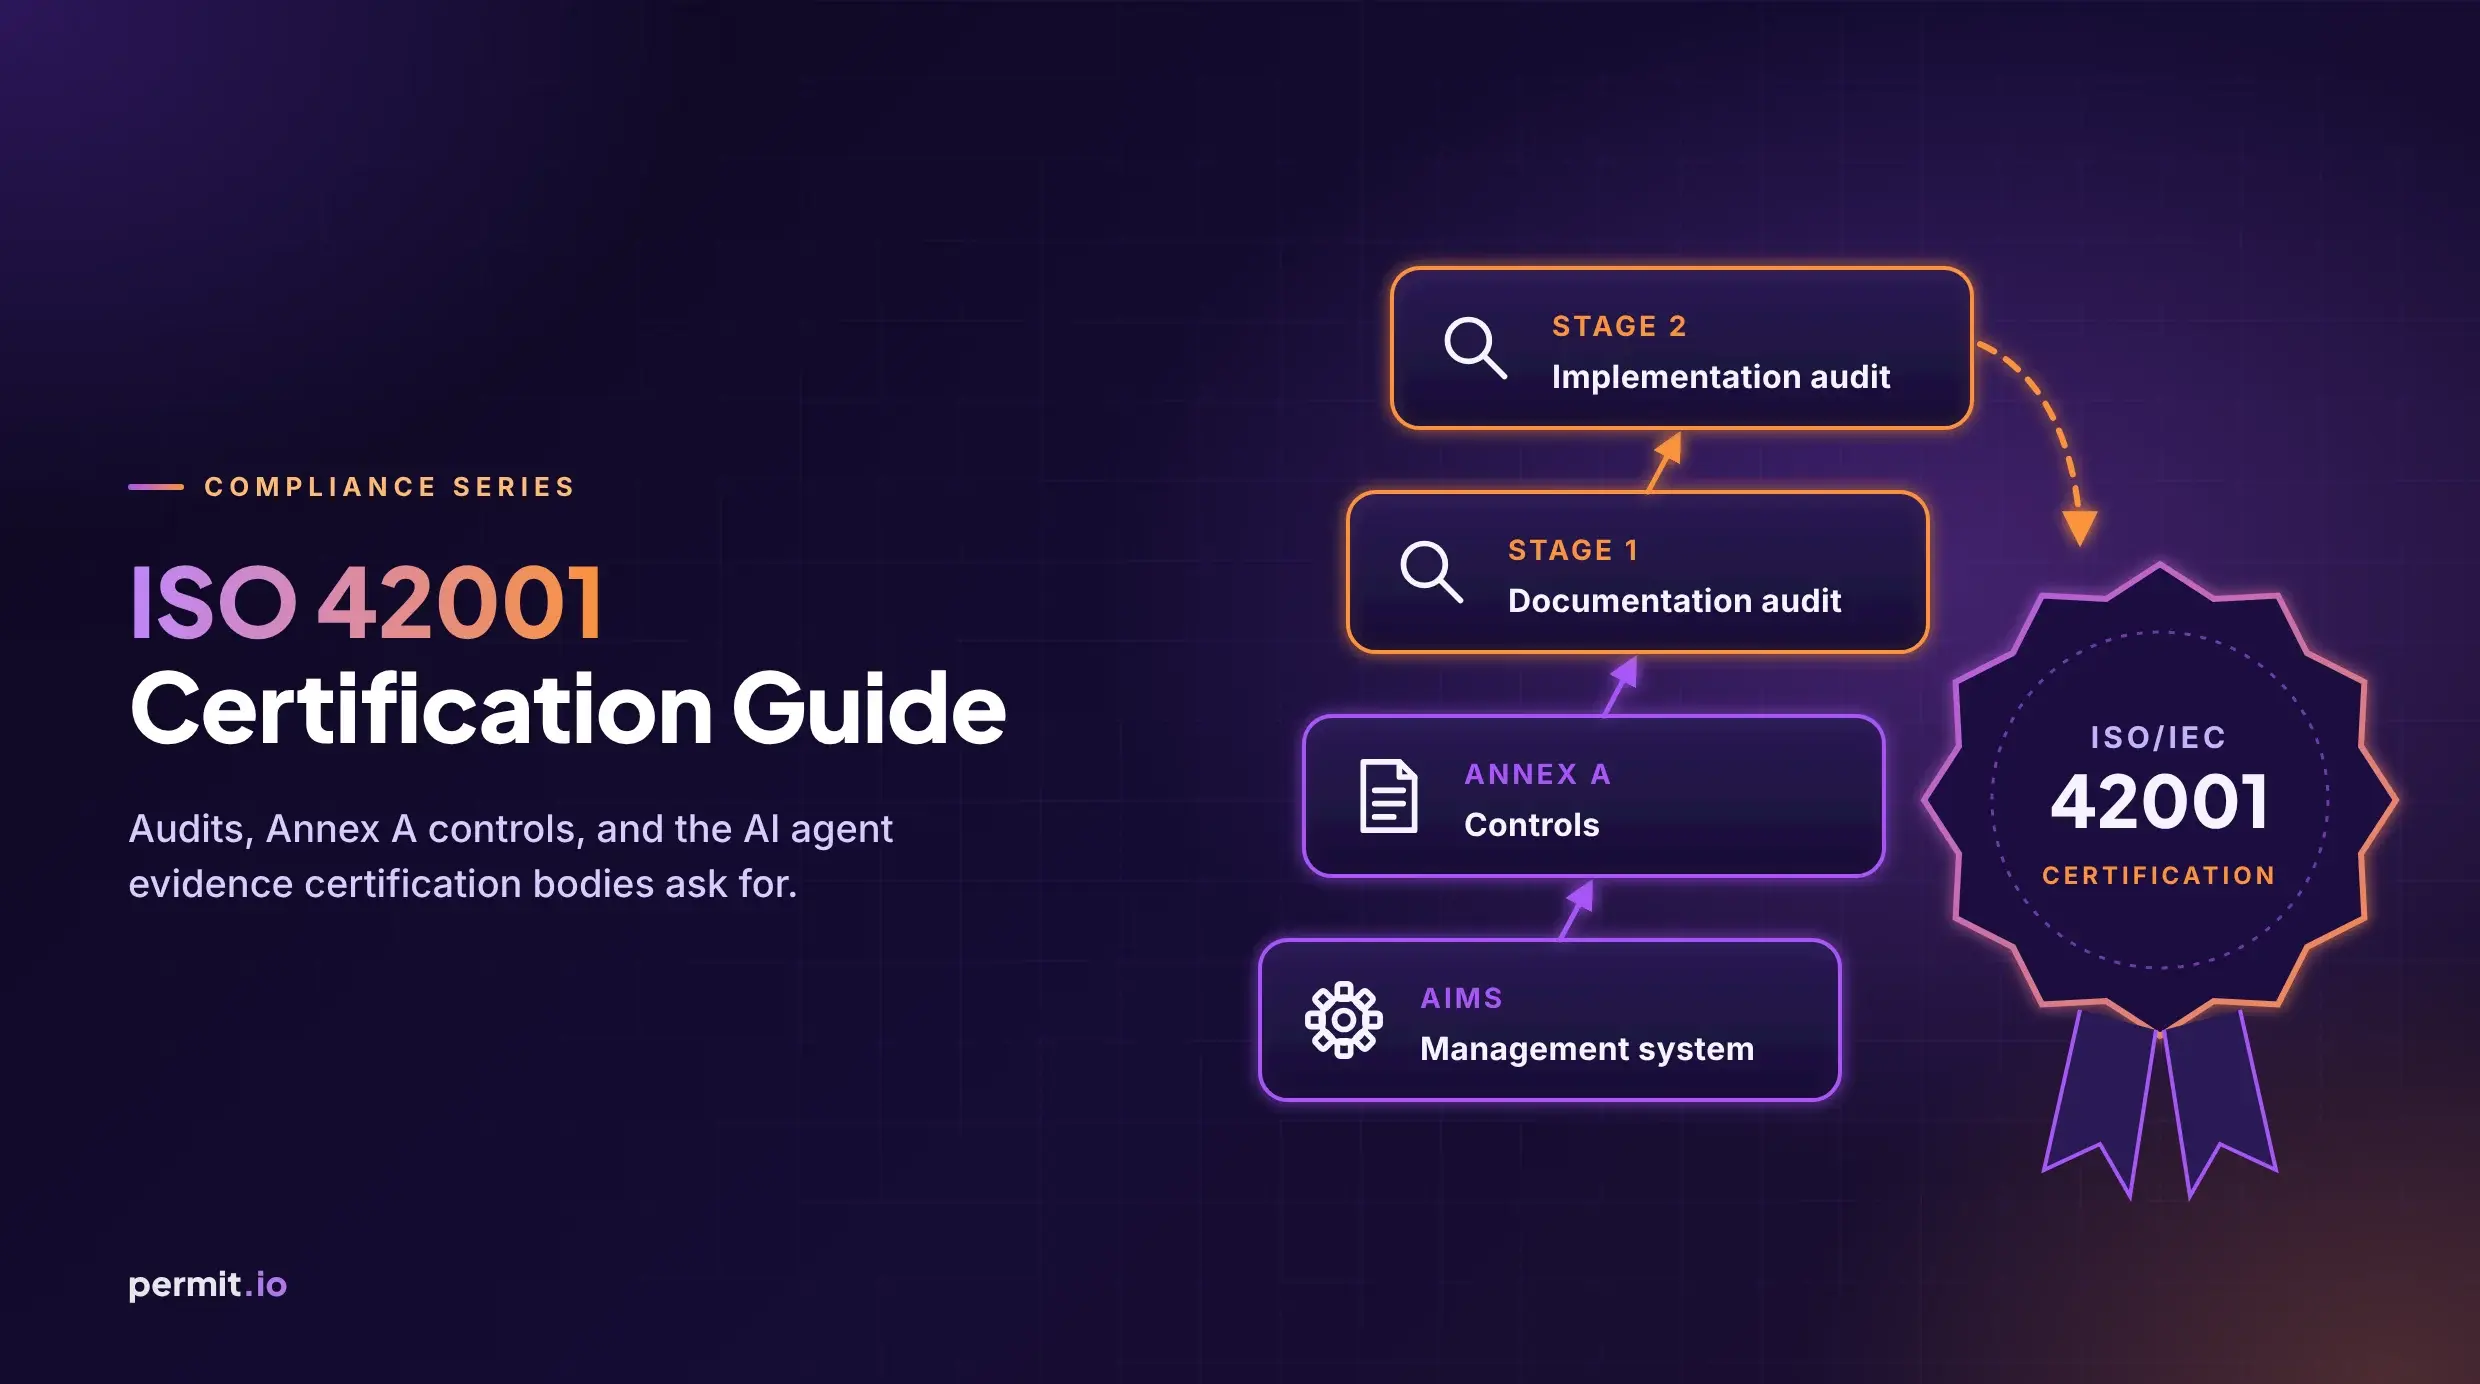
What ISO 42001 certification involves: the AI management system, accredited certification bodies, stage 1 and 2 audits, Annex A controls, and agent evidence.
Or Weis
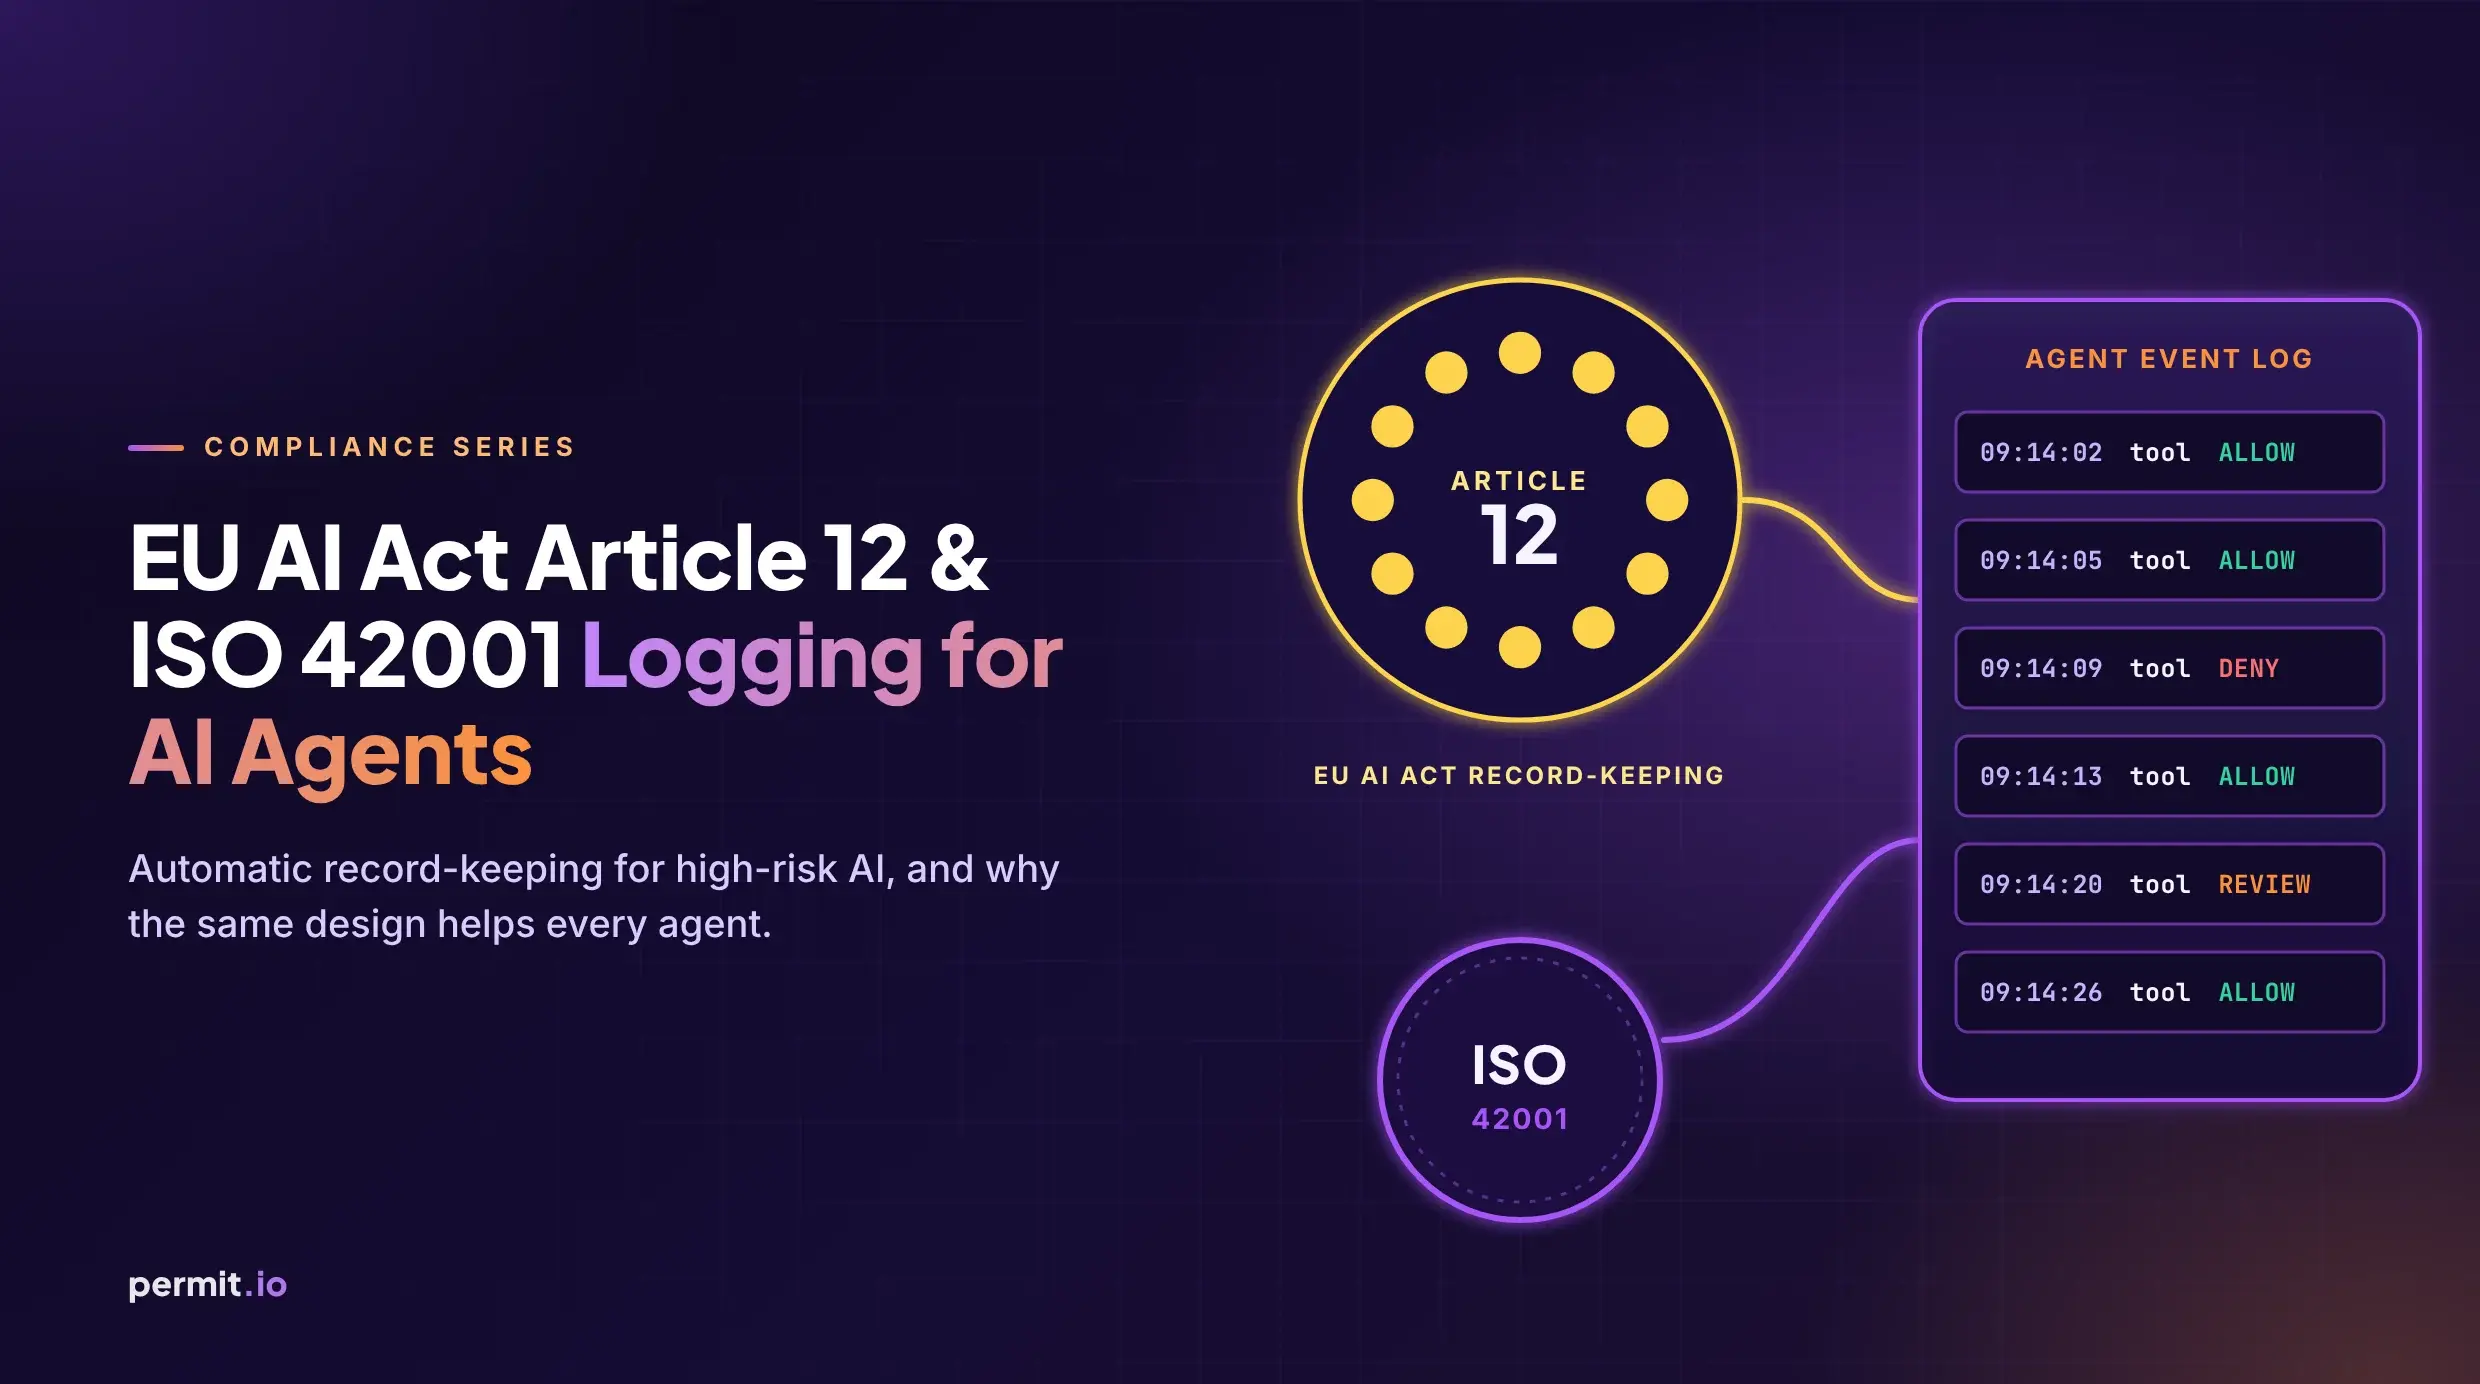
EU AI Act Article 12 record-keeping for high-risk AI, plus ISO 42001 logging, and why that design still helps non-high-risk agents.
Or Weis
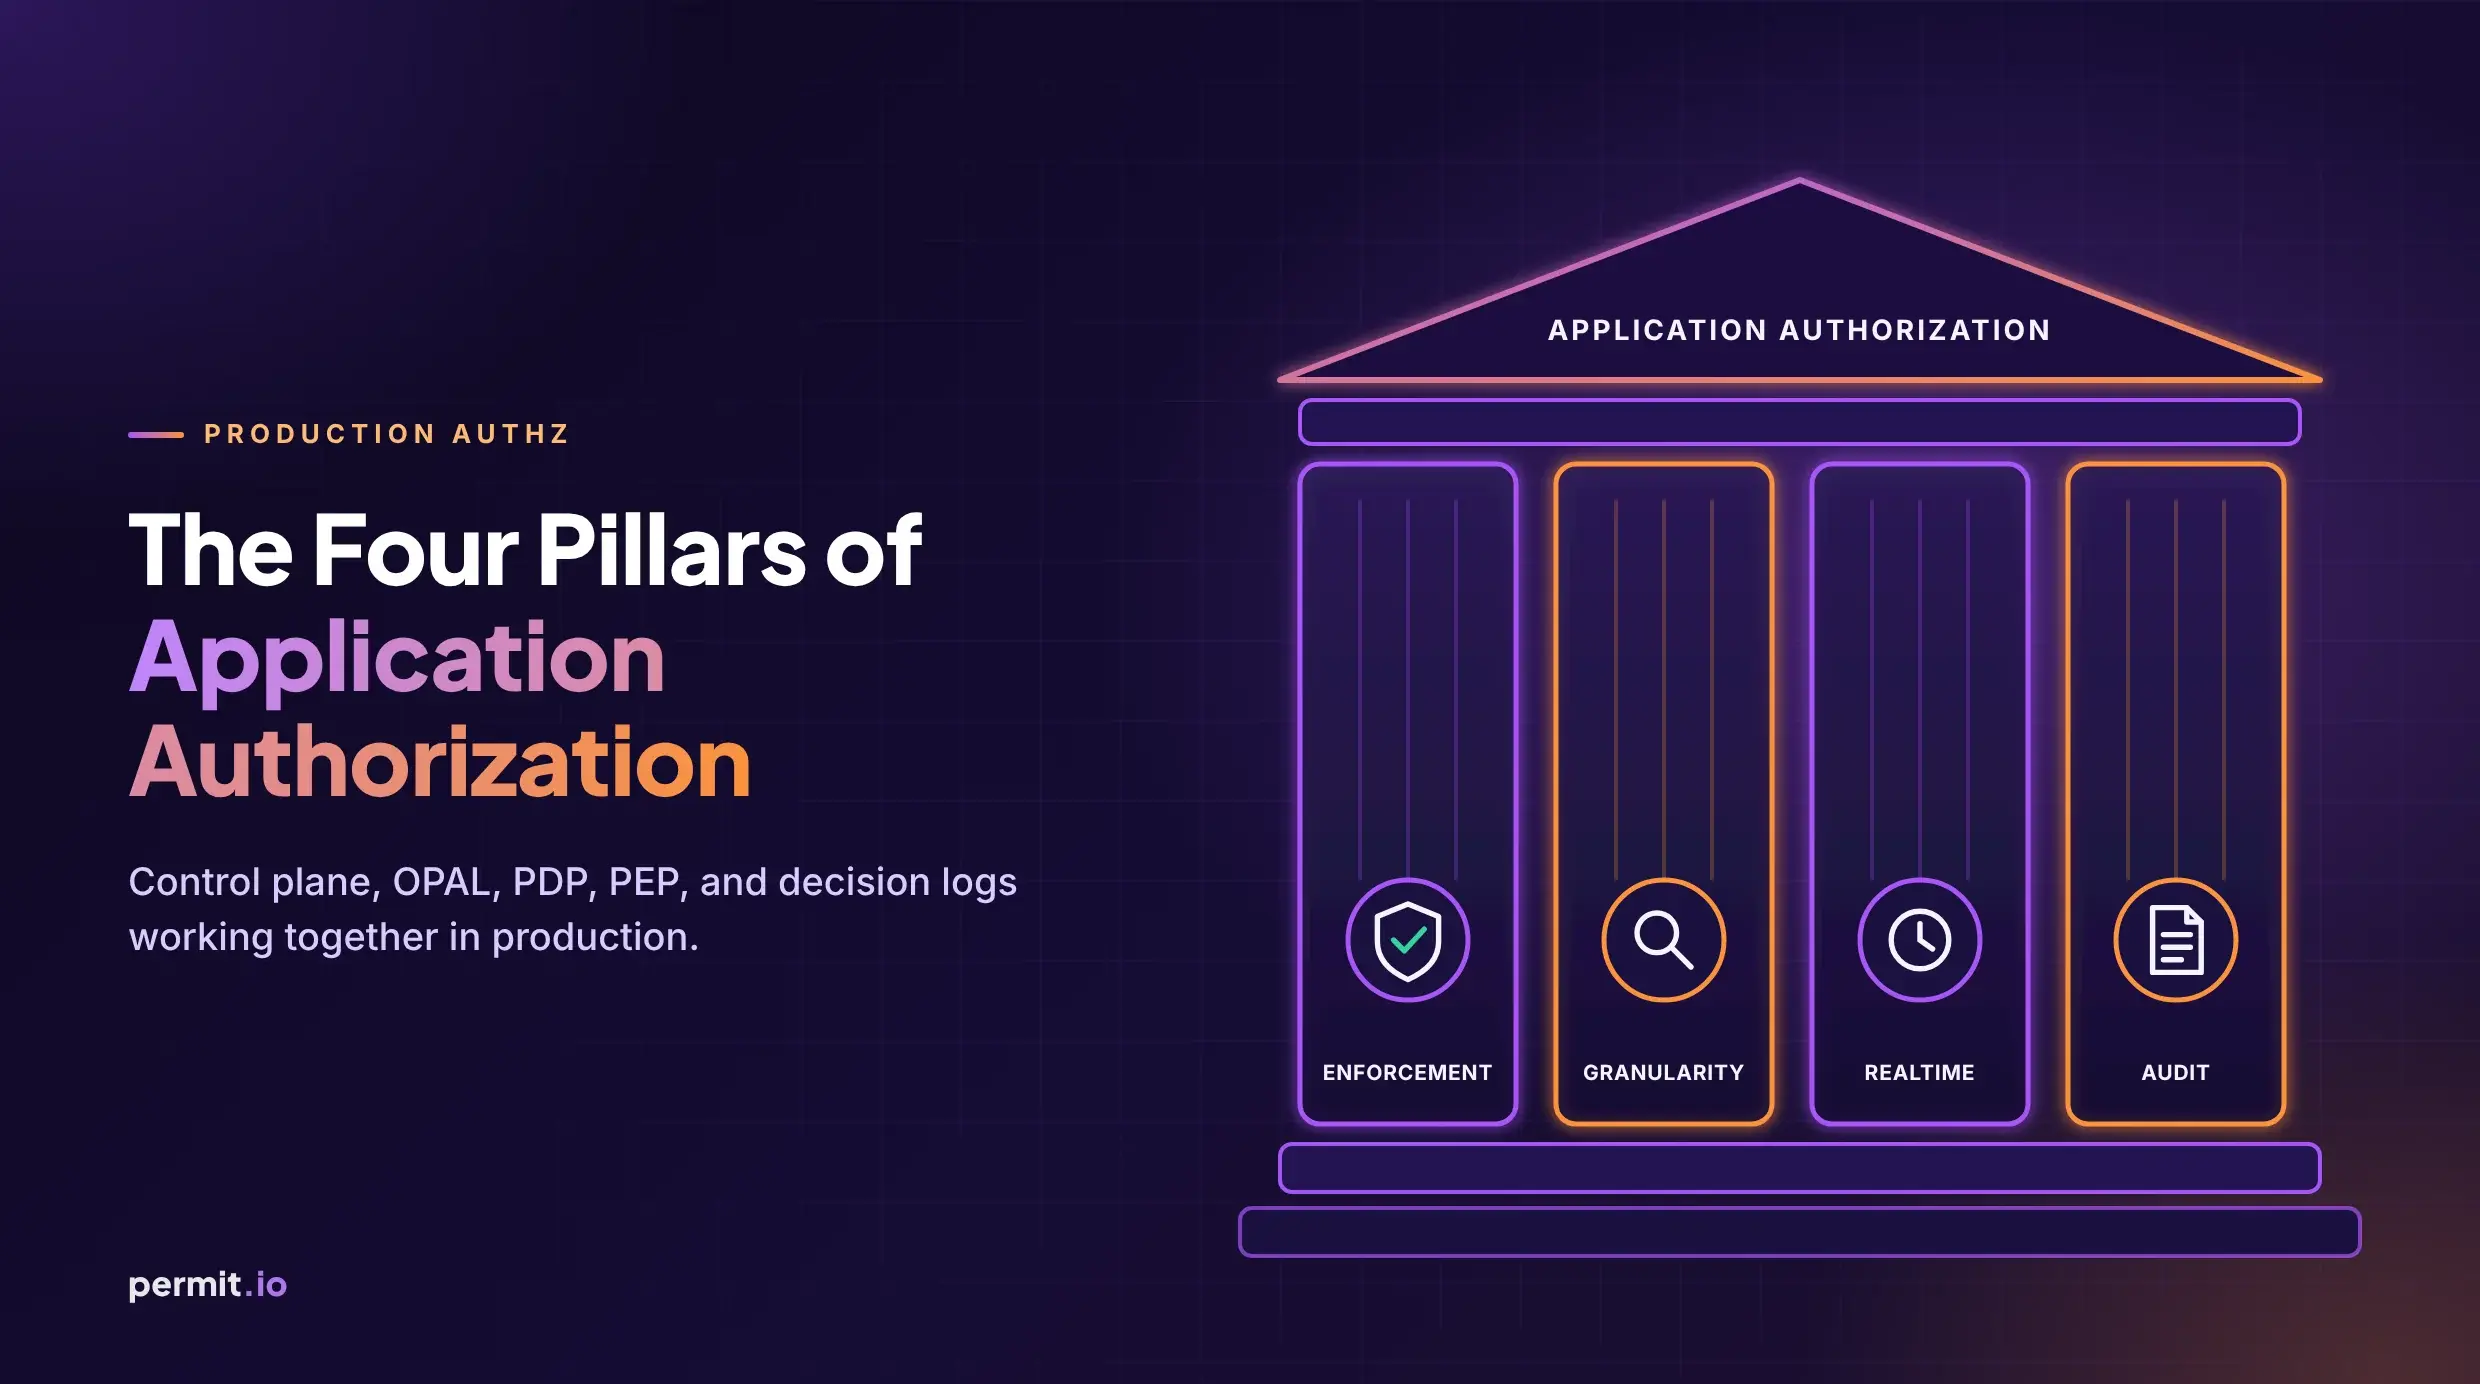
Production AuthZ needs four pillars: enforce at every sensitive action, fine grain, realtime revoke/sync, and auditable decisions. Control plane → OPAL → PDP → PEP → logs is the architecture that makes them work together.
Or Weis
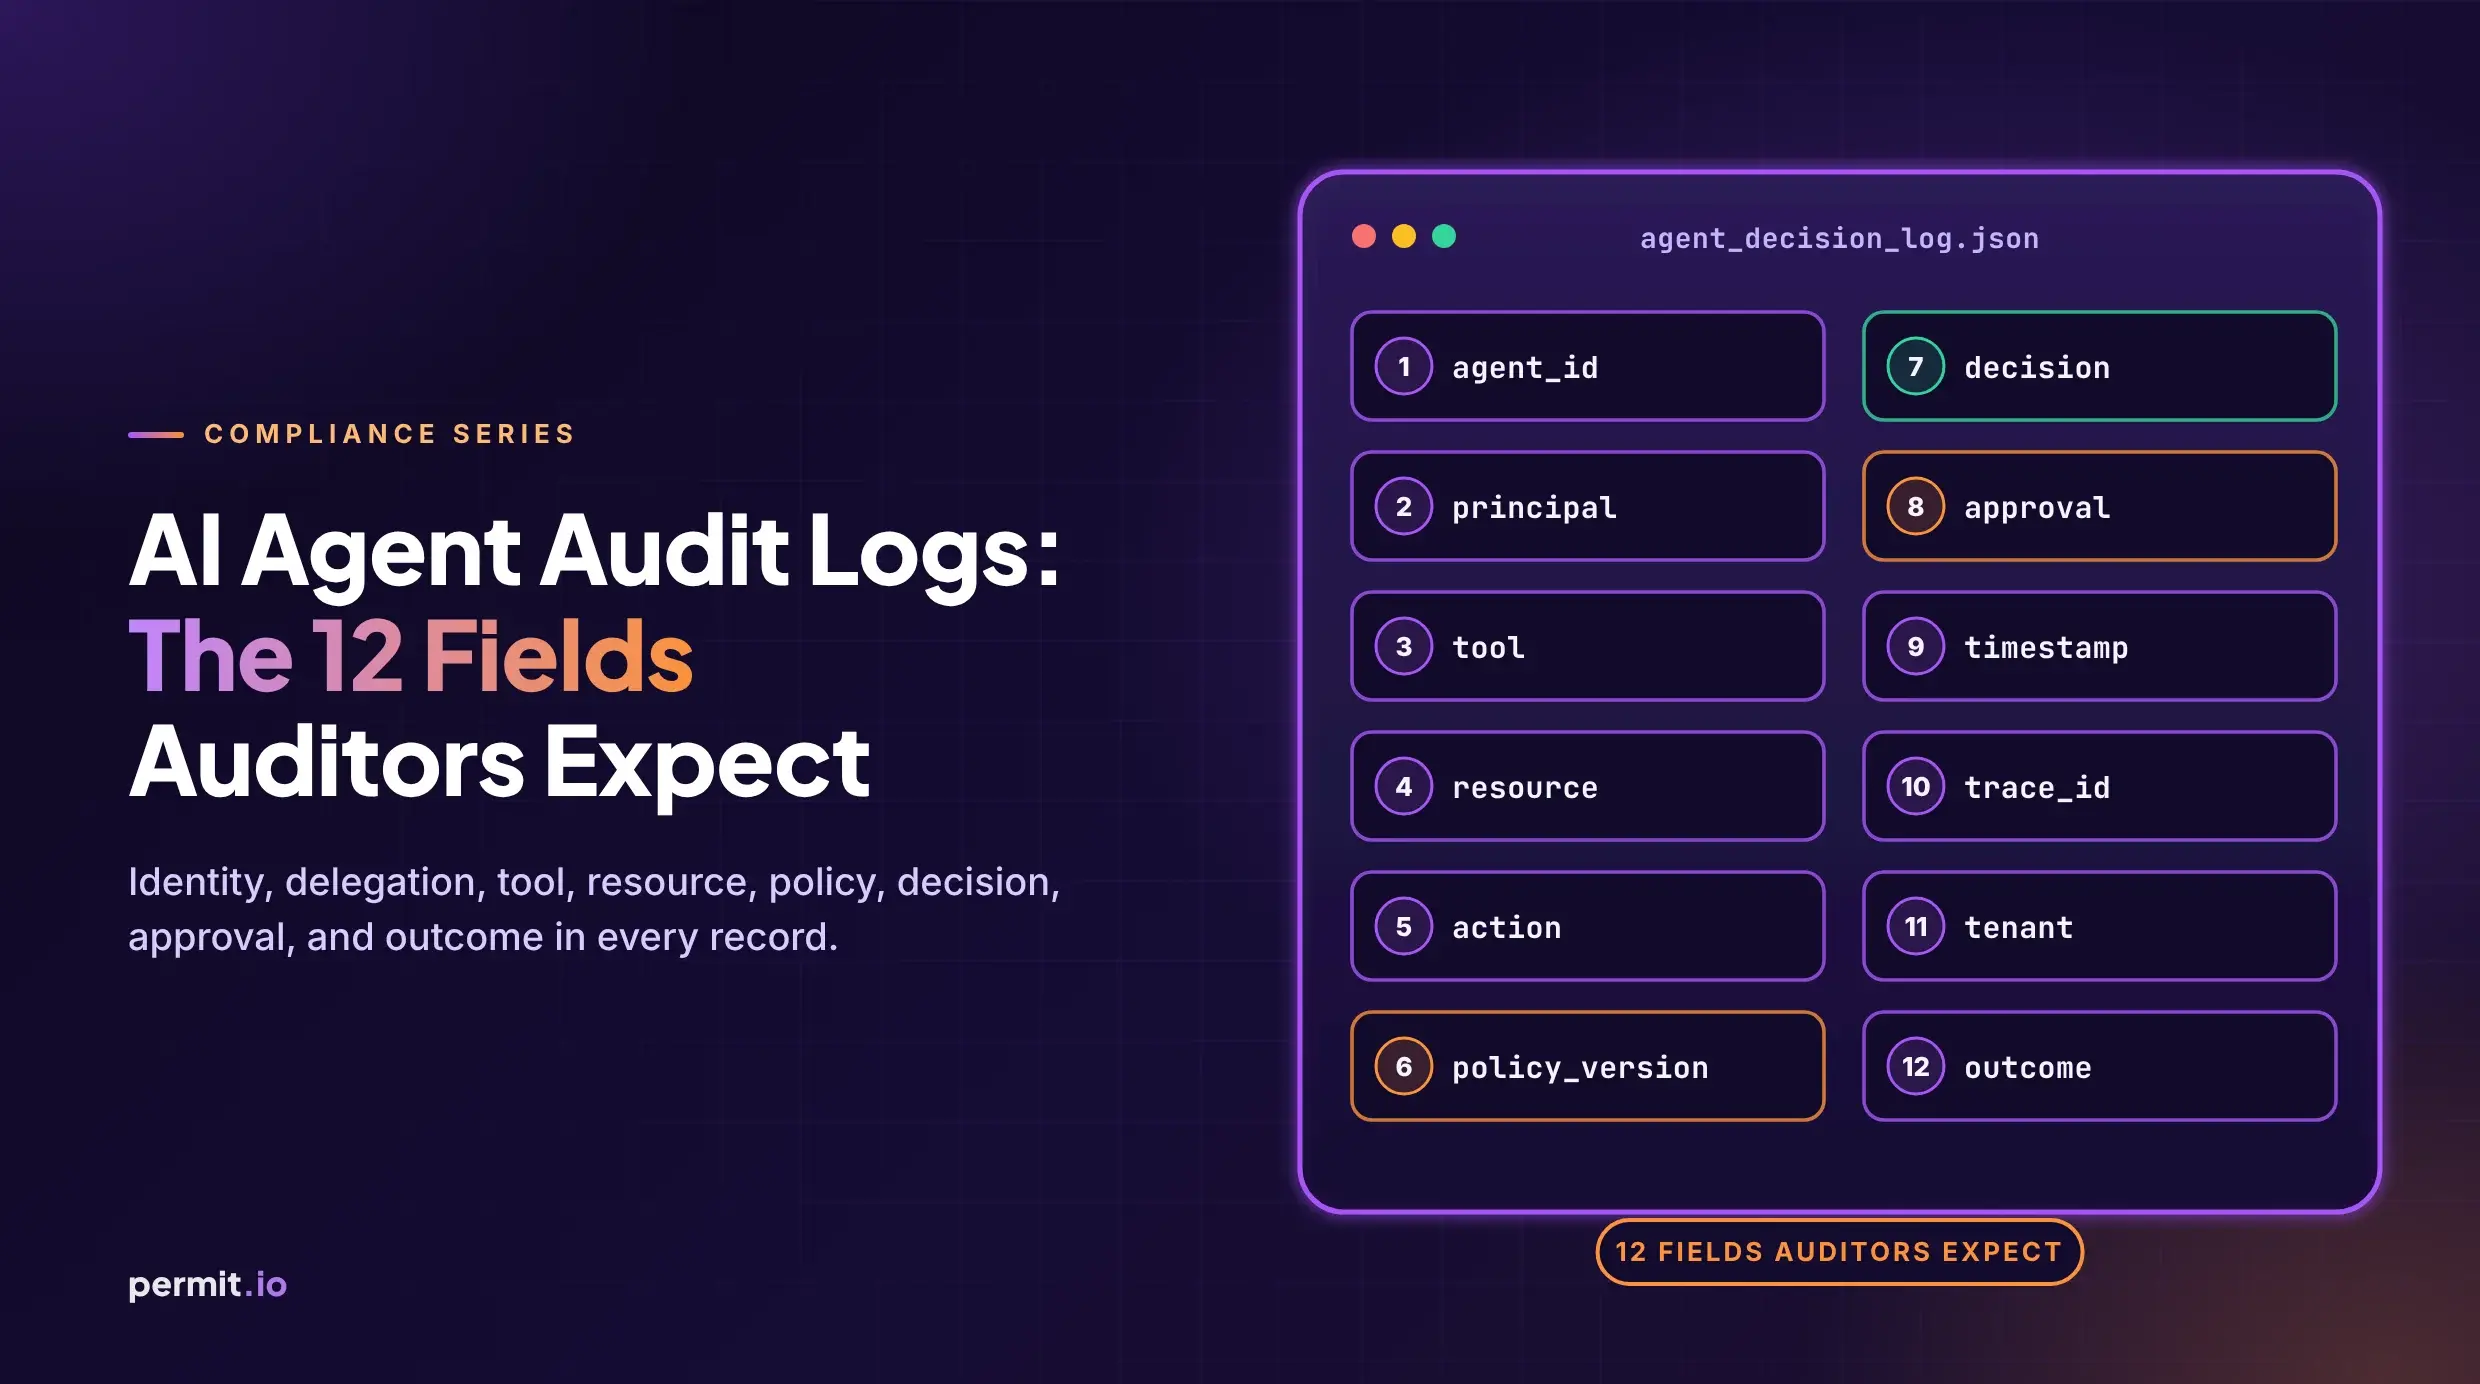
AI agent audit logs need about twelve fields: identity, delegation, tool, resource, policy, decision, HITL, and outcome.
Or Weis
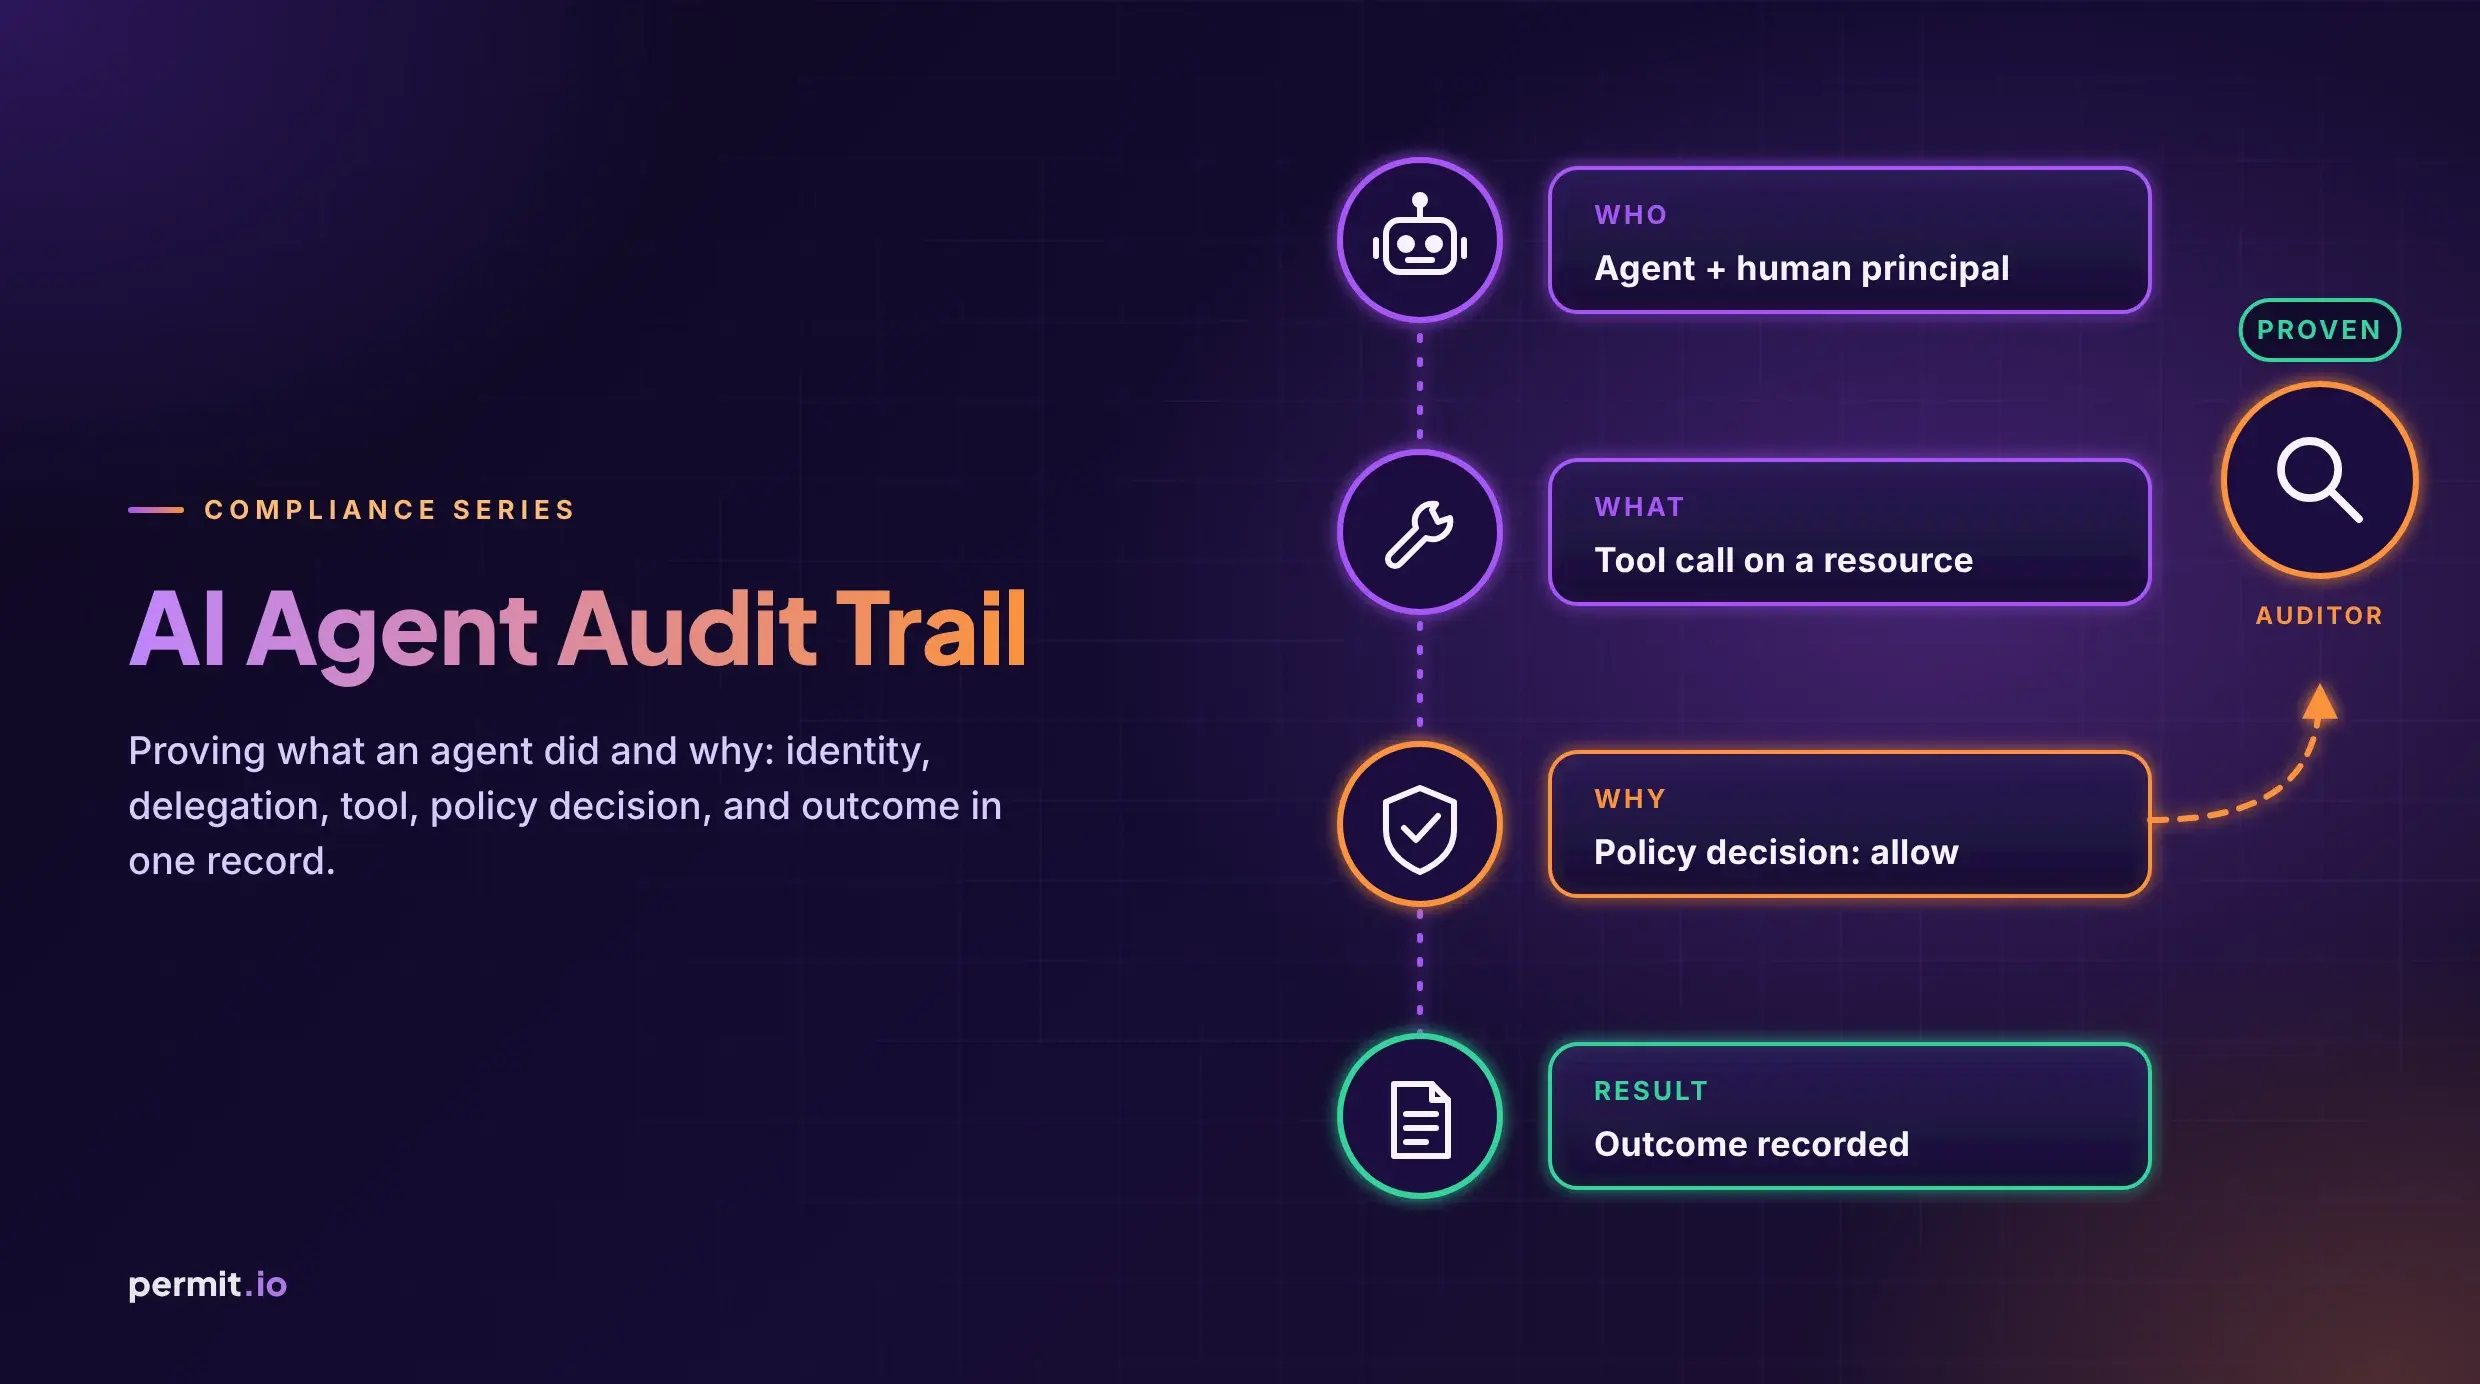
An AI agent audit trail binds identity, delegation, tool, resource, policy, allow/deny, HITL, and outcome. Tool traces are not enough.
Or Weis
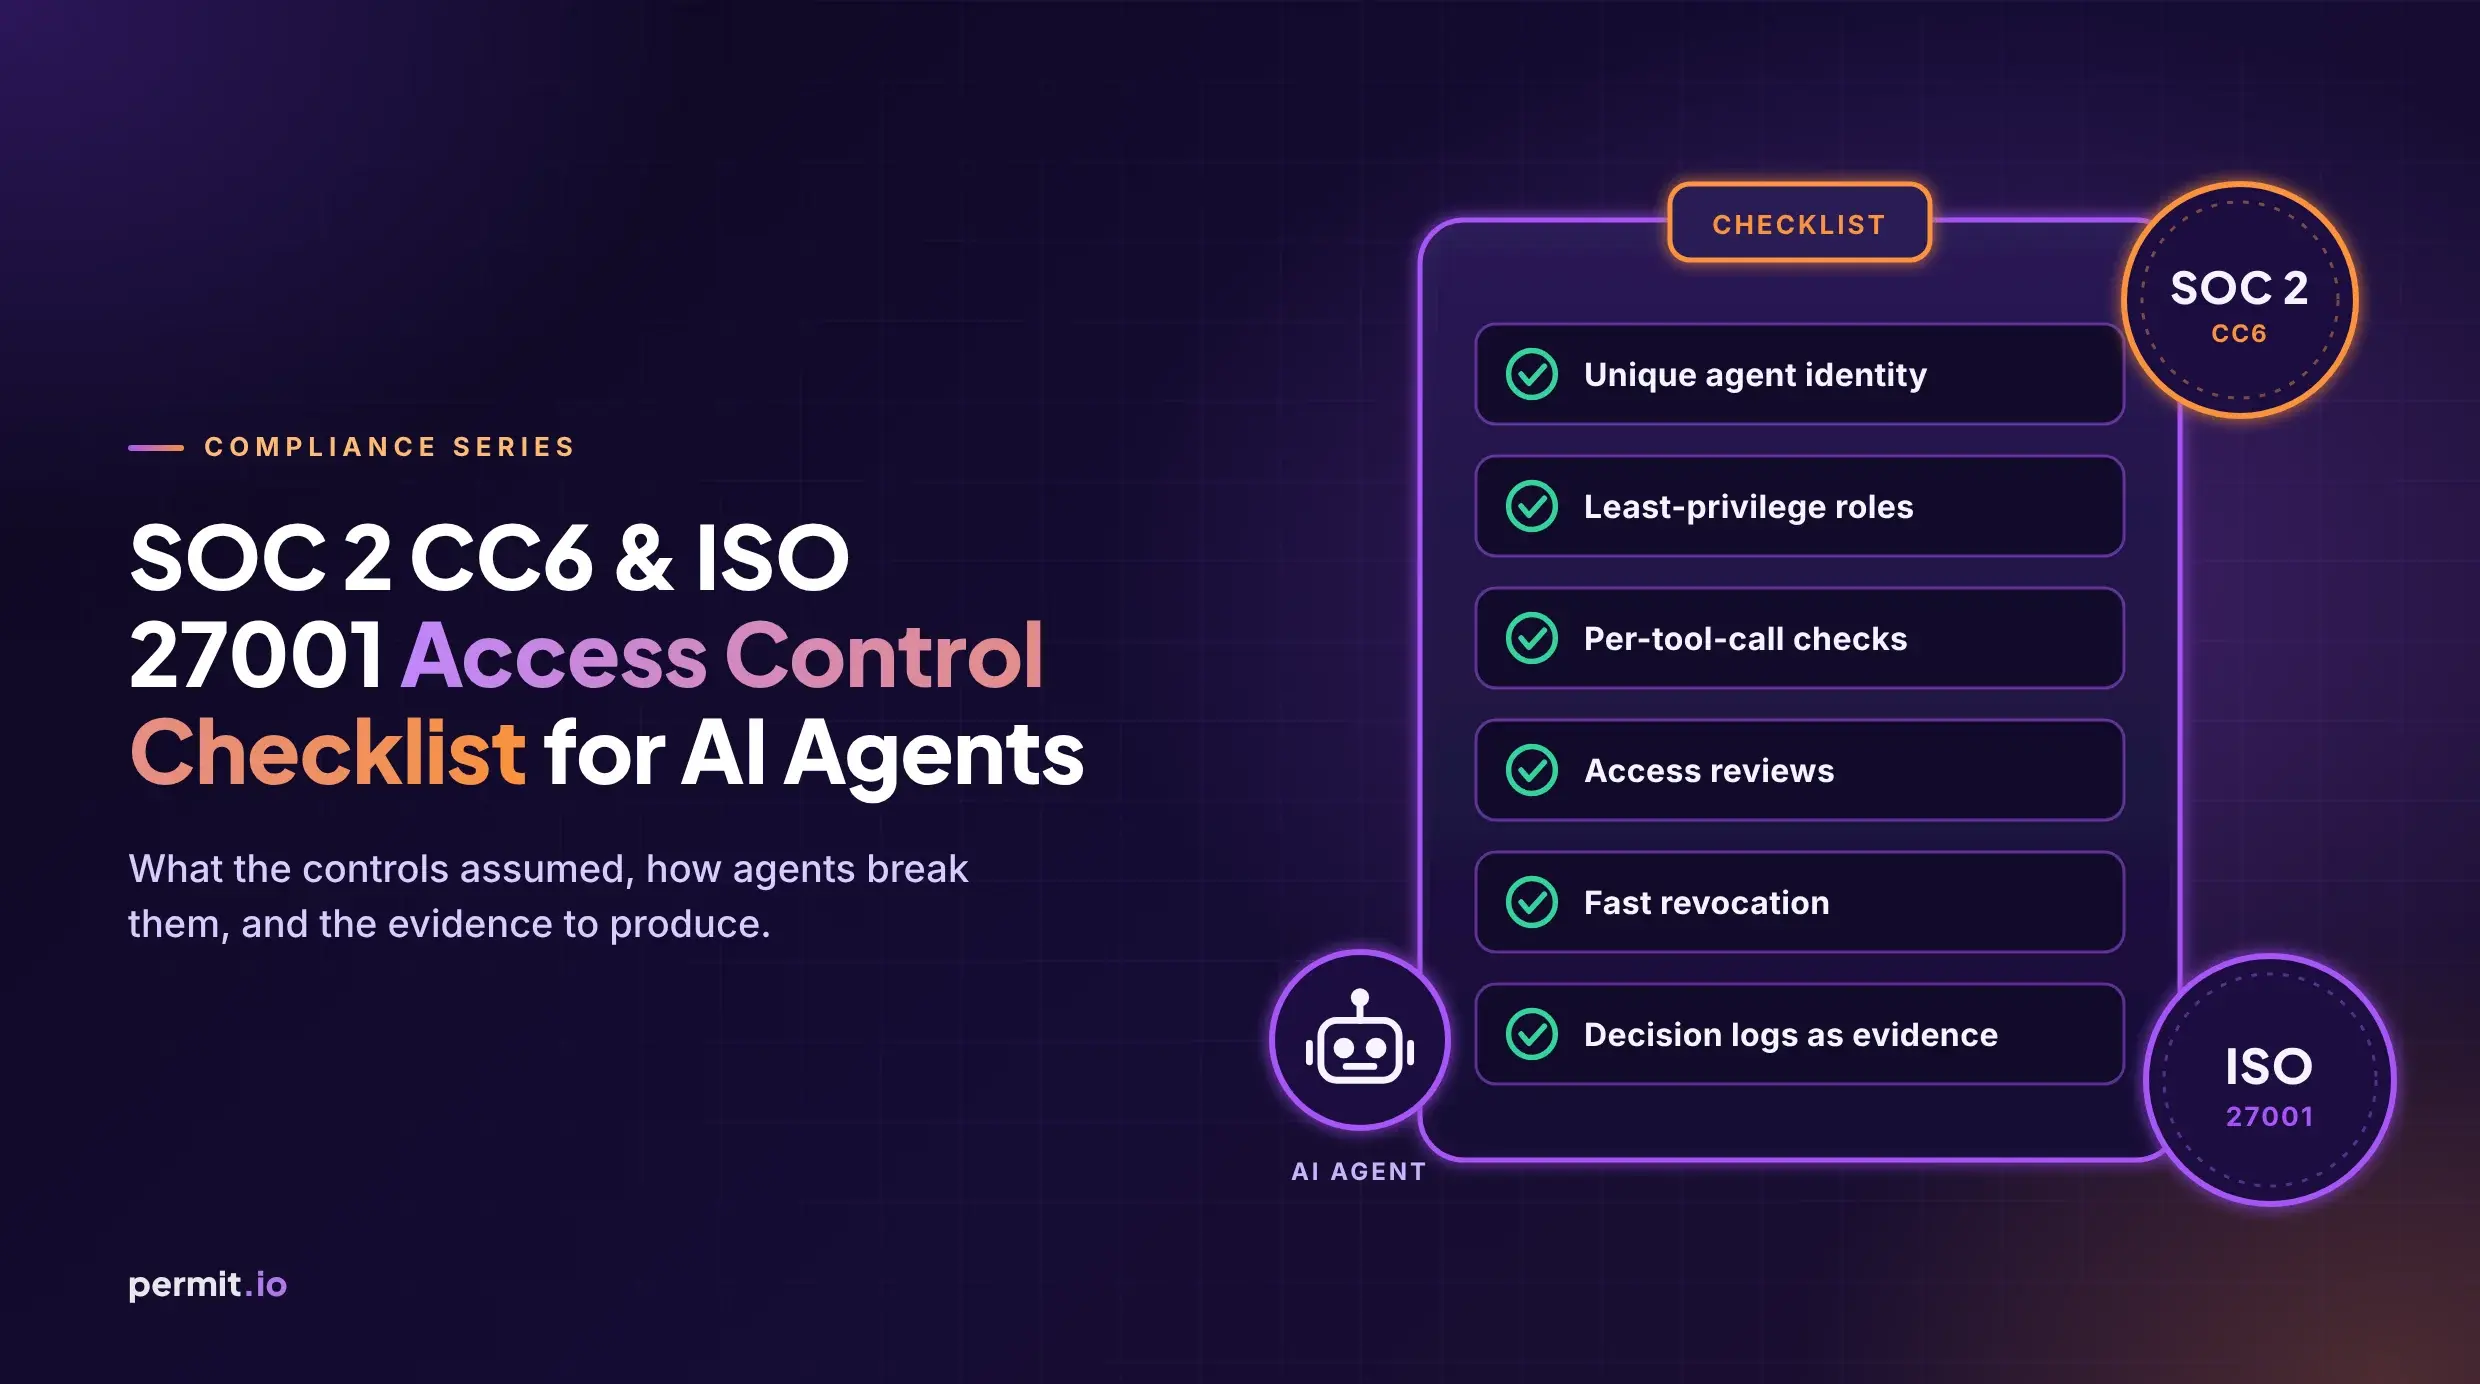
SOC 2 CC6 and ISO 27001 access control checklist for AI agents: what controls assumed, how agents break them, evidence to produce.
Or Weis
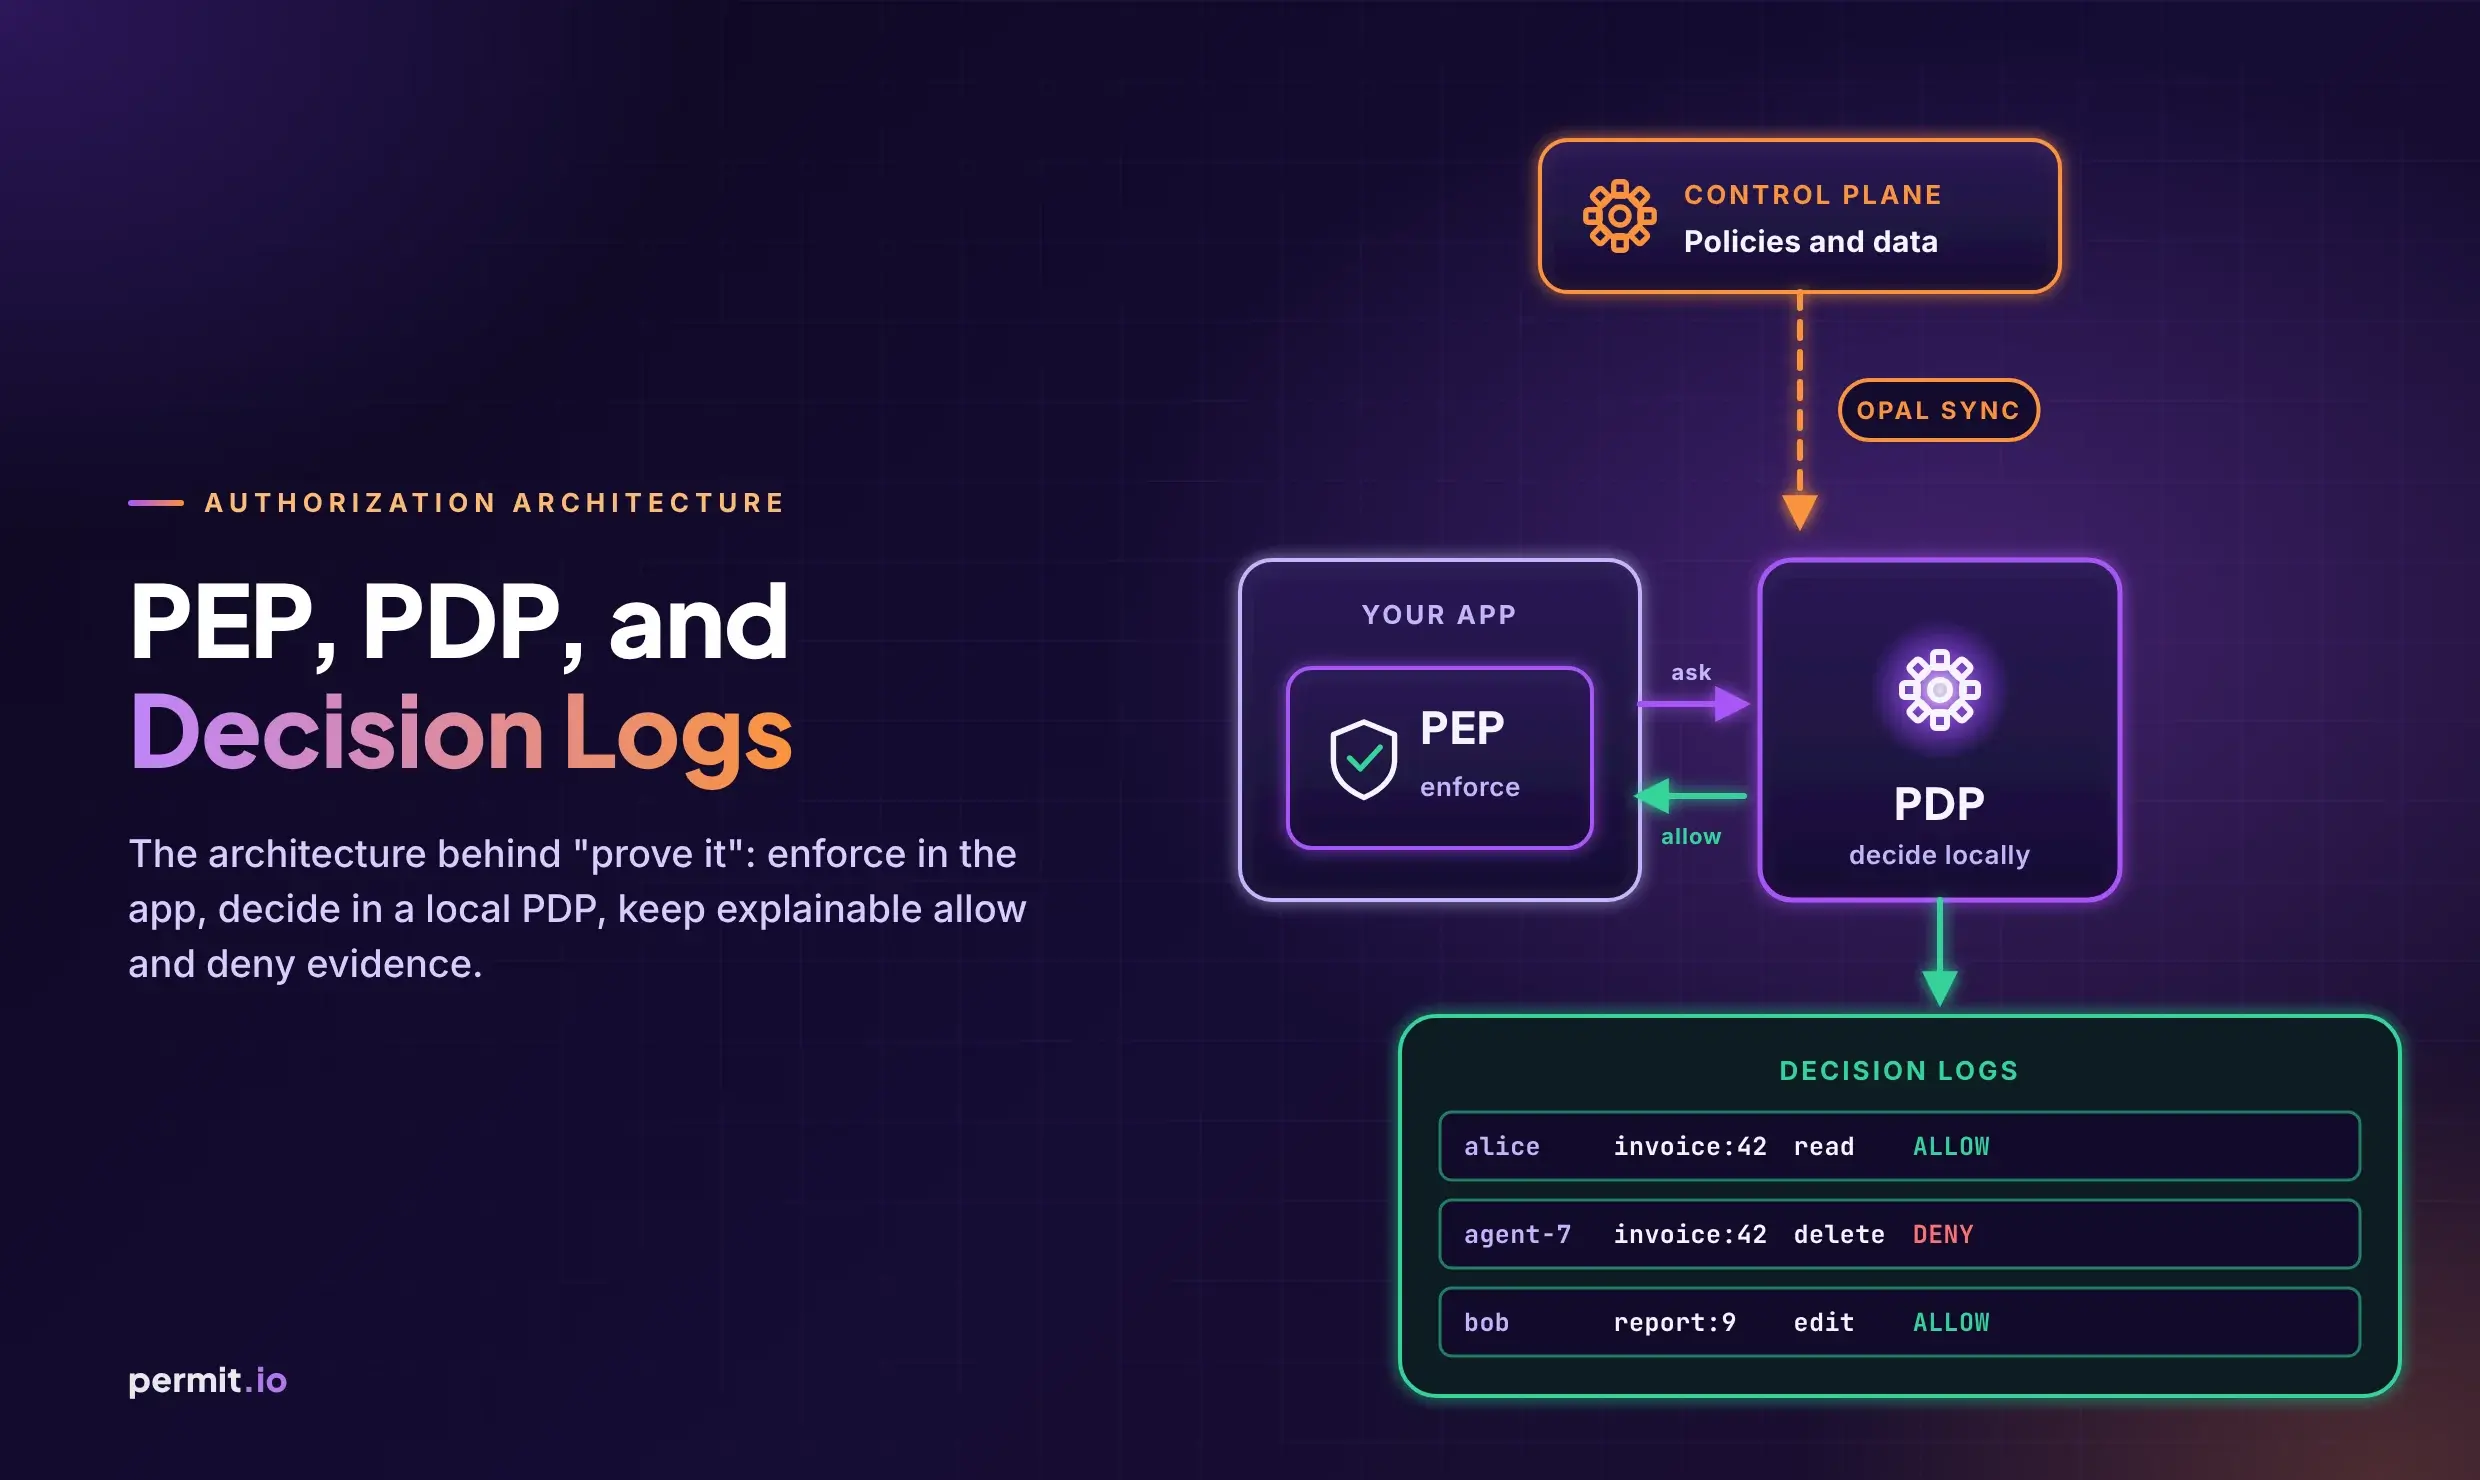
Regulators’ “prove it” maps to PEP + PDP + decision logs: enforce in the app, decide in a local PDP synced by OPAL, and keep explainable allow/deny evidence.
Or Weis
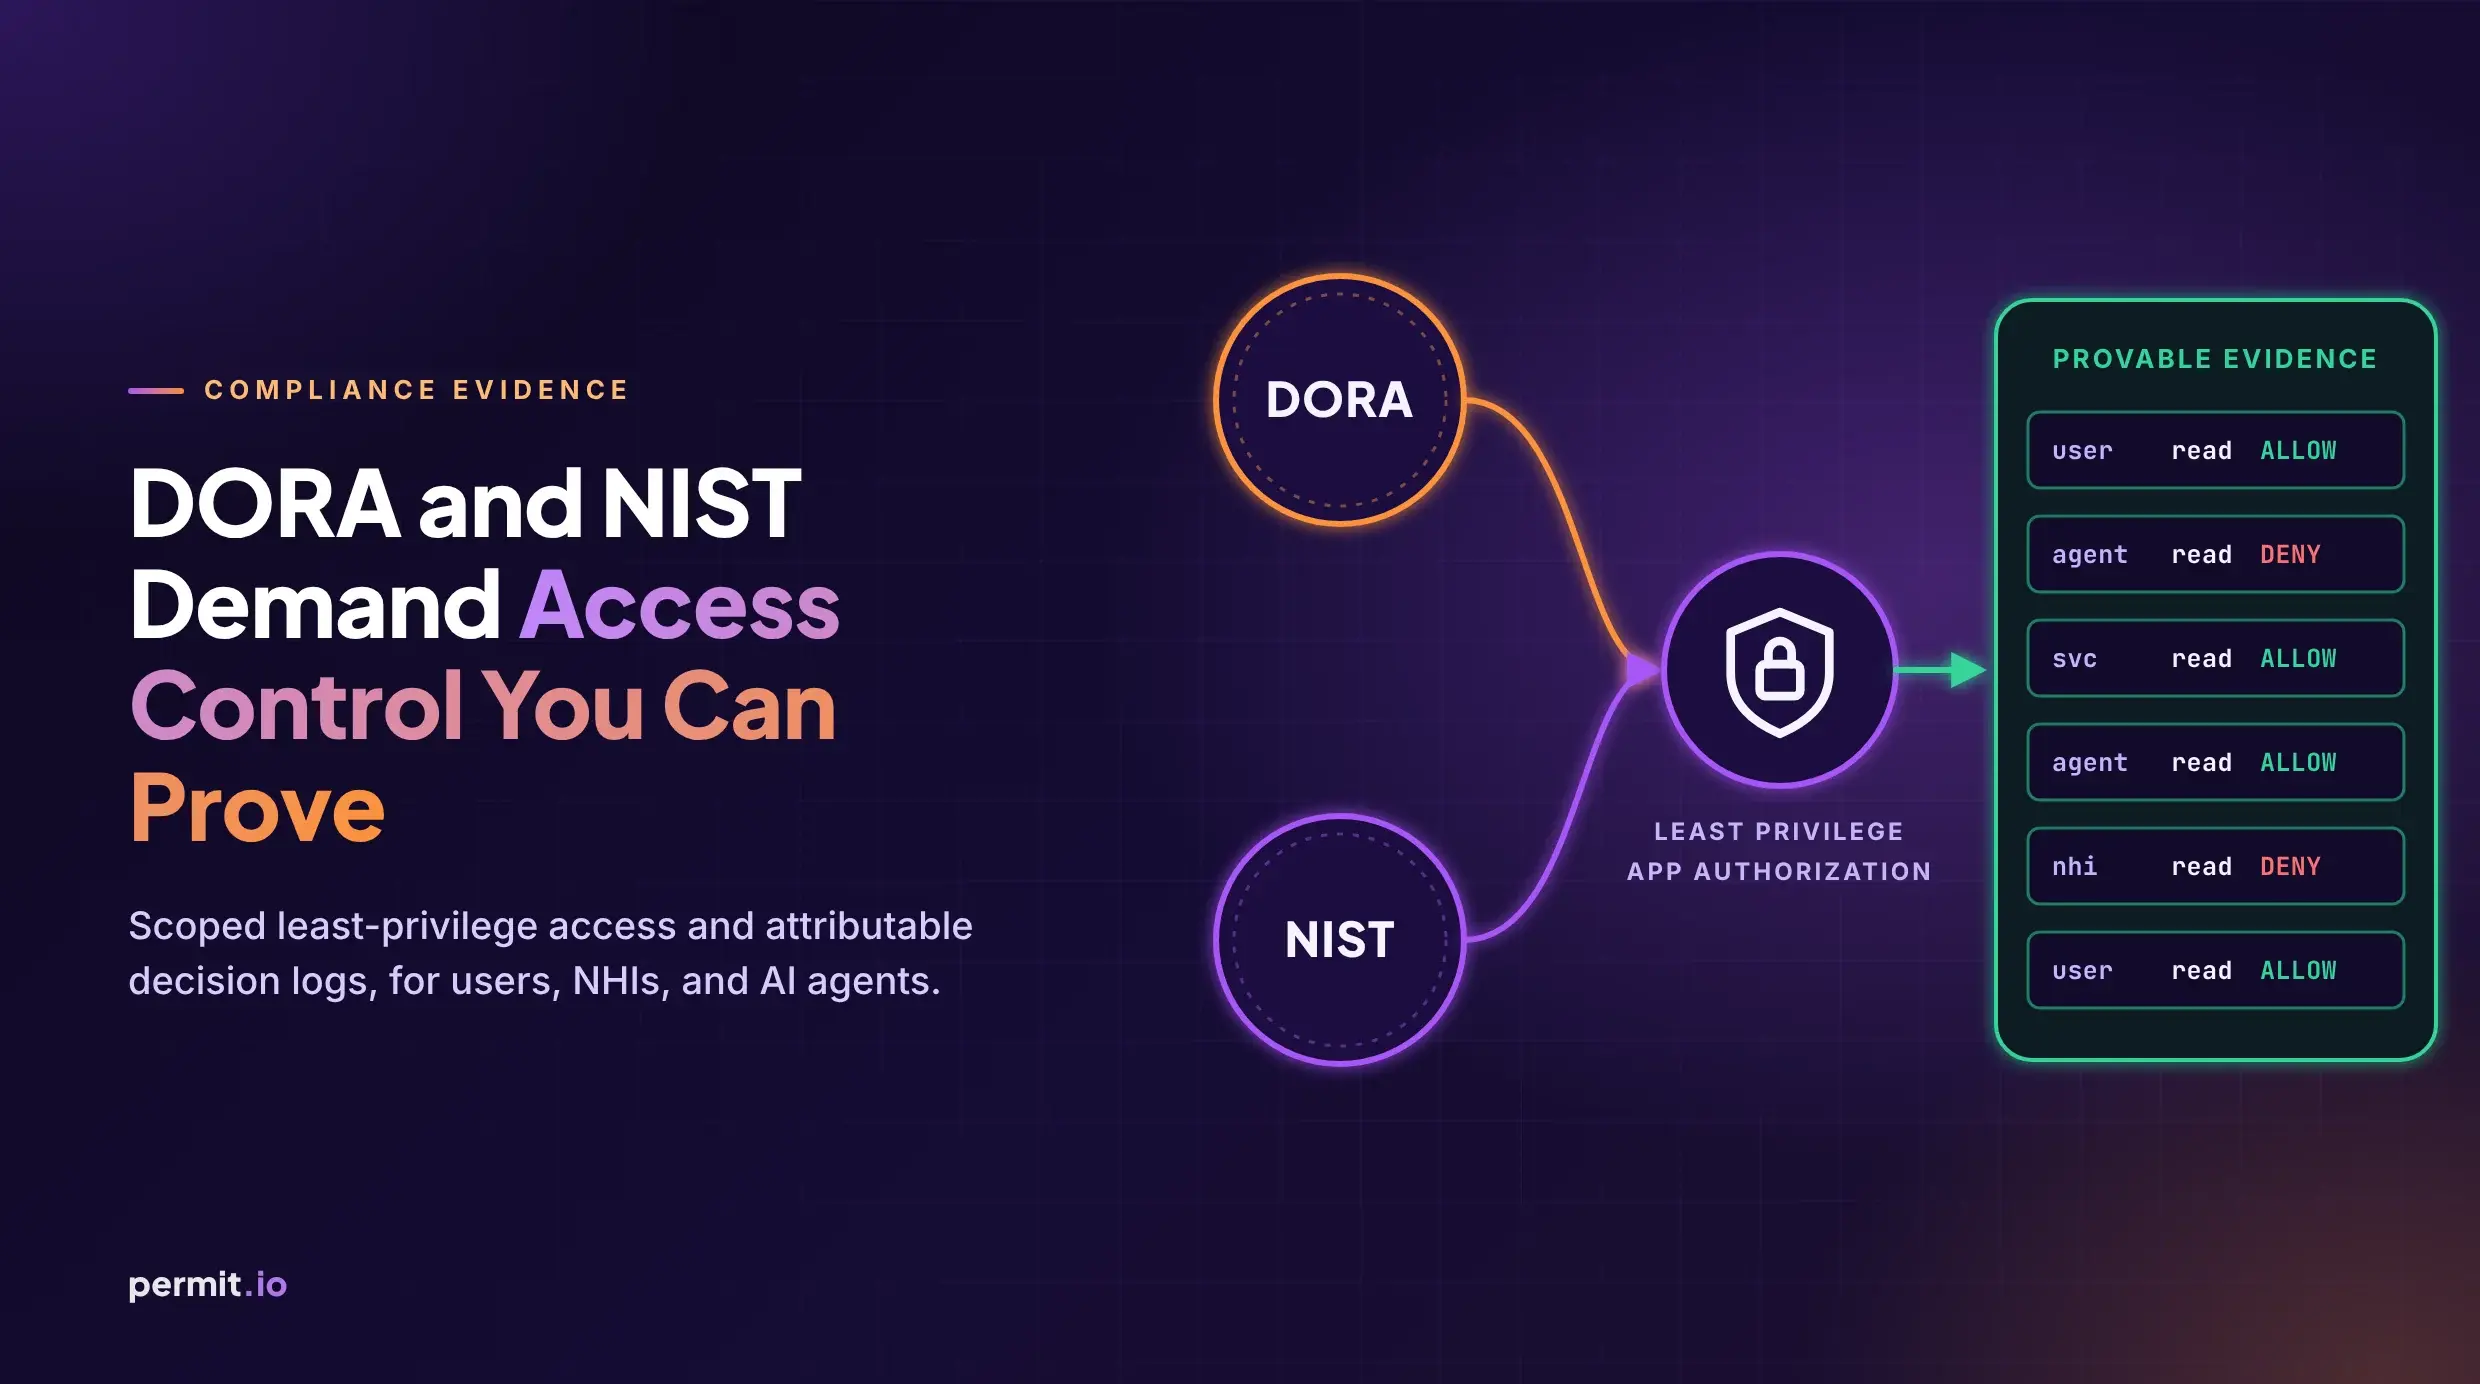
DORA and NIST do not prescribe a vendor. They expect scoped least-privilege access and attributable logs, including for NHIs and agents. Application FGA with decision logs is how product teams produce that evidence.
Or Weis
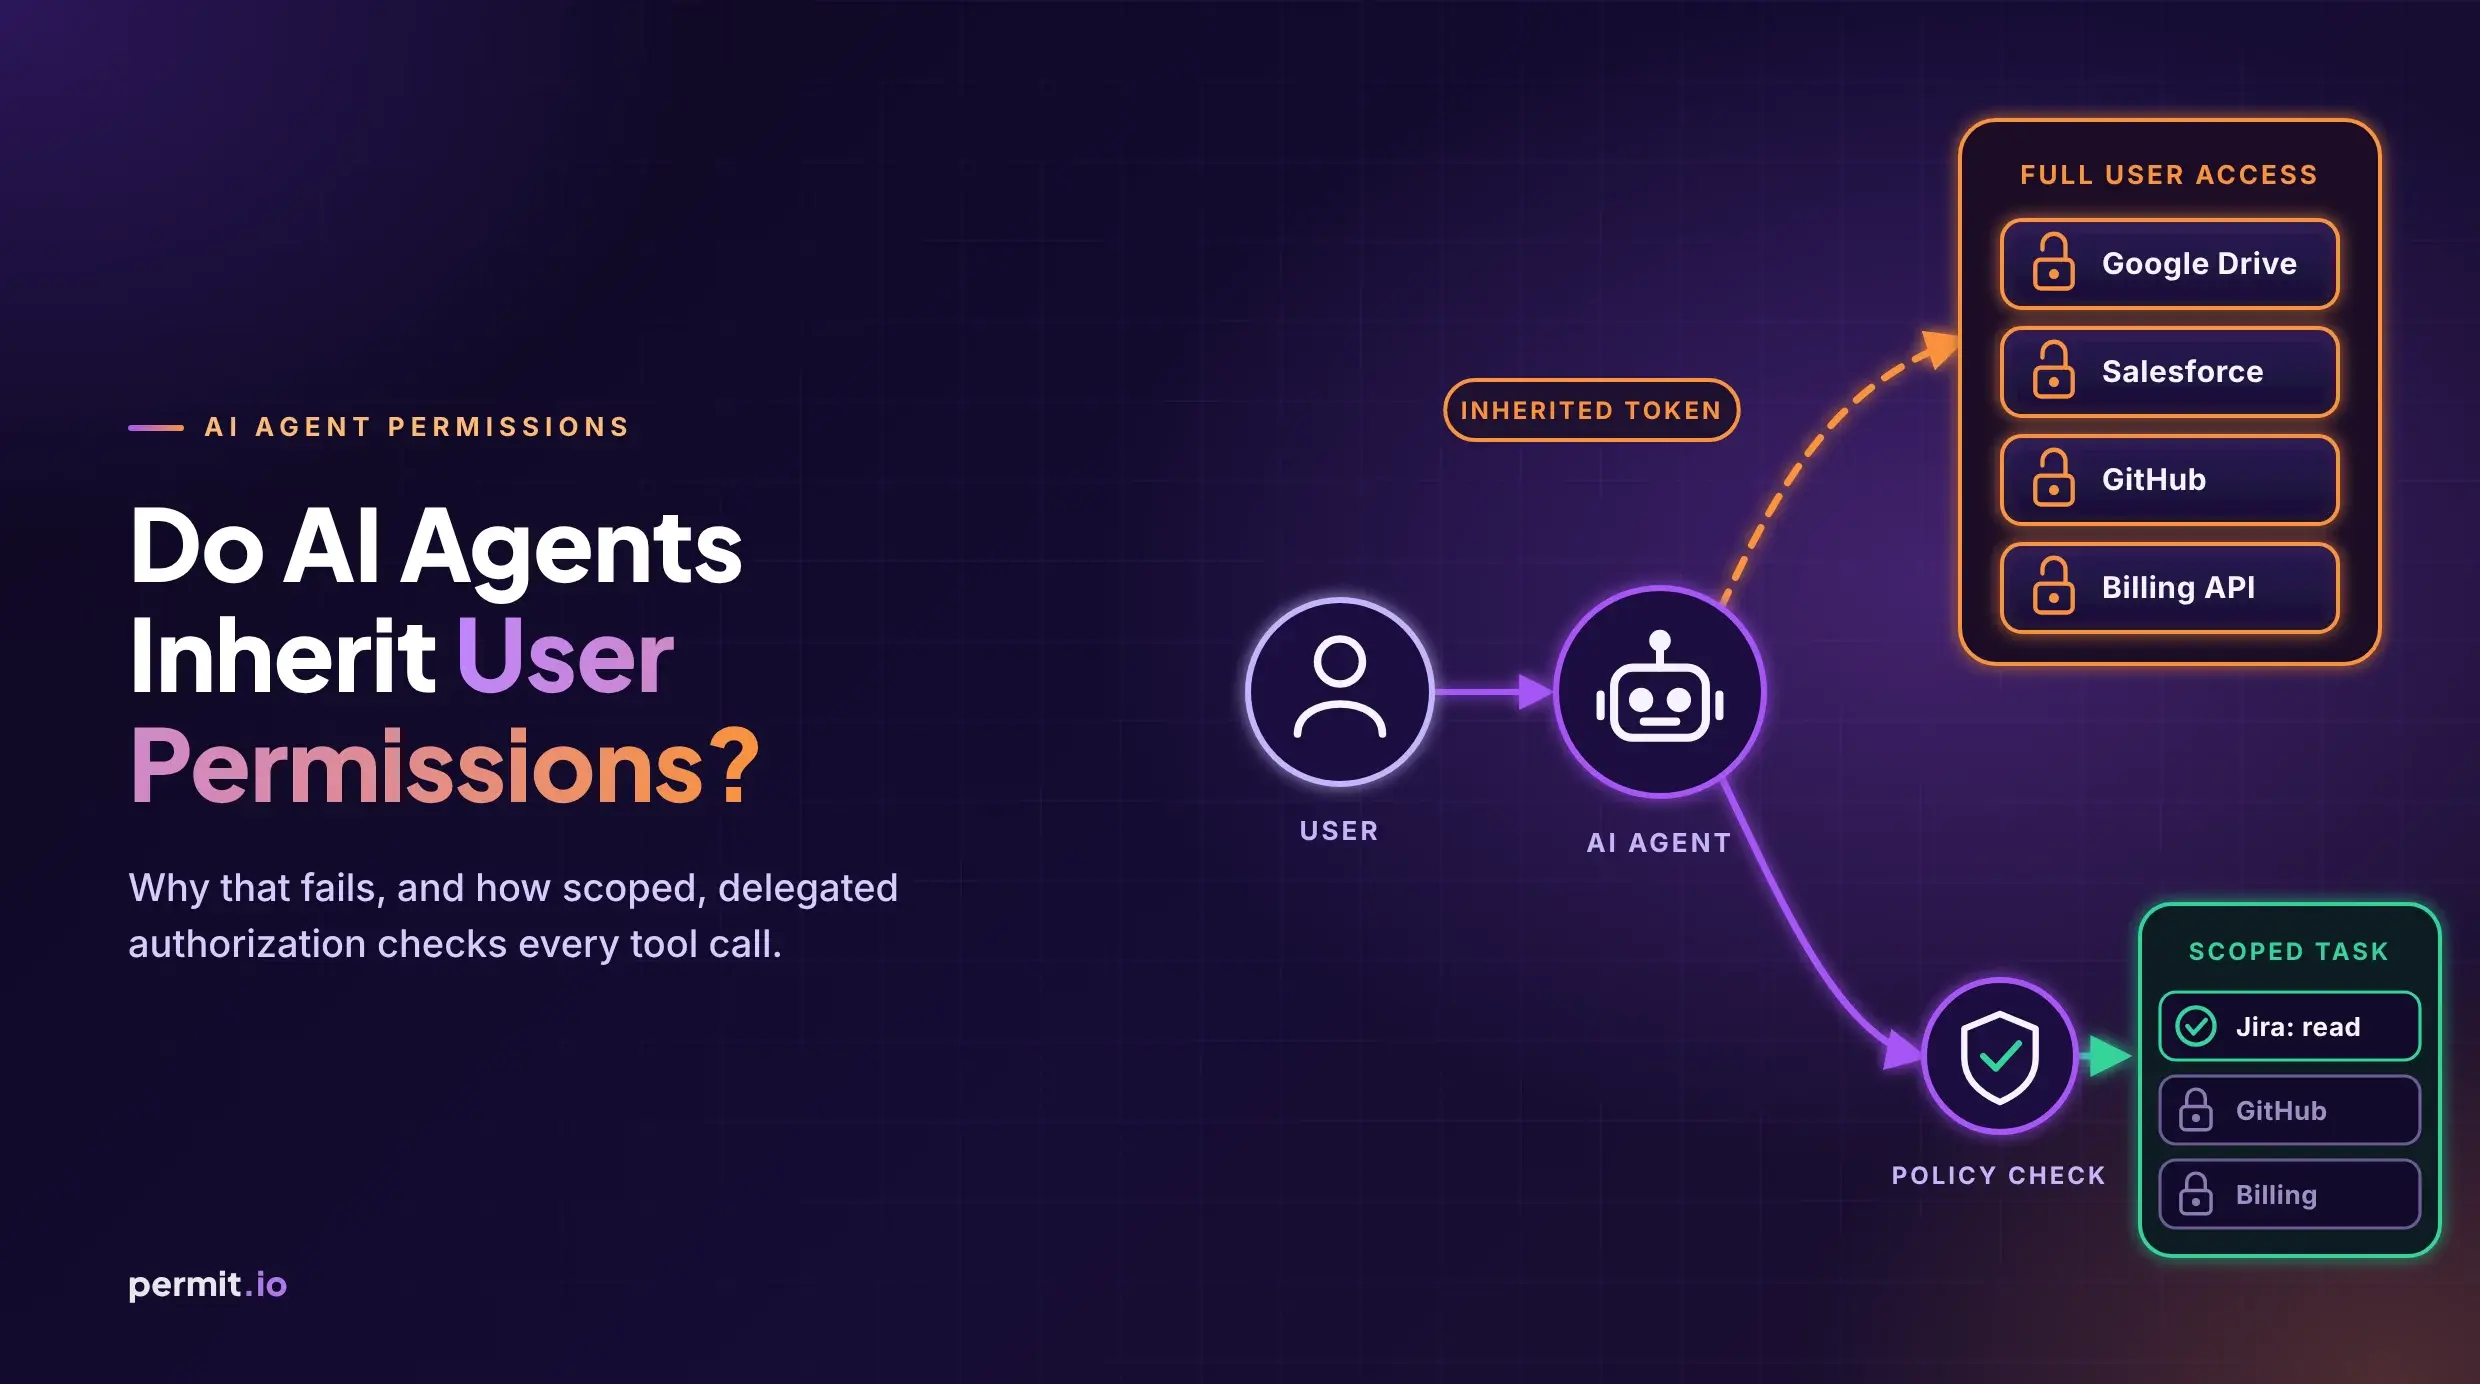
AI agents get their own IdP token, separate from the user session. OAuth scopes are too coarse for resource-level rules; check agent role at each tool call.
Or Weis
Your authorization model shapes least-privilege evidence in access reviews. Role assignments, attribute conditions, and relationship tuples each prove different things.
Or Weis
Hybrid authorization by default: RBAC for org roles, ABAC for context, ReBAC for sharing graphs—one check API across models. How to pick a stack before role explosion, and why least privilege needs explainable entitlements.
Or Weis
Authentication (AuthN) is who you are; authorization (AuthZ) is what you're allowed to do. Learn 401 vs 403, why IdPs don't replace app AuthZ, and how to externalize permissions.
Or Weis
SOC 2-style access reviews need more than IdP login events. Explainable allow and deny decision logs — decision provenance from identity to policy to resource — are the authorization evidence that makes application-level access controls concrete.
Or Weis
Every authorization decision should be explainable. Authorization observability is not more logs — it is decision provenance. Here is how to build an audit trail that answers why access was allowed or denied.
Or Weis
Fine-grained authorization belongs in a dedicated control plane—not scattered if-statements. Learn when to externalize authorization and stop rebuilding DIY RBAC in application code.
Or Weis
MCP servers are now operational control surfaces for cloud and API platforms. This article explains the trust model, control stack, and audit architecture enterprises need before AI agents can safely execute infrastructure actions.
Or Weis
A practical review guide for security, privacy, and procurement teams evaluating whether an MCP gateway can meet SOC 2, HIPAA, and privacy requirements — with concrete examples from Permit MCP Gateway.