
Loading
Teams · Product
Custom roles, team sharing, approval steps. Enterprise deals keep asking for them, and each one used to mean a backend project. With Permit, the permission model is something product and operations can change, inside guardrails engineering sets once.
“Permit’s intuitive policy editor allows access to complex attribute-based conditions that are robust enough for our developers to use, yet simple enough for our non-technical staff to configure without the need for IT assistance”
 Nate YoungChief Information Officer, Maricopa County Recorder’s Office
Enterprise buyers expect roles shaped to their org chart. With hardcoded roles, each request becomes engineering work.
Letting users share projects, reports, or workspaces safely looks like a small feature and hides a real authorization problem.
Customers want to invite users, assign roles, and approve access themselves, and someone has to build that interface.
Adjusting who can see a feature or take an action waits in the queue for the next deploy.
Engineering integrates once. After that, the permission model is configuration, not code.
Change roles and permissions in a no-code editor, inside guardrails engineering sets. At Maricopa County, non-technical staff configure attribute-based conditions without IT.
Add Elements to your product so customer admins invite users and assign roles themselves.
Let users request access and the right person approve it, inside your own UI, with a recorded trail.
Offer customer-defined roles through the API. Salt Security built a dashboard that maps access to each customer’s own structure.
Relationship-based policies make sharing a report grant access to that report, and nothing else in the workspace.
A viewer comments on a report shared with her directly. Illustrative data.
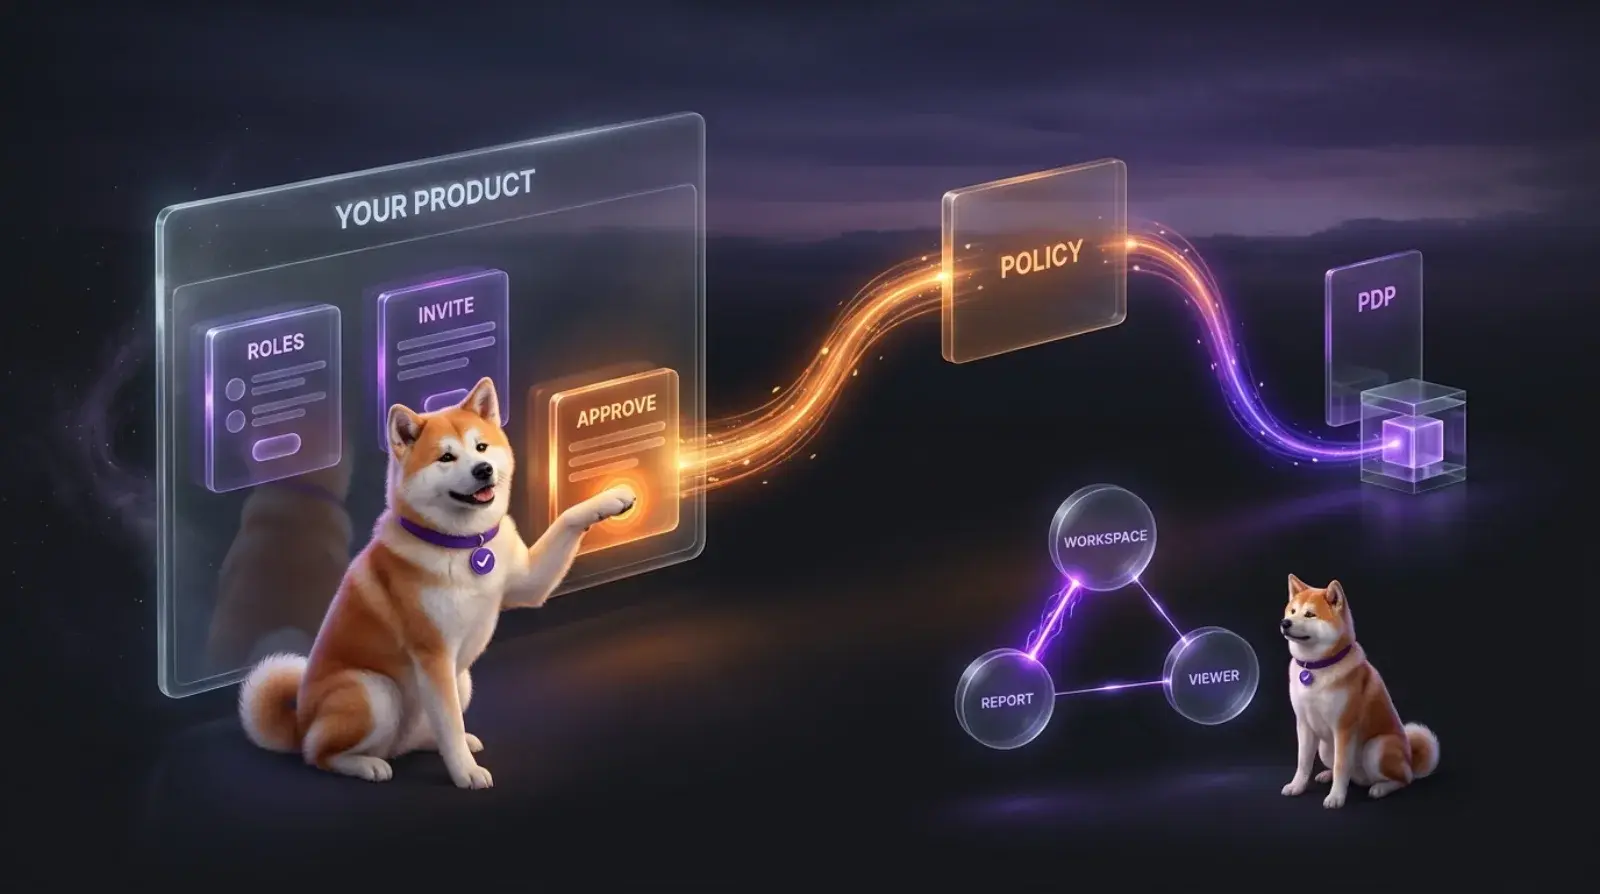
How a permission decision is made
“At Jules we aim to streamline the process of buying/selling recycled materials, and sharing access as part of our portal is an important step to achieve that. Allowing users to share access is both important to get right and hard to do so, we're delighted to have Permit solve this problem for us end to end.”
 Jean Philippe BoulCo-founder & COO, Jules AI
“We built a UI on top of Permit’s API, allowing our customers to configure permissions in a way that makes sense to them. Instead of forcing them into predefined roles, they can now map access controls to their own organizational structure.”
Yes. Editor changes are saved as policy code, and policy guards limit which roles and resources each team can change.
Embeddable UI components for user management, access requests, approval flows, and audit logs that you add to your own product.
Expose role management through Permit’s API or Elements. Customers define roles for their organization, within the permissions your policies allow them to grant.
No. Policy and data changes sync to decision points in real time, so updates apply without a release.
Not in a way users notice. Checks are answered by a decision point running next to your service instead of a remote call, and in Centauri AI’s case study they ran in single-digit milliseconds.
Tell us what you are authorizing and where it runs. We come to the call with a model of how Permit would enforce it.