
Or Weis
Announcing Permit MCP Gateway
Announcing Permit MCP Gateway, a new trust and enforcement layer for MCP that brings identity, consent, fine-grained authorization, auditability, and runtime control to AI agent actions.
Read more
Featured Stories
Or Weis
Announcing Permit MCP Gateway, a new trust and enforcement layer for MCP that brings identity, consent, fine-grained authorization, auditability, and runtime control to AI agent actions.
Gabriel L. Manor
The new Permit.io CLI brings developer-first workflows to access control. Define, test, deploy, and enforce fine-grained authorization using AI, CI/CD, GitOps, and OpenAPI — all from your terminal
Or Weis
An embeddable PDP runs policy evaluation inside your application process. Compare it with sidecar and remote PDPs on latency, data sync, upgrades and operations, and learn when to pick each.
Ziv Cohen
Enterprise-Managed Authorization lets organizations connect users to MCP servers without per-user OAuth consent screens. This guide covers how Claude auto-connect and ID-JAG identity assertions work, how to validate them securely with tenant isolation, and where application-level per-tool authorization picks up after the identity exchange.
Ze'ev Manilovich
An AI agent with delegated access is a textbook confused deputy: it holds real authority and can be talked into using it for someone else. Here is how it happens over MCP and the delegated access pattern that stops it.
Or Weis
An AI agent can be aligned with its task when you hand it a token and drifting two minutes later. Here is how the alignment problem shows up in real agent workflows, and how to enforce alignment at runtime with a per-action authorization check.
Ze'ev Manilovich
Auth0 FGA provides managed relationship-based authorization built on OpenFGA. A comparison with Permit.io covering policy languages, deployment models, and enterprise features.
Or Weis
OPA vs OpenFGA vs Cedar: comparing policy engines for fine-grained authorization. Strengths, trade-offs, and use cases of OPA, OpenFGA, and Cedar for scalable access control.
Or Weis
OpenFGA alternatives for fine-grained authorization including SpiceDB, Cerbos, OPA, Cedar, and Permit.io. A comparison of relationship-based and policy-based approaches to help you choose.
Ze'ev Manilovich
WorkOS FGA extends RBAC with hierarchical resource scoping. A comparison with Permit.io covering policy languages, deployment models, and when each fits your authorization requirements.
Or Weis
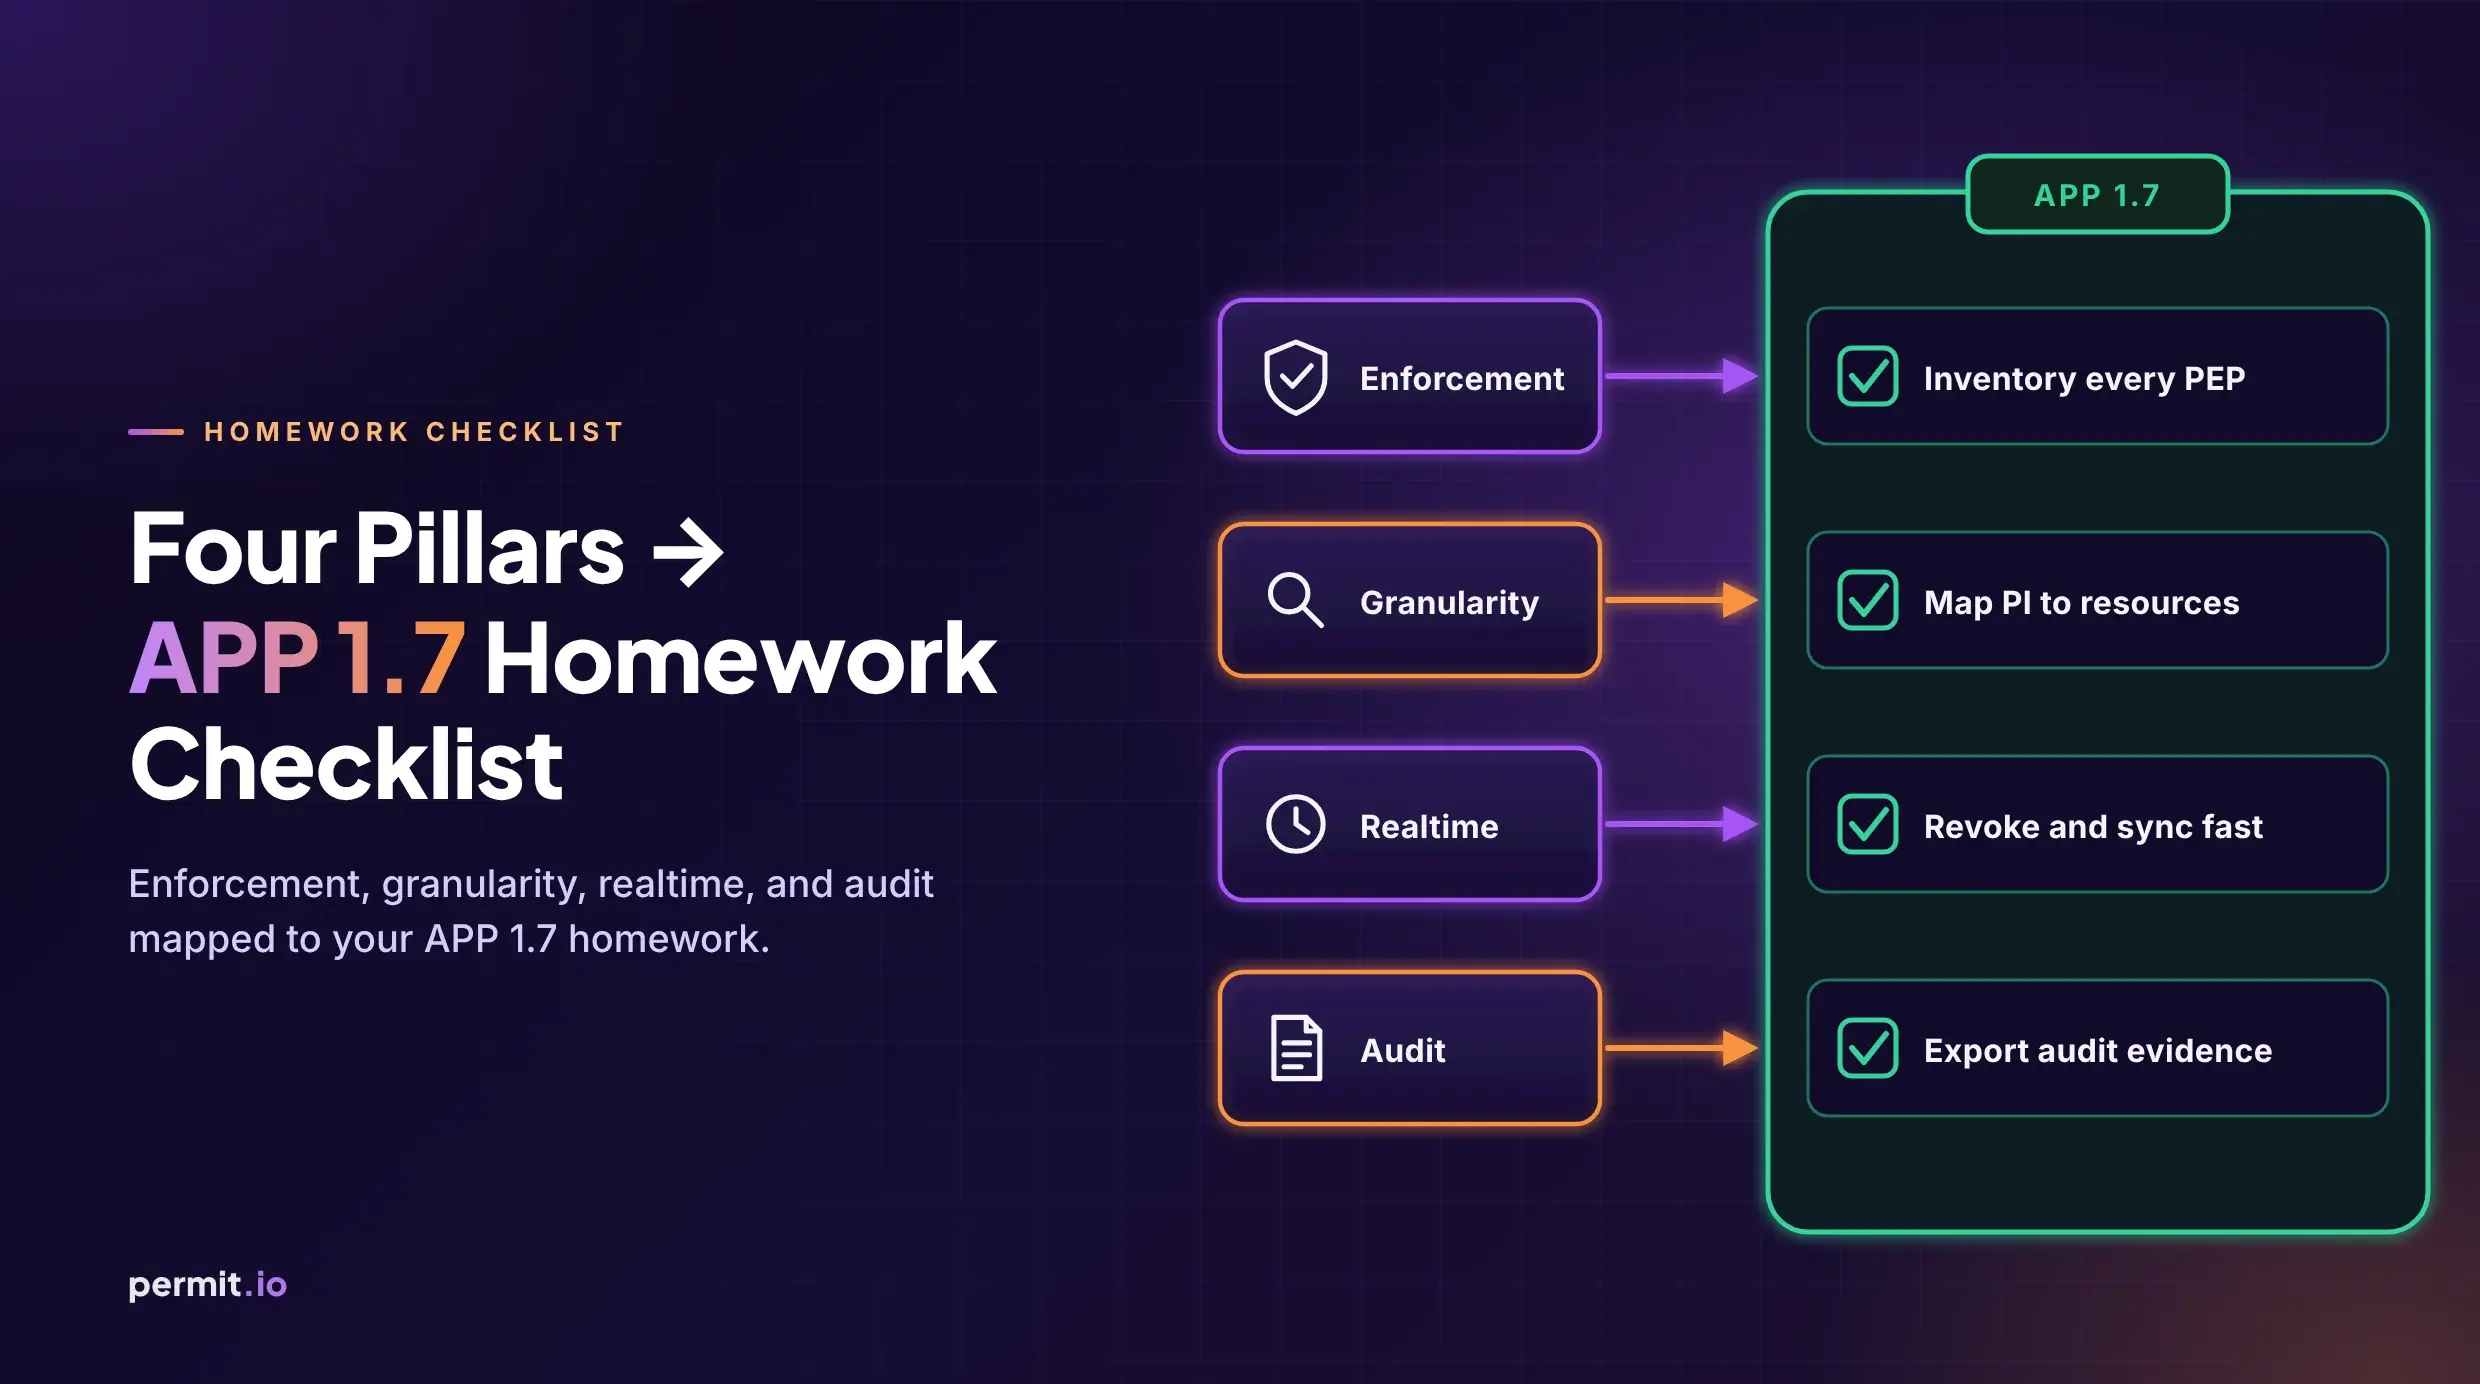
Map enforcement, granularity, realtime, and audit to APP 1.7 homework: inventory PEPs, PI→resource maps, revoke/sync, and audit/export for privacy-policy statements.
Or Weis
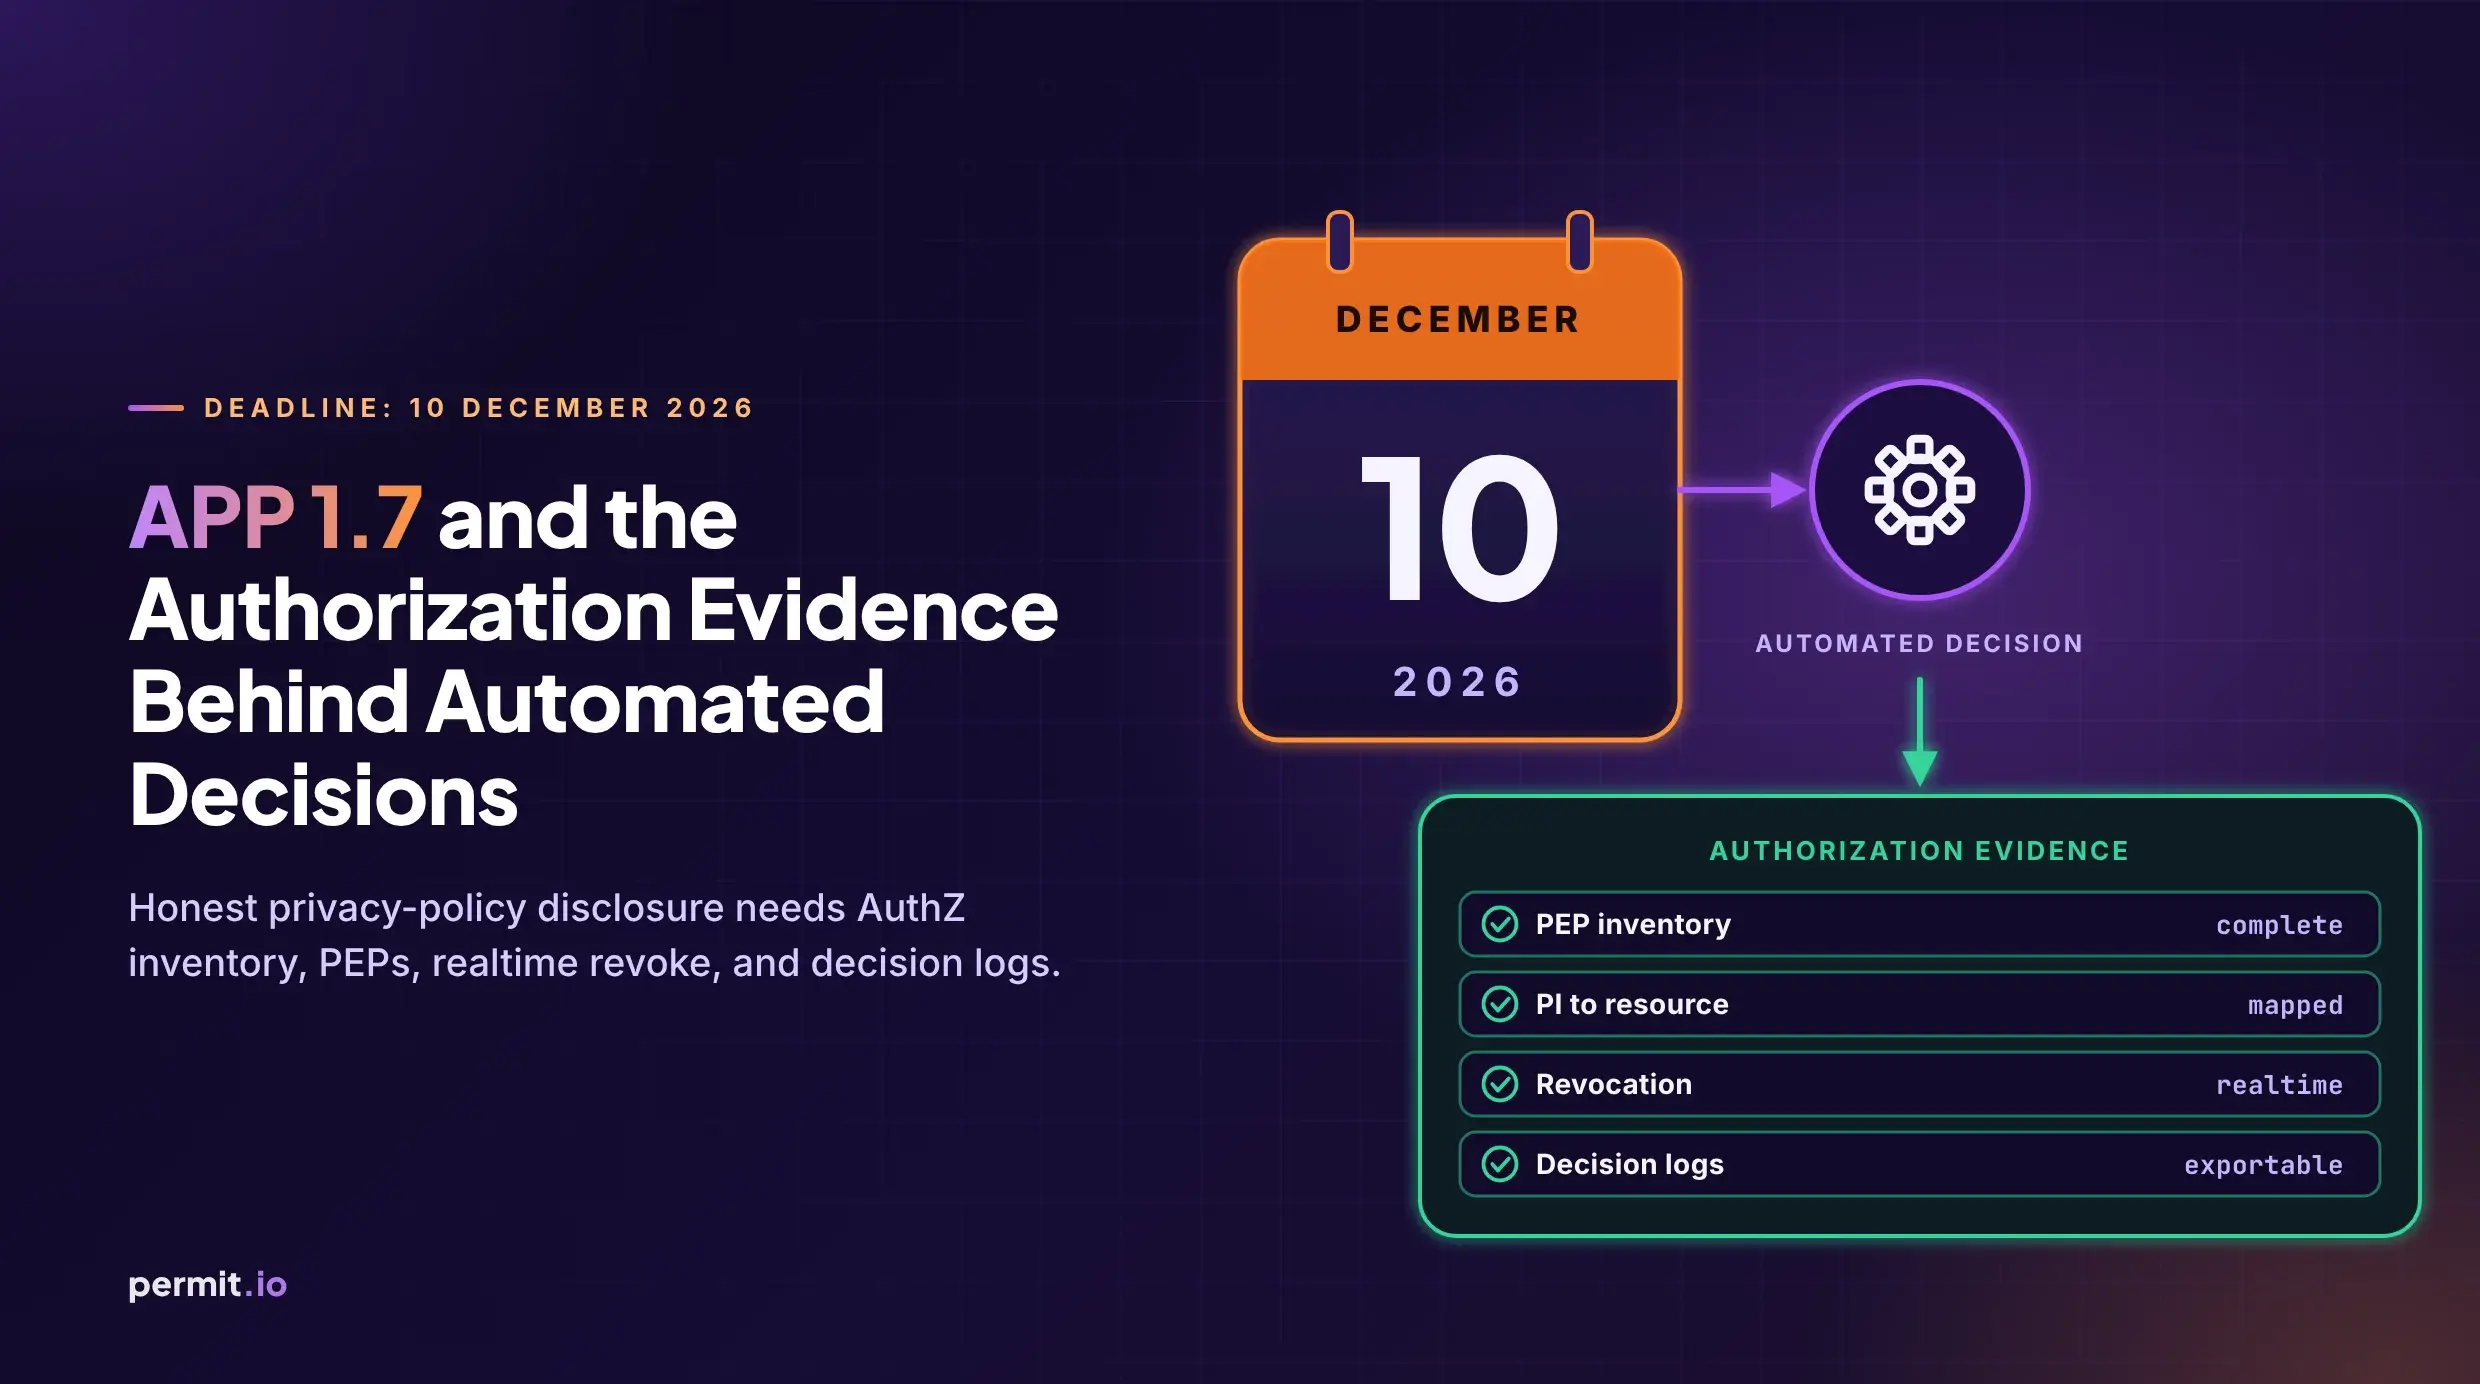
APP 1.7-1.9 commence 10 December 2026. Honest ADM privacy-policy disclosure needs AuthZ inventory, PI→resource maps, PEPs, realtime revoke, and decision-log evidence, plus a soft APRA parallel.
Ze'ev Manilovich
EN 18286:2026 is Europe's first harmonised standard under the EU AI Act. It turns Article 17's QMS requirements into auditable processes. Here's what it means for teams shipping AI agents.
Or Weis
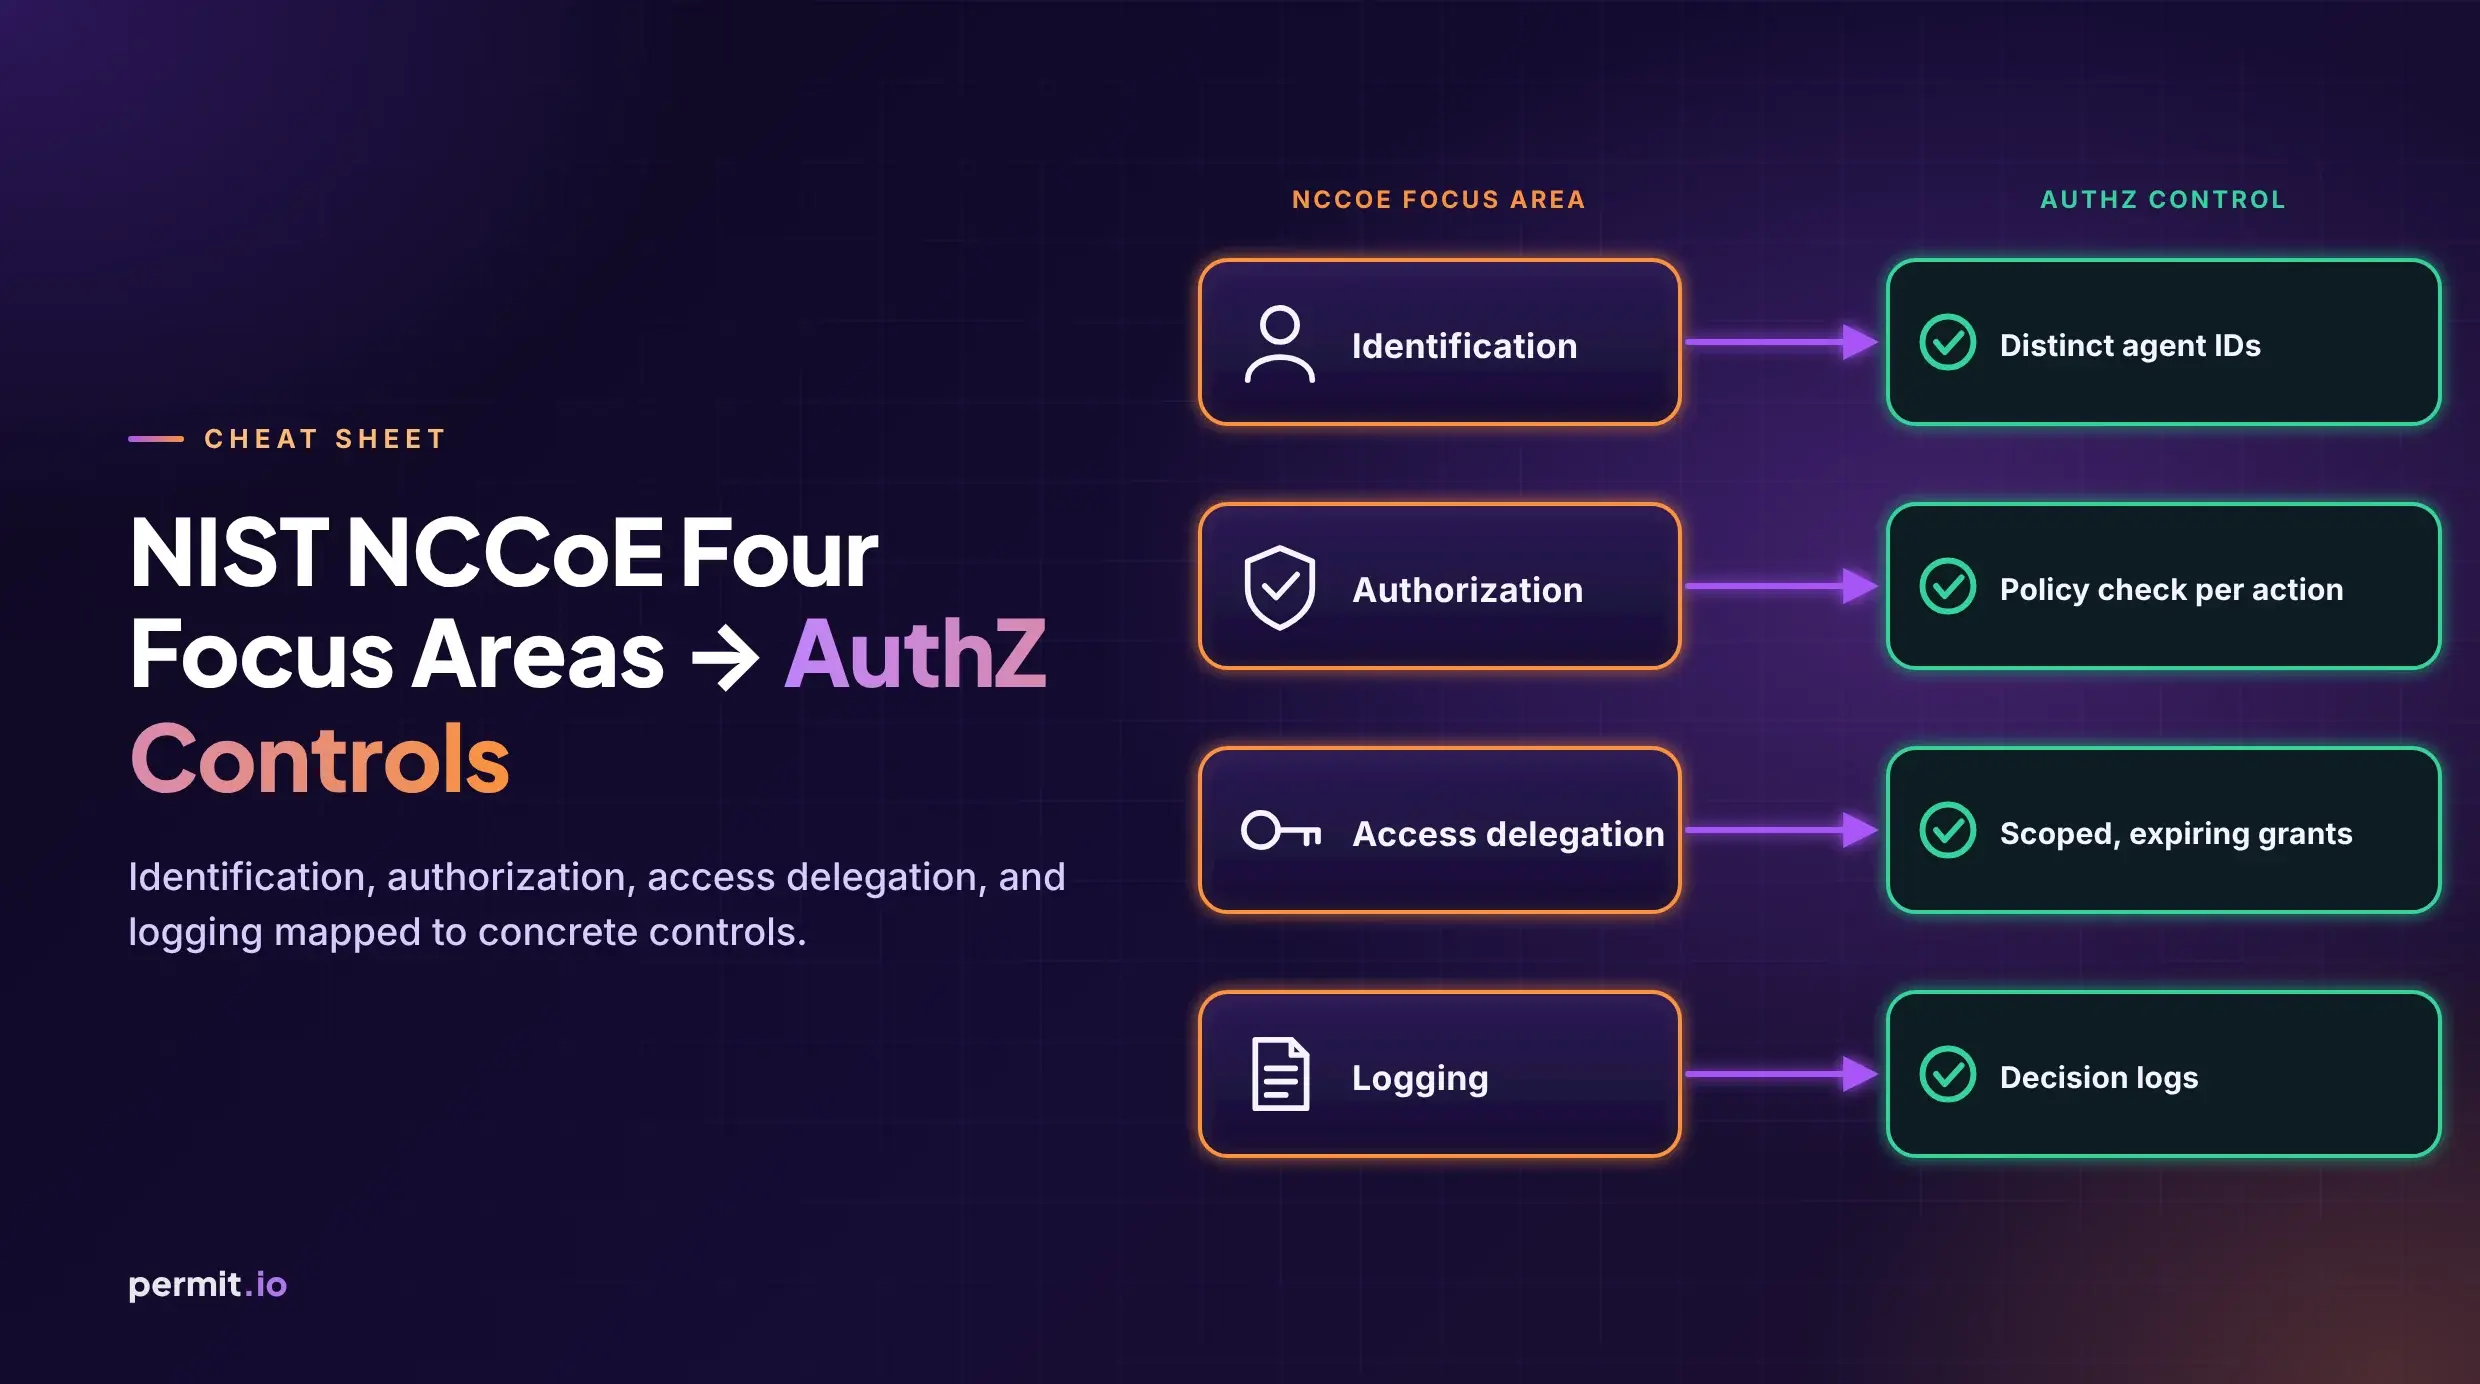
Cheat-sheet: NIST NCCoE's four focus areas (identification, authorization, access delegation, and logging) mapped to concrete AuthZ controls. Soft alignment aid, not a certification checklist.