
Or Weis
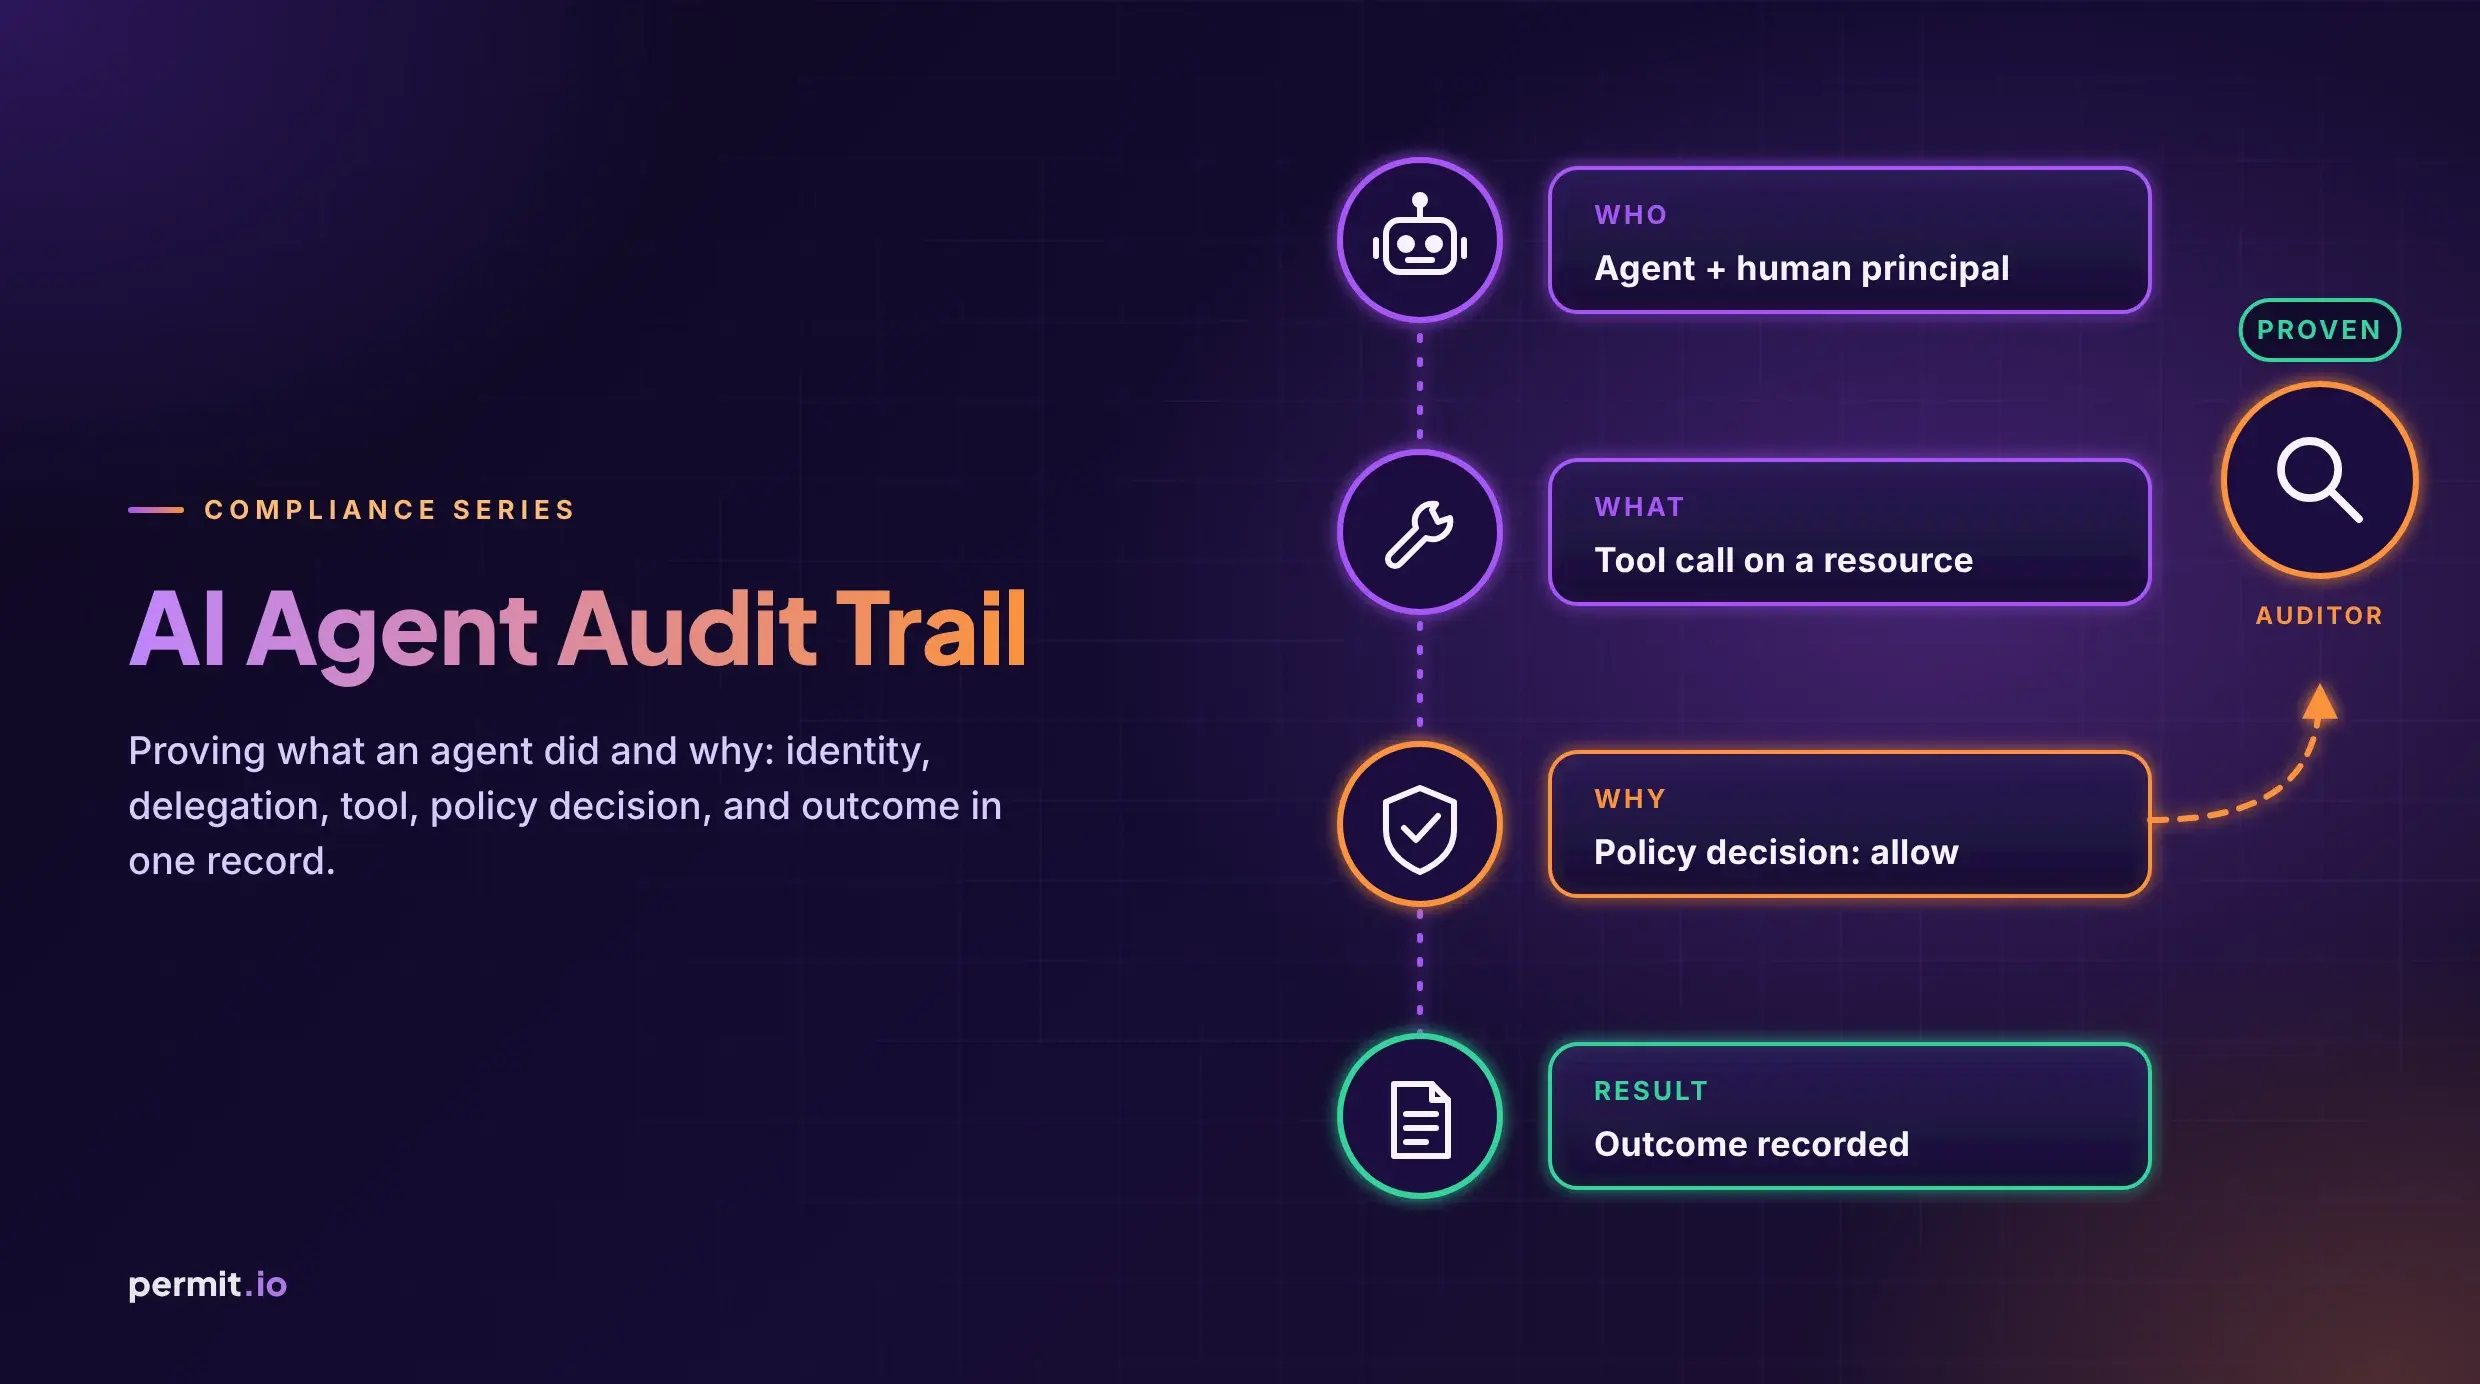
AI Agent Audit Trail: Proving What an Agent Did and Why
An AI agent audit trail binds identity, delegation, tool, resource, policy, allow/deny, HITL, and outcome. Tool traces are not enough.
Read more
Co-Founder / CEO at Permit.io

Or Weis
An AI agent audit trail binds identity, delegation, tool, resource, policy, allow/deny, HITL, and outcome. Tool traces are not enough.
Or Weis
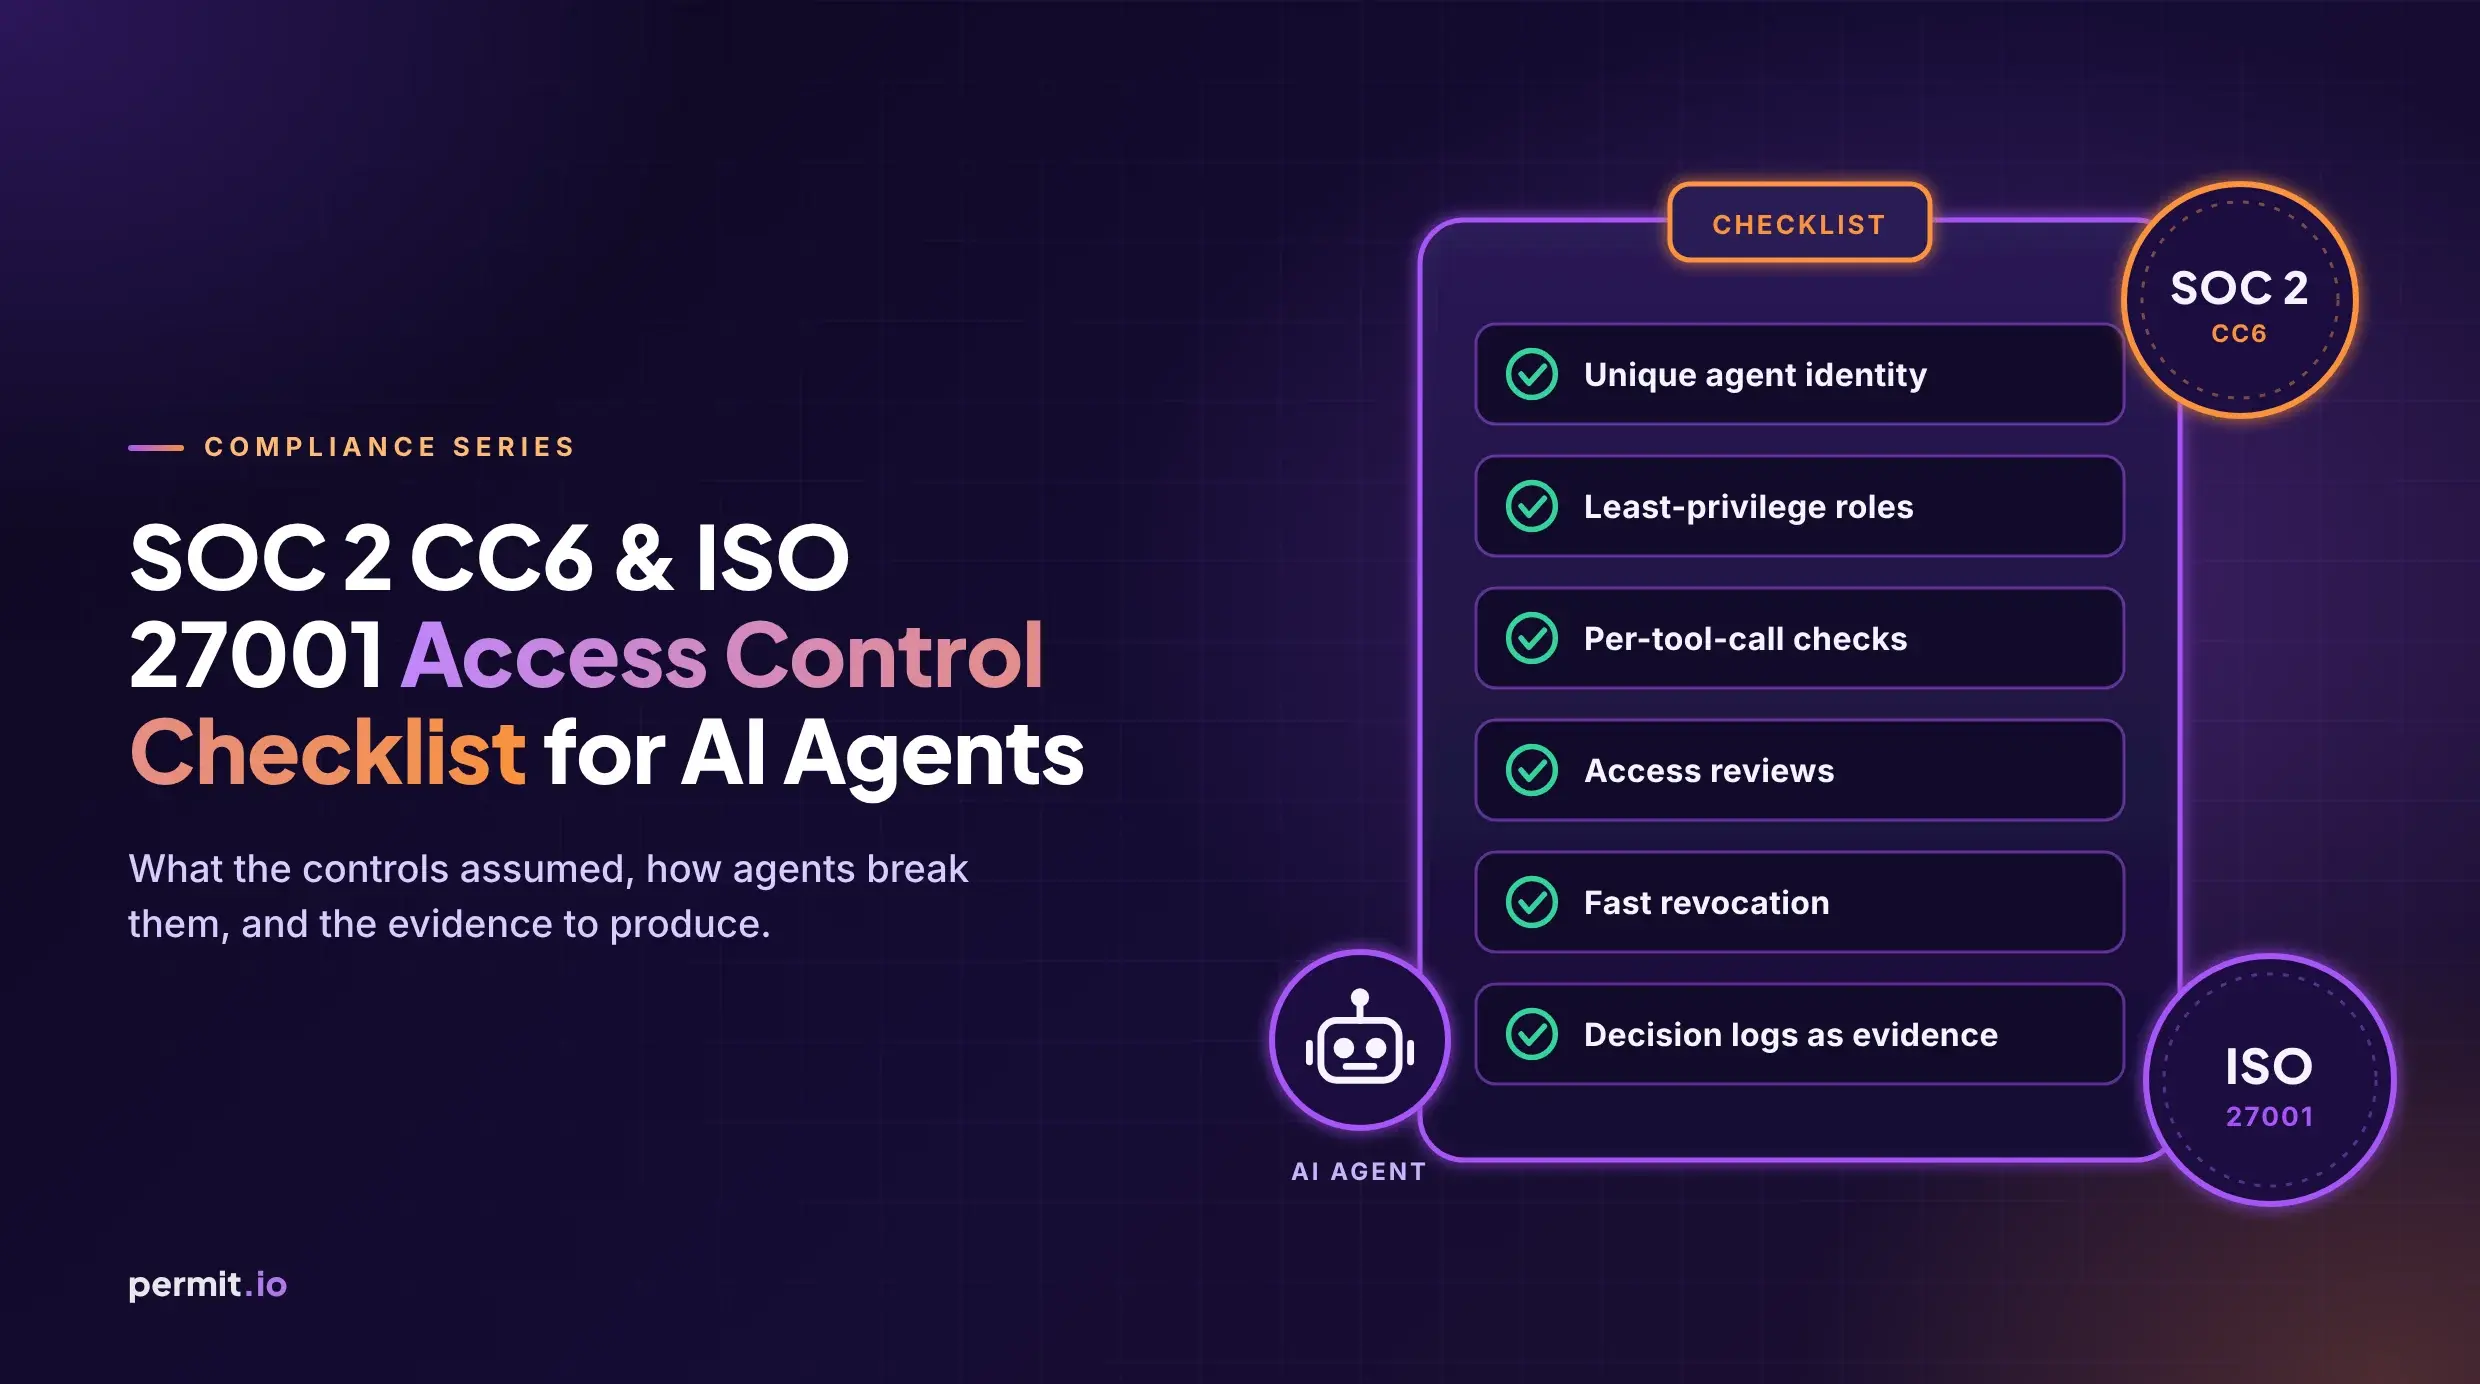
SOC 2 CC6 and ISO 27001 access control checklist for AI agents: what controls assumed, how agents break them, evidence to produce.
Or Weis
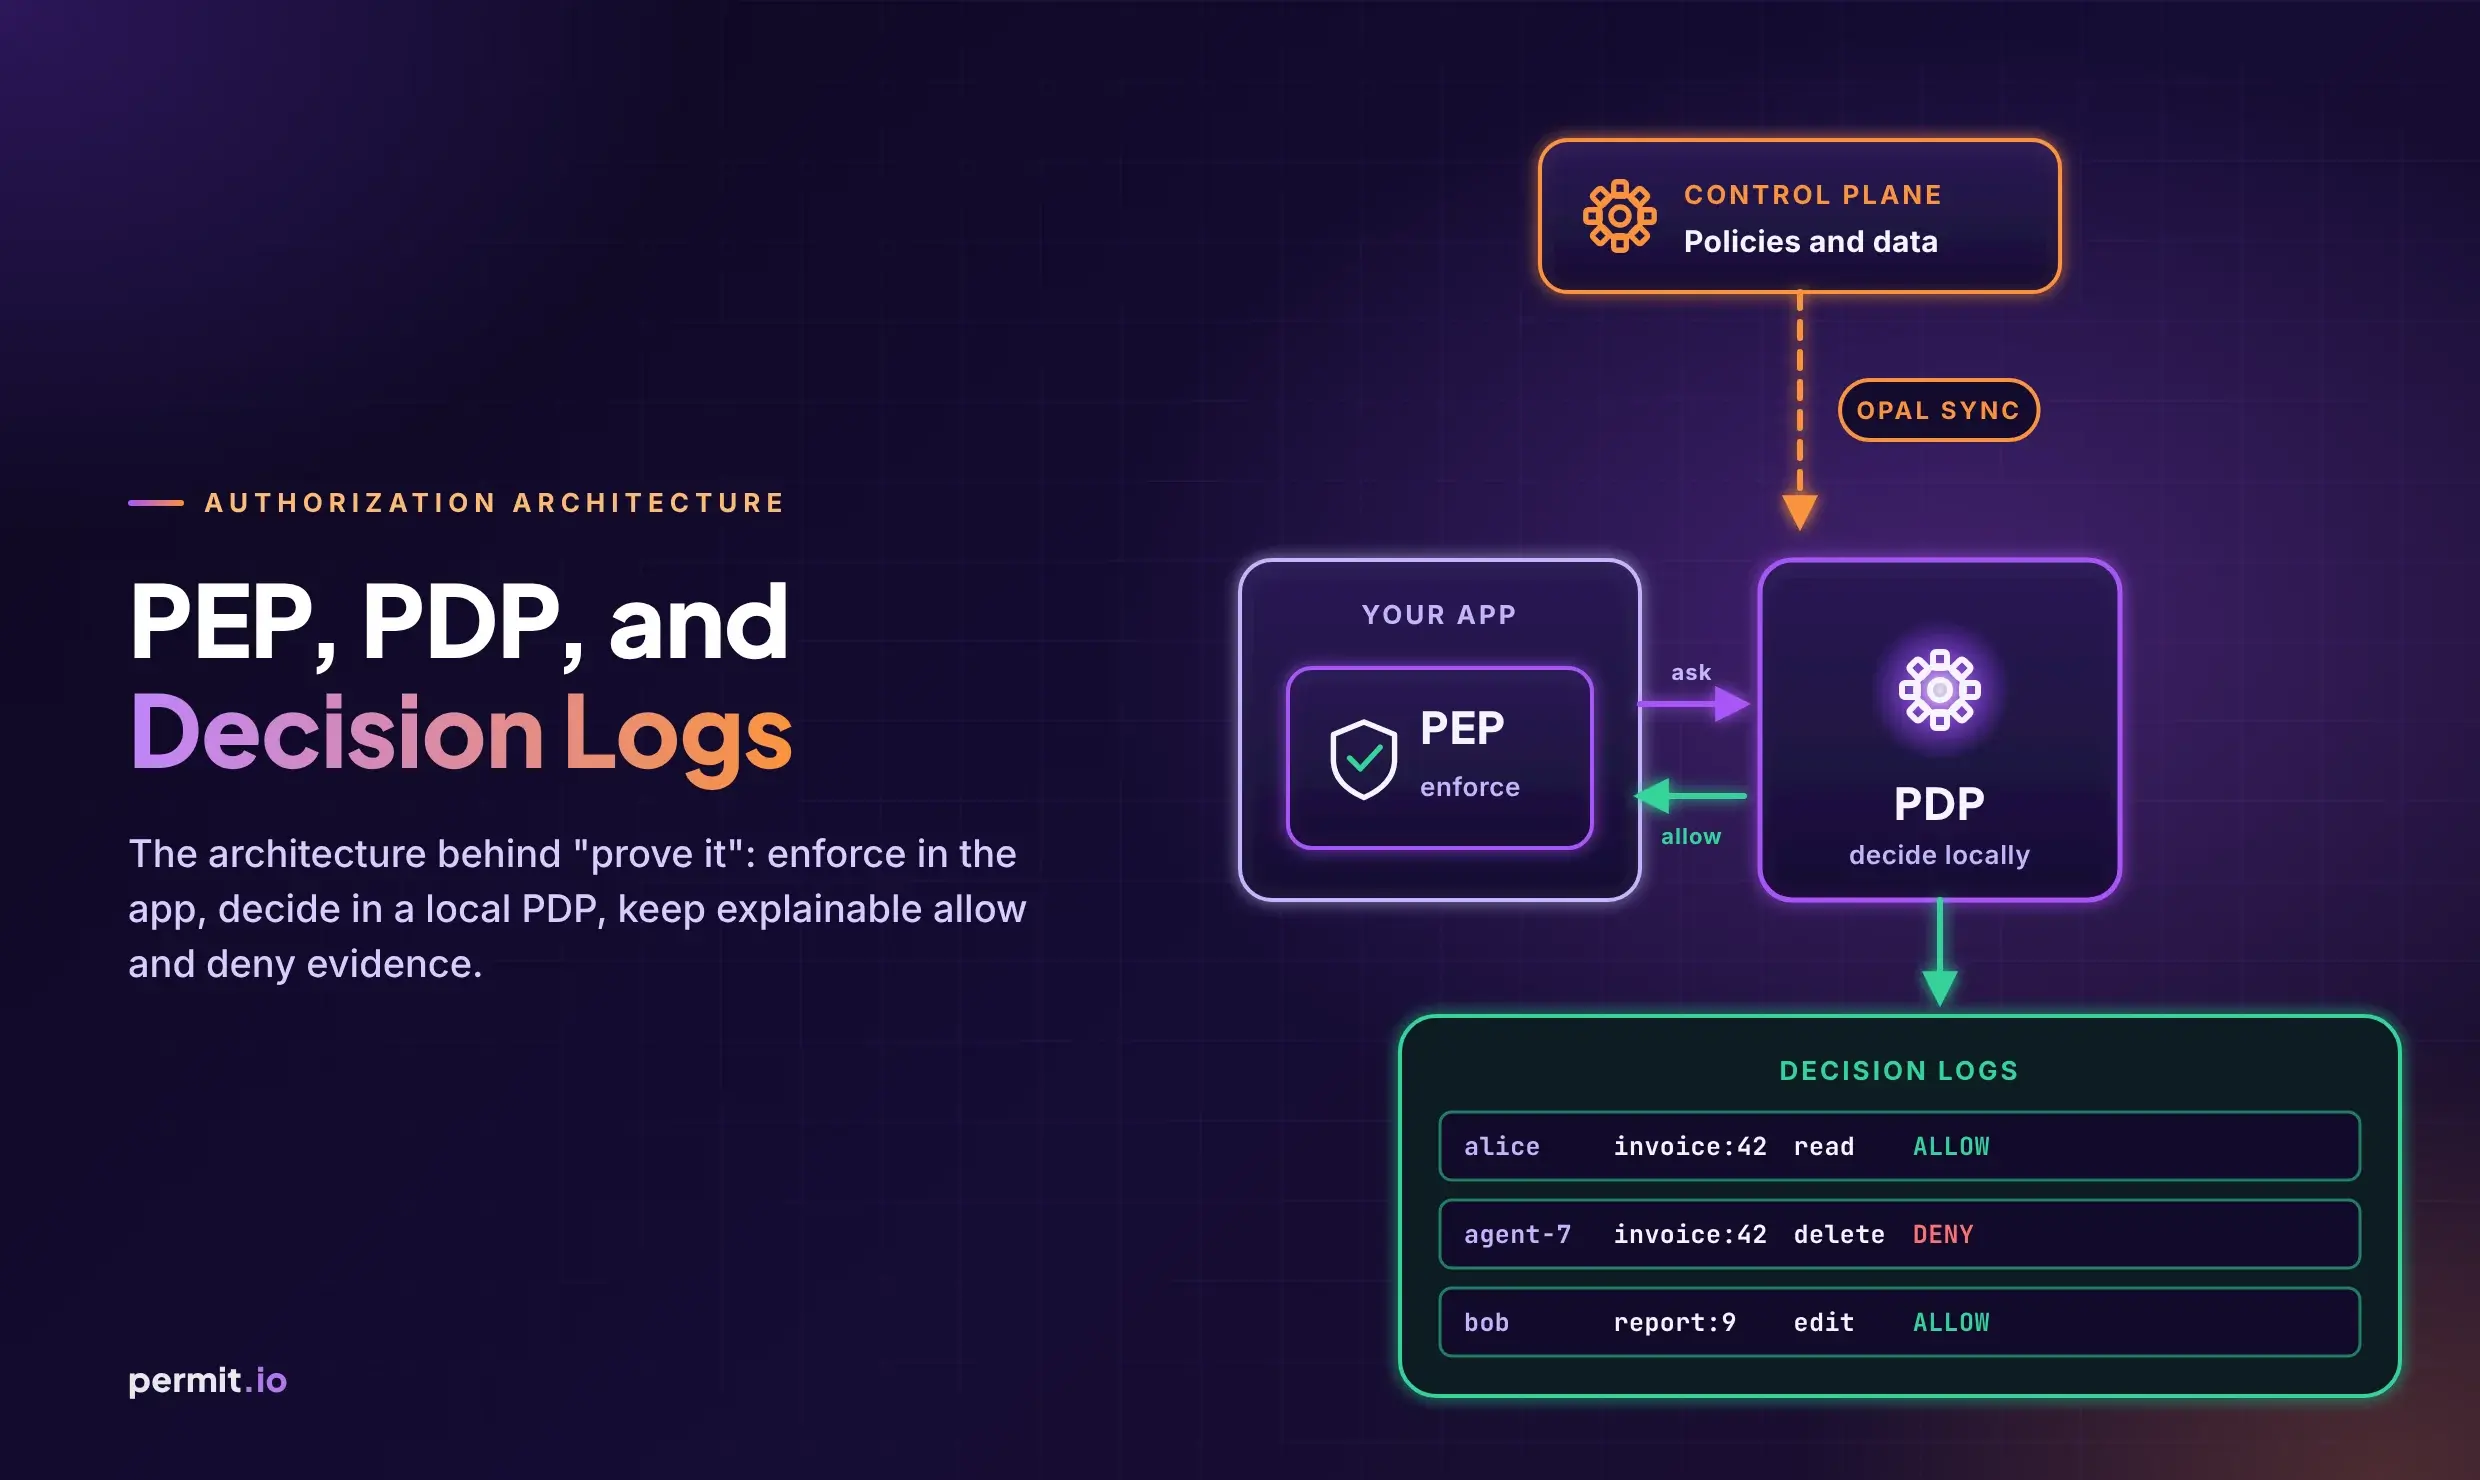
Regulators’ “prove it” maps to PEP + PDP + decision logs: enforce in the app, decide in a local PDP synced by OPAL, and keep explainable allow/deny evidence.
Or Weis
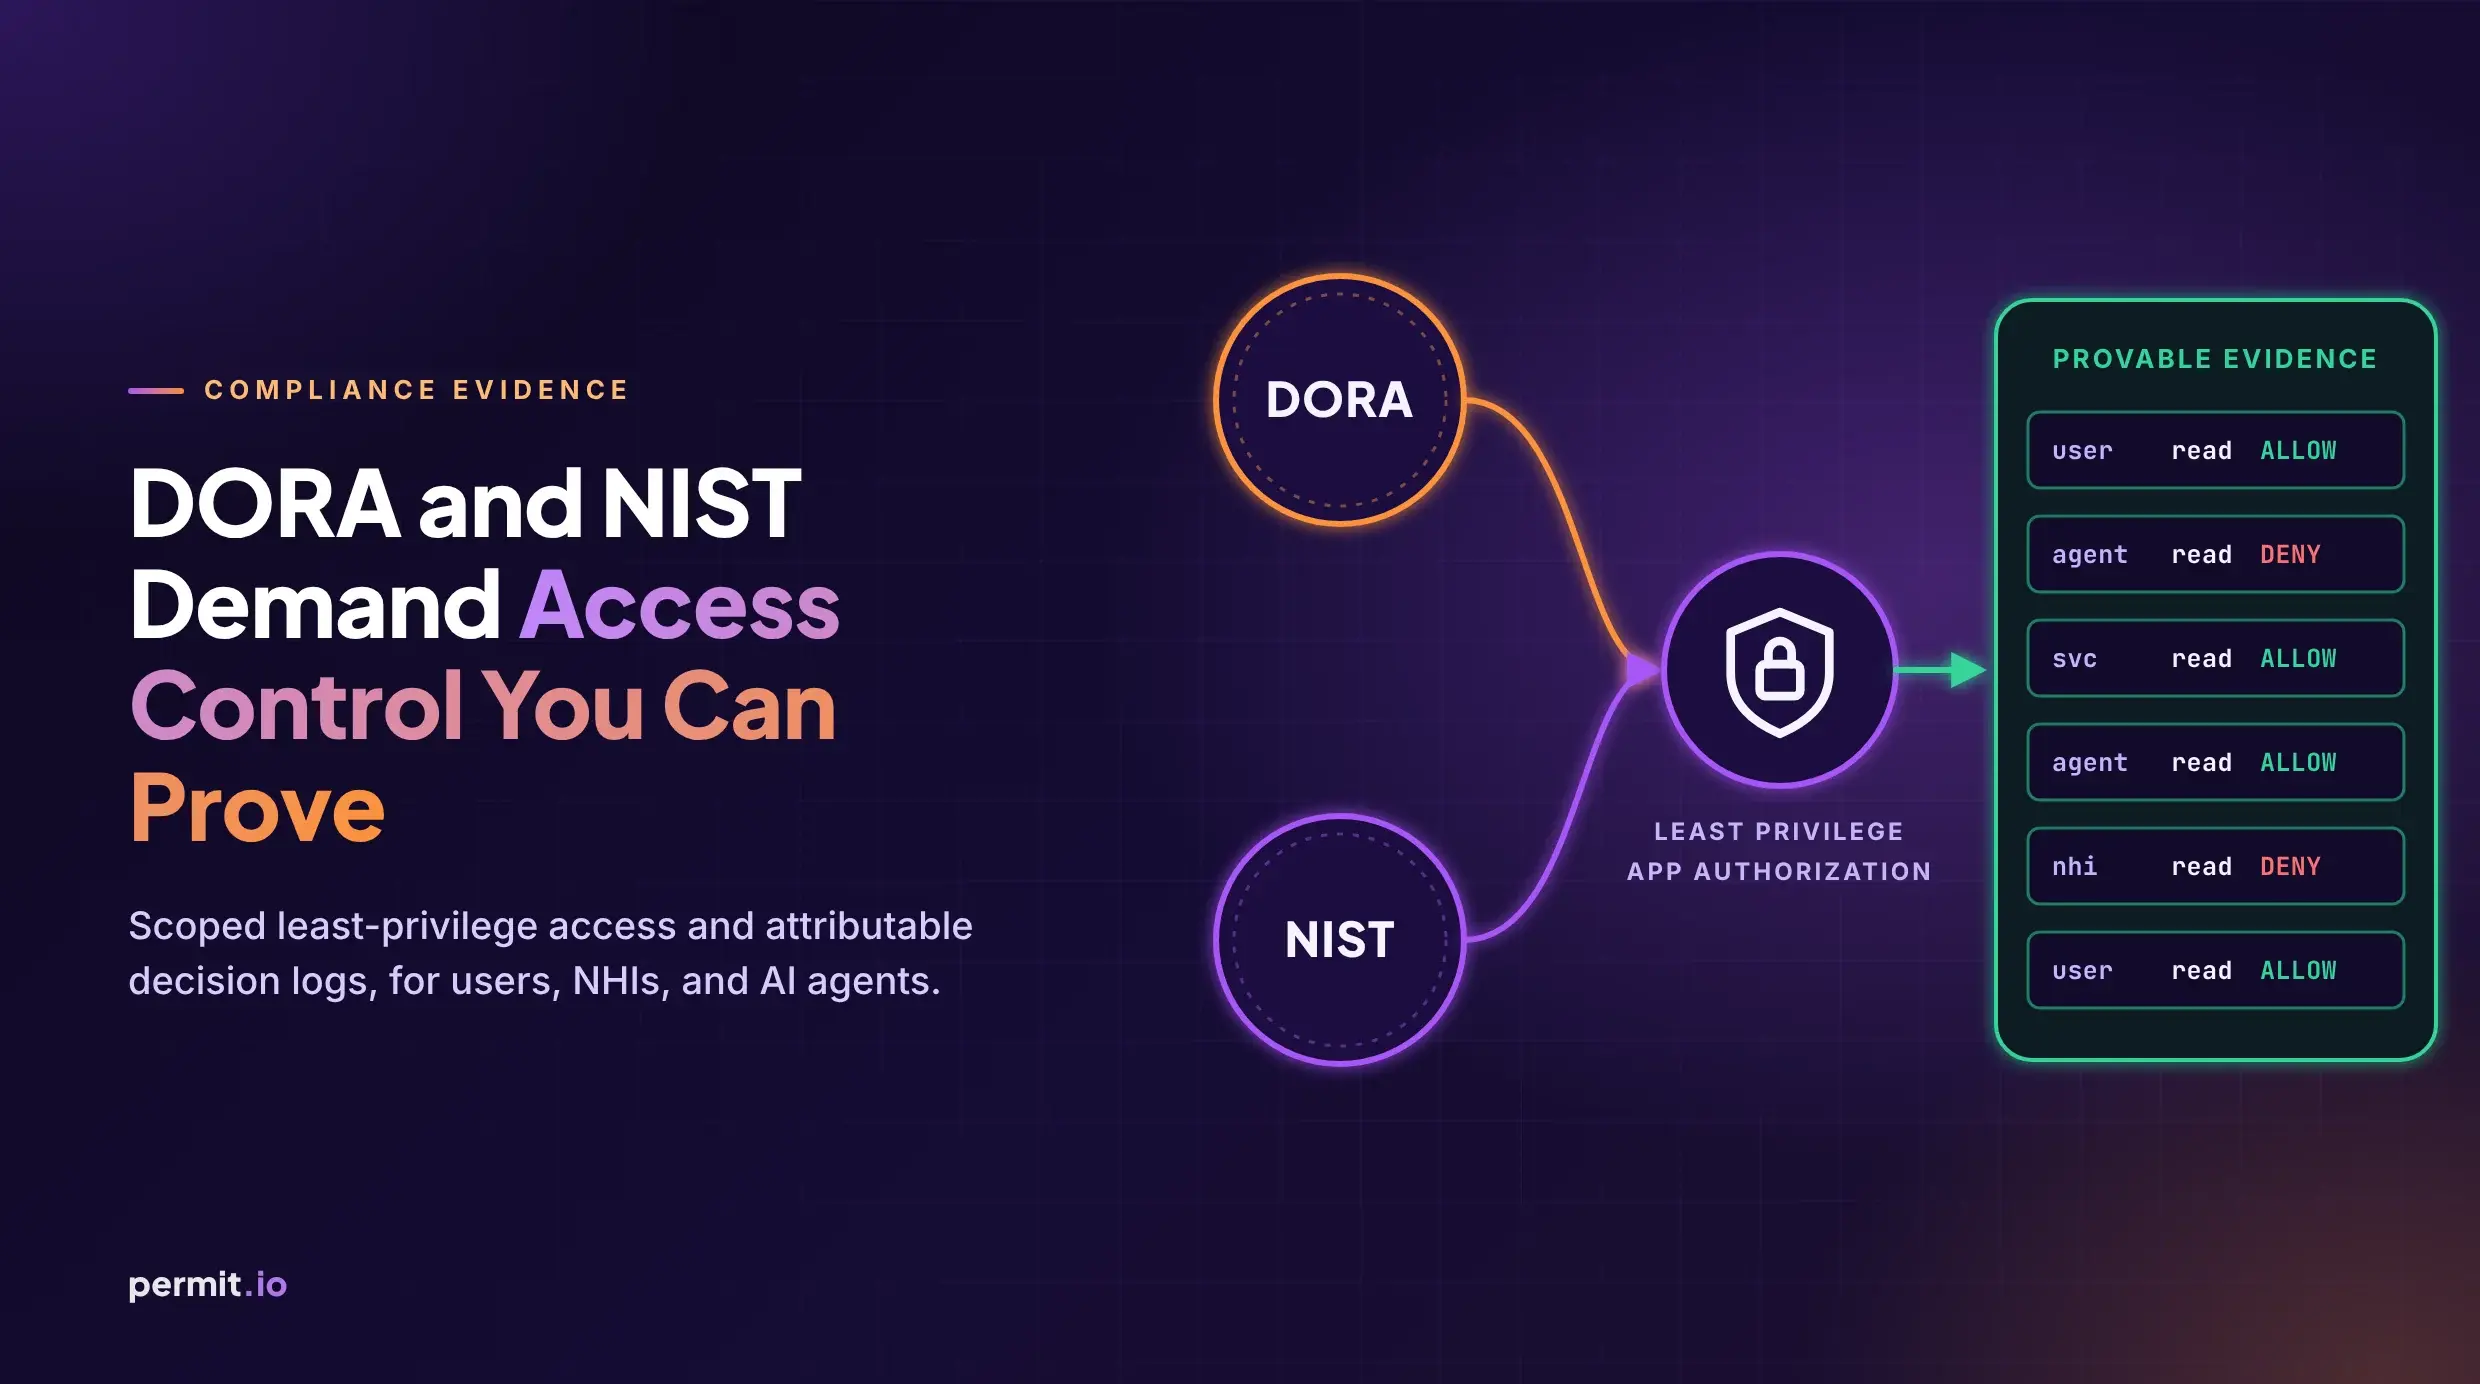
DORA vs NIST on access control: both point to least privilege and attributable logs, for NHIs and AI agents too. Decision logs turn access control into evidence.
Or Weis
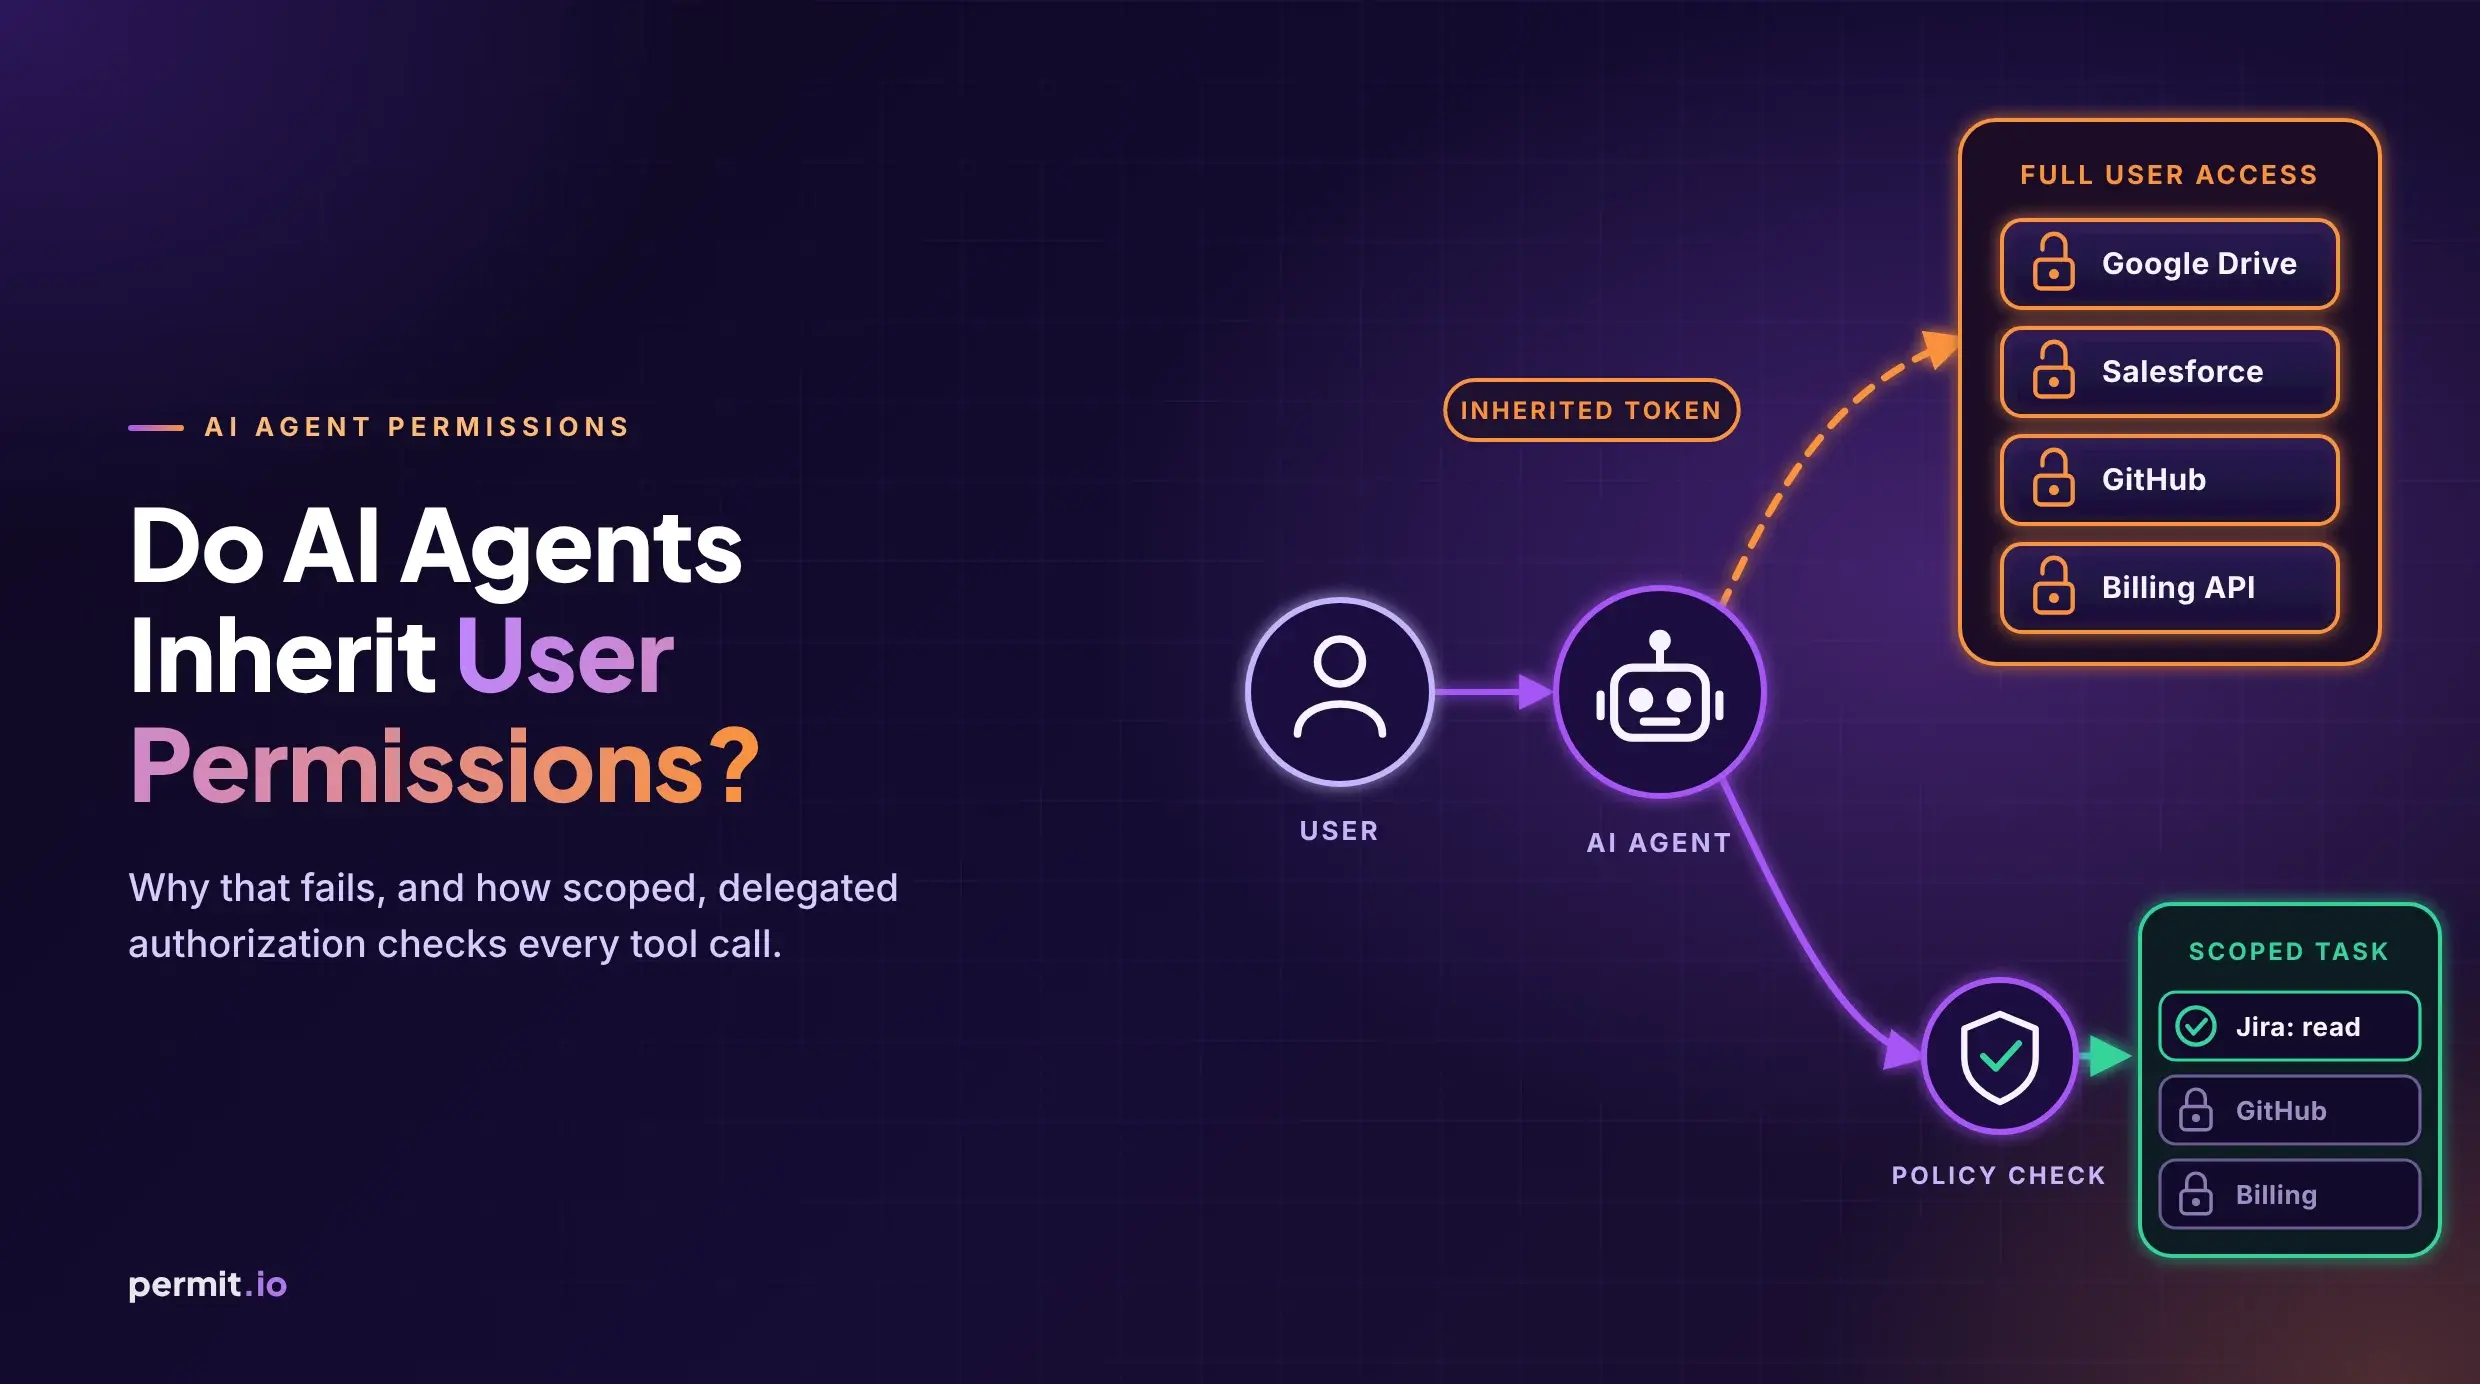
AI agents get their own IdP token, separate from the user session. OAuth scopes are too coarse for resource-level rules; check agent role at each tool call.
Or Weis
Your authorization model shapes least-privilege evidence in access reviews. Role assignments, attribute conditions, and relationship tuples each prove different things.
Or Weis
Hybrid authorization by default: RBAC for org roles, ABAC for context, ReBAC for sharing graphs—one check API across models. How to pick a stack before role explosion, and why least privilege needs explainable entitlements.
Or Weis
AuthN proves who you are; AuthZ decides what you can do. See the 401 vs 403 difference, real SaaS examples, and how to separate identity from permissions.
Or Weis
SOC 2-style access reviews need more than IdP login events. Explainable allow and deny decision logs — decision provenance from identity to policy to resource — are the authorization evidence that makes application-level access controls concrete.
Or Weis
Every authorization decision should be explainable. Authorization observability is not more logs — it is decision provenance. Here is how to build an audit trail that answers why access was allowed or denied.
Or Weis
Fine-grained authorization belongs in a dedicated control plane—not scattered if-statements. Learn when to externalize authorization and stop rebuilding DIY RBAC in application code.
Or Weis
MCP servers are now operational control surfaces for cloud and API platforms. This article explains the trust model, control stack, and audit architecture enterprises need before AI agents can safely execute infrastructure actions.