
Or Weis
Announcing Permit MCP Gateway
Announcing Permit MCP Gateway, a new trust and enforcement layer for MCP that brings identity, consent, fine-grained authorization, auditability, and runtime control to AI agent actions.
Read more
Featured Stories
Or Weis
Announcing Permit MCP Gateway, a new trust and enforcement layer for MCP that brings identity, consent, fine-grained authorization, auditability, and runtime control to AI agent actions.
Gabriel L. Manor
The new Permit.io CLI brings developer-first workflows to access control. Define, test, deploy, and enforce fine-grained authorization using AI, CI/CD, GitOps, and OpenAPI — all from your terminal
Or Weis
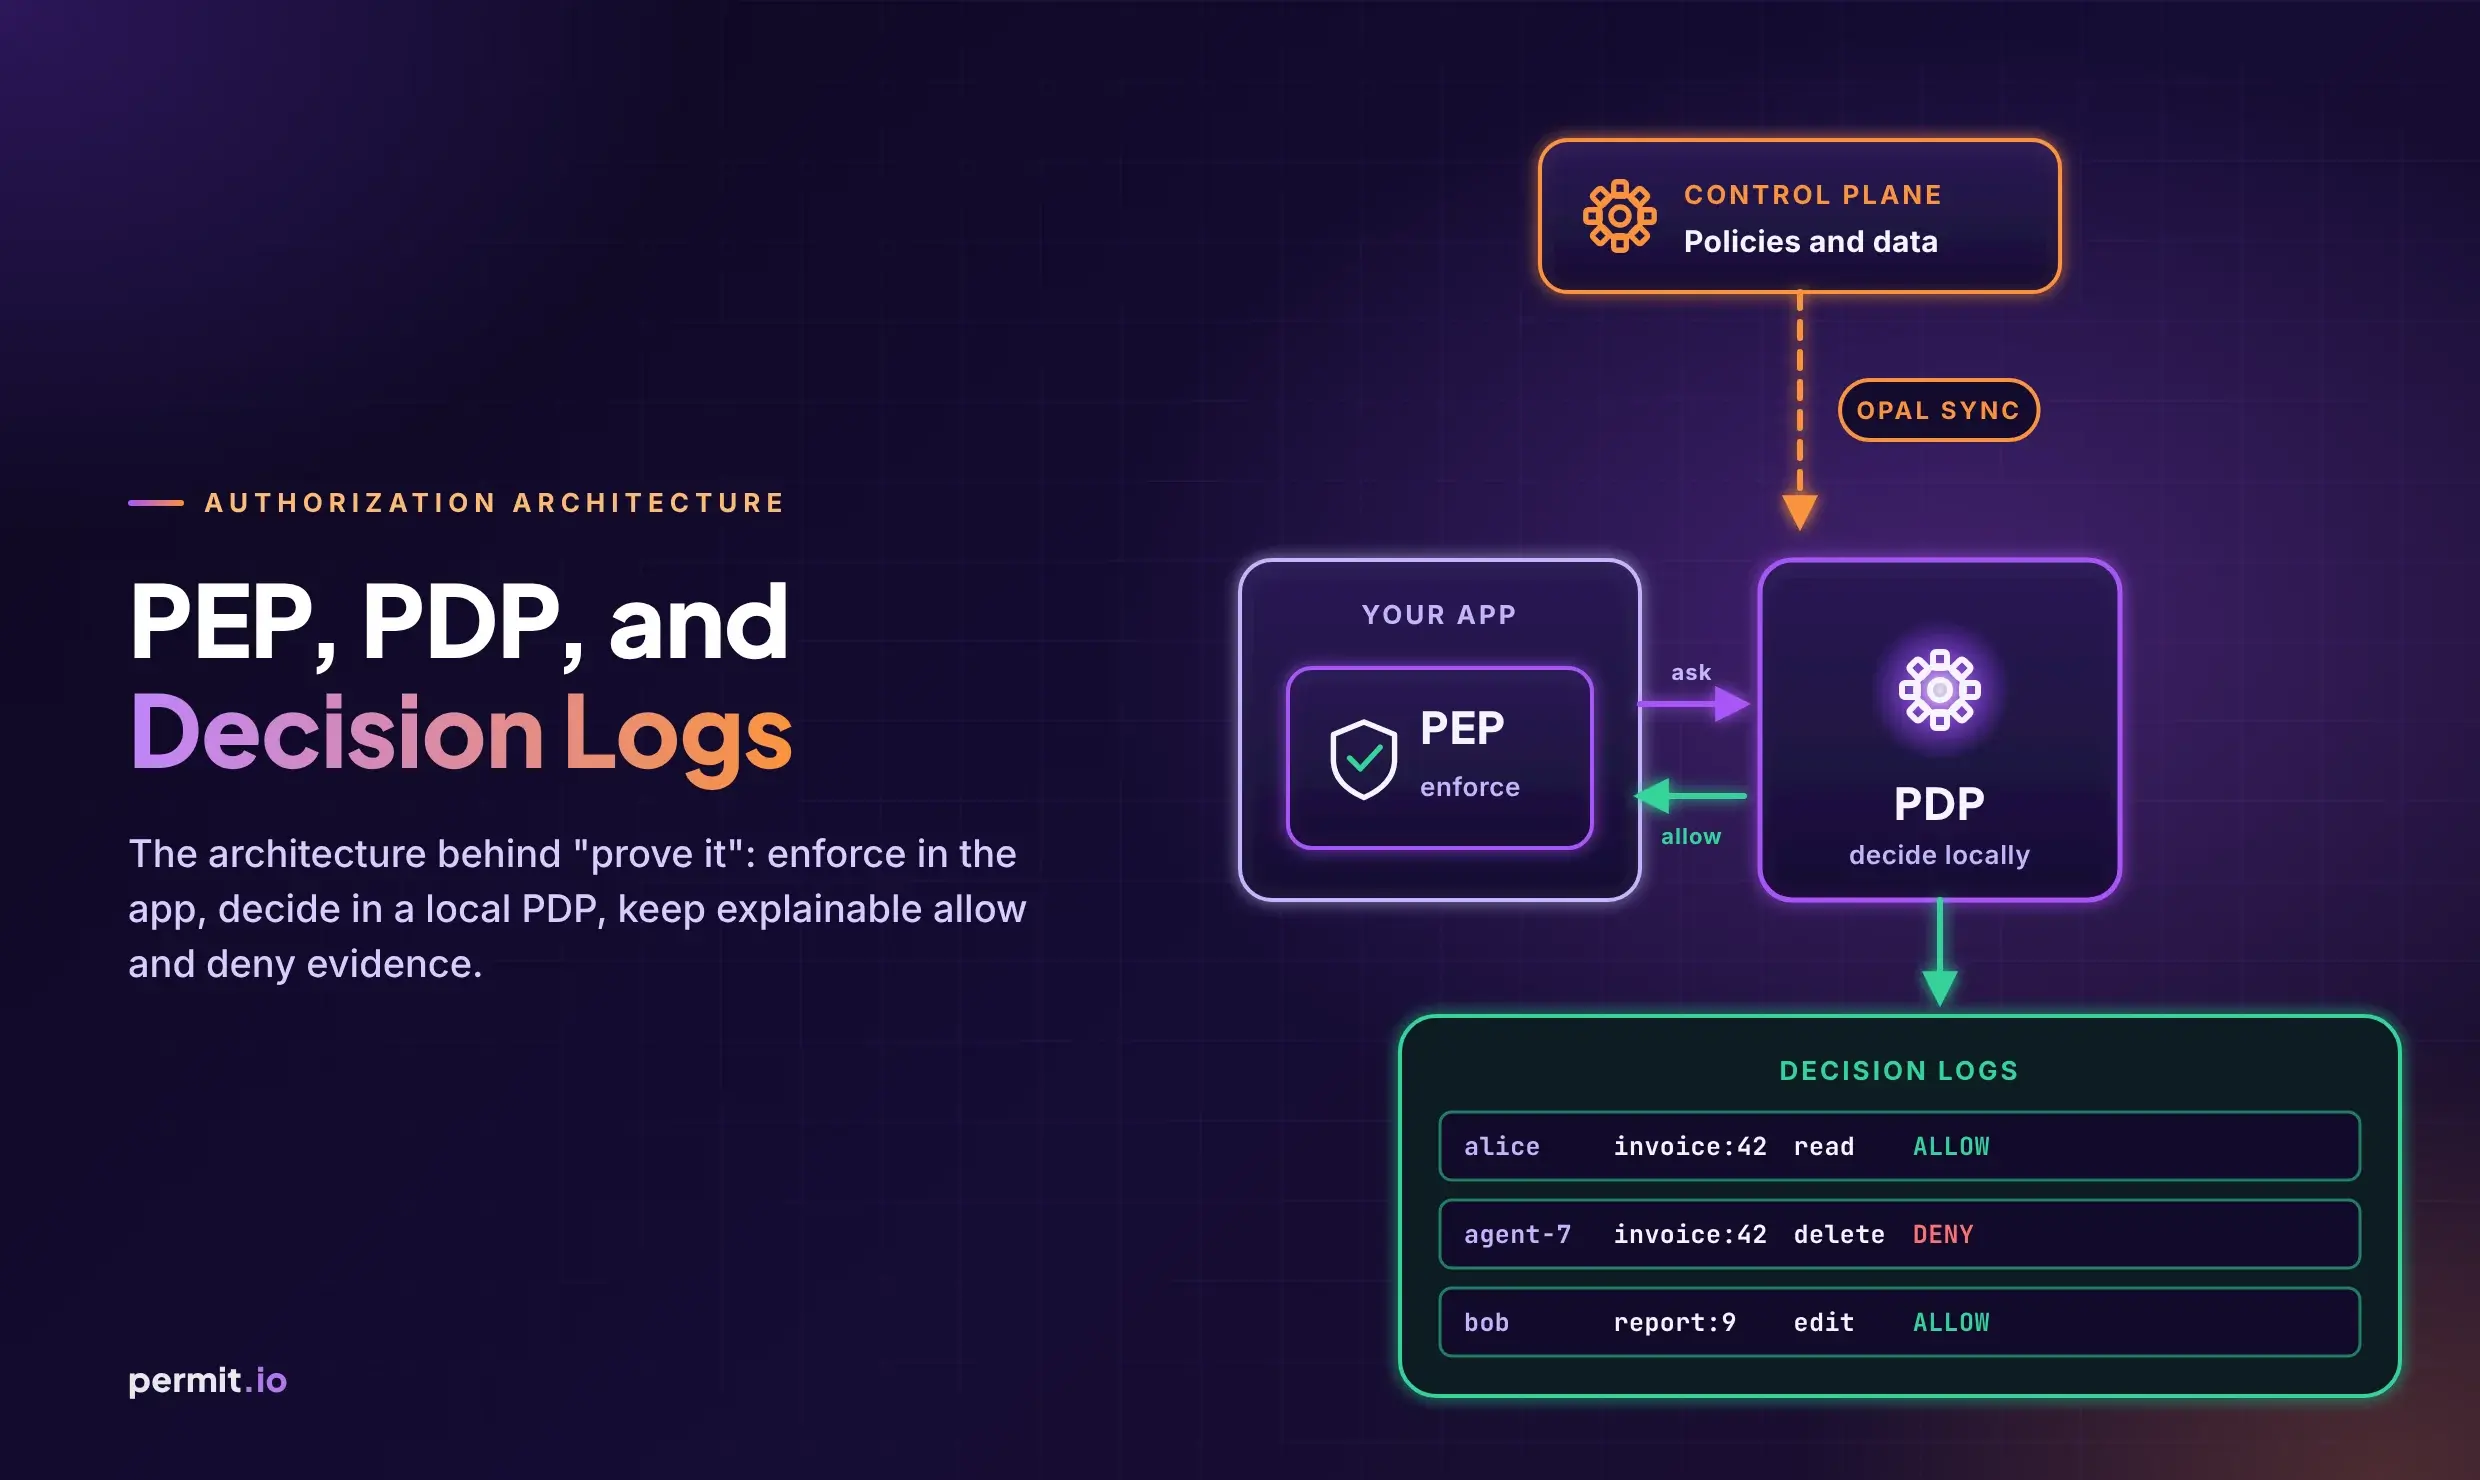
Regulators’ “prove it” maps to PEP + PDP + decision logs: enforce in the app, decide in a local PDP synced by OPAL, and keep explainable allow/deny evidence.
Or Weis
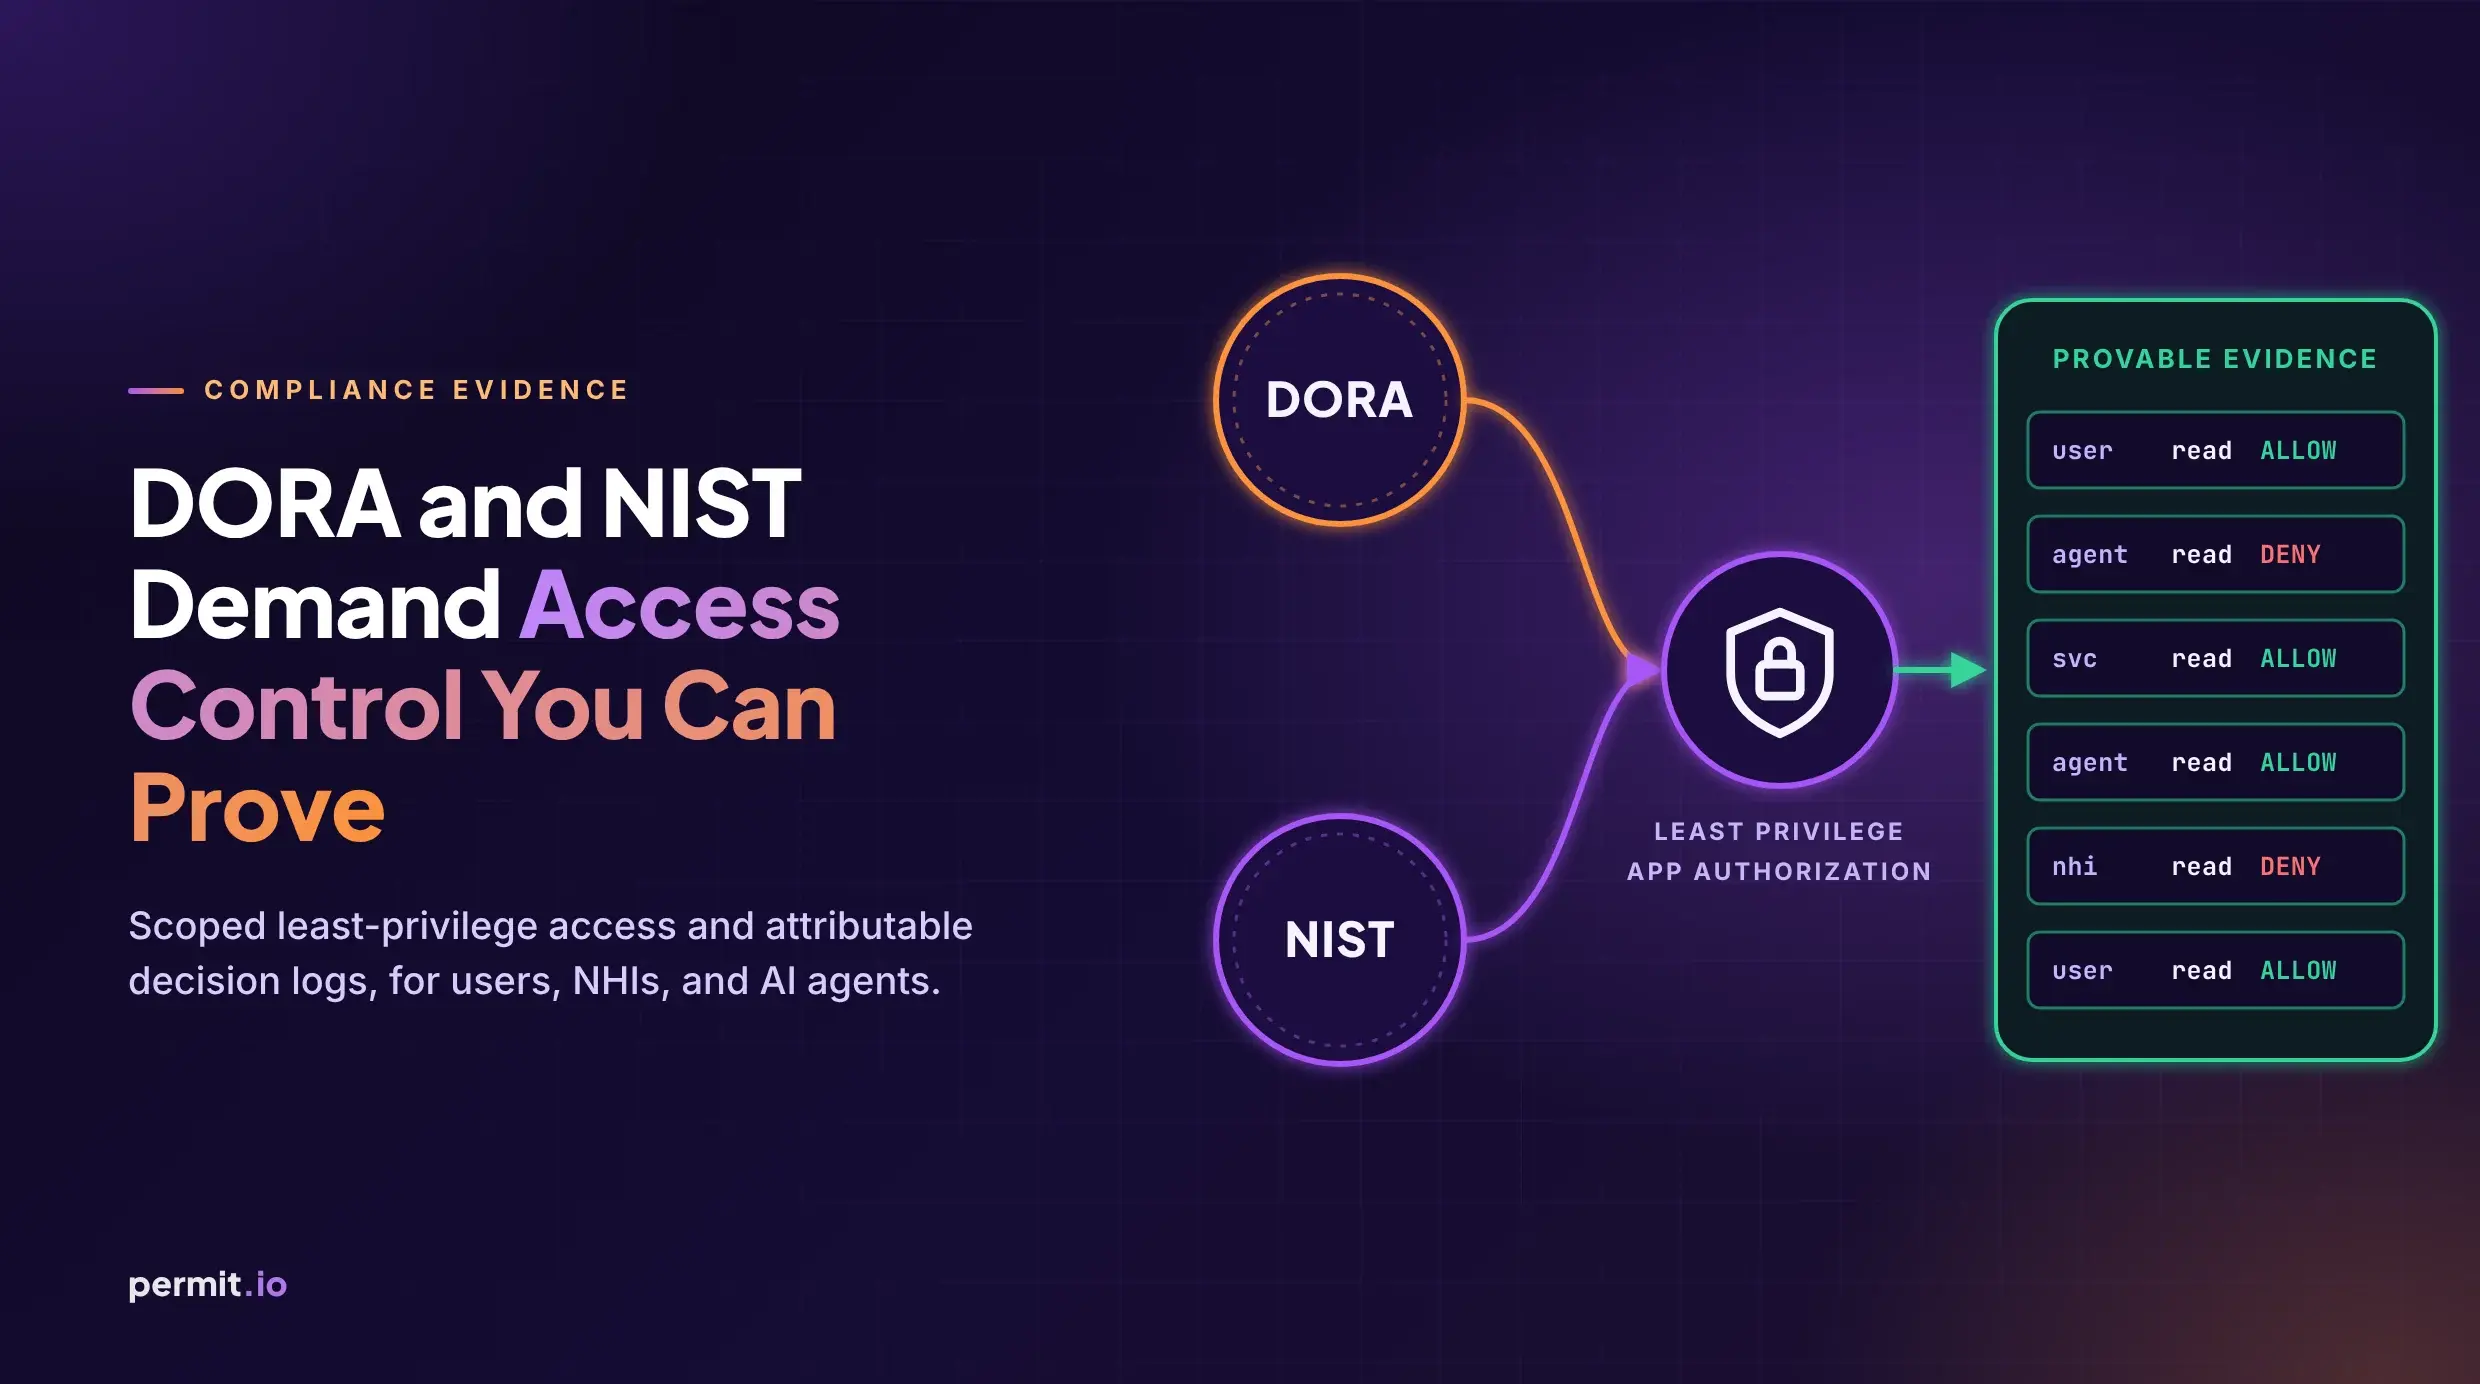
DORA vs NIST on access control: both point to least privilege and attributable logs, for NHIs and AI agents too. Decision logs turn access control into evidence.
Or Weis
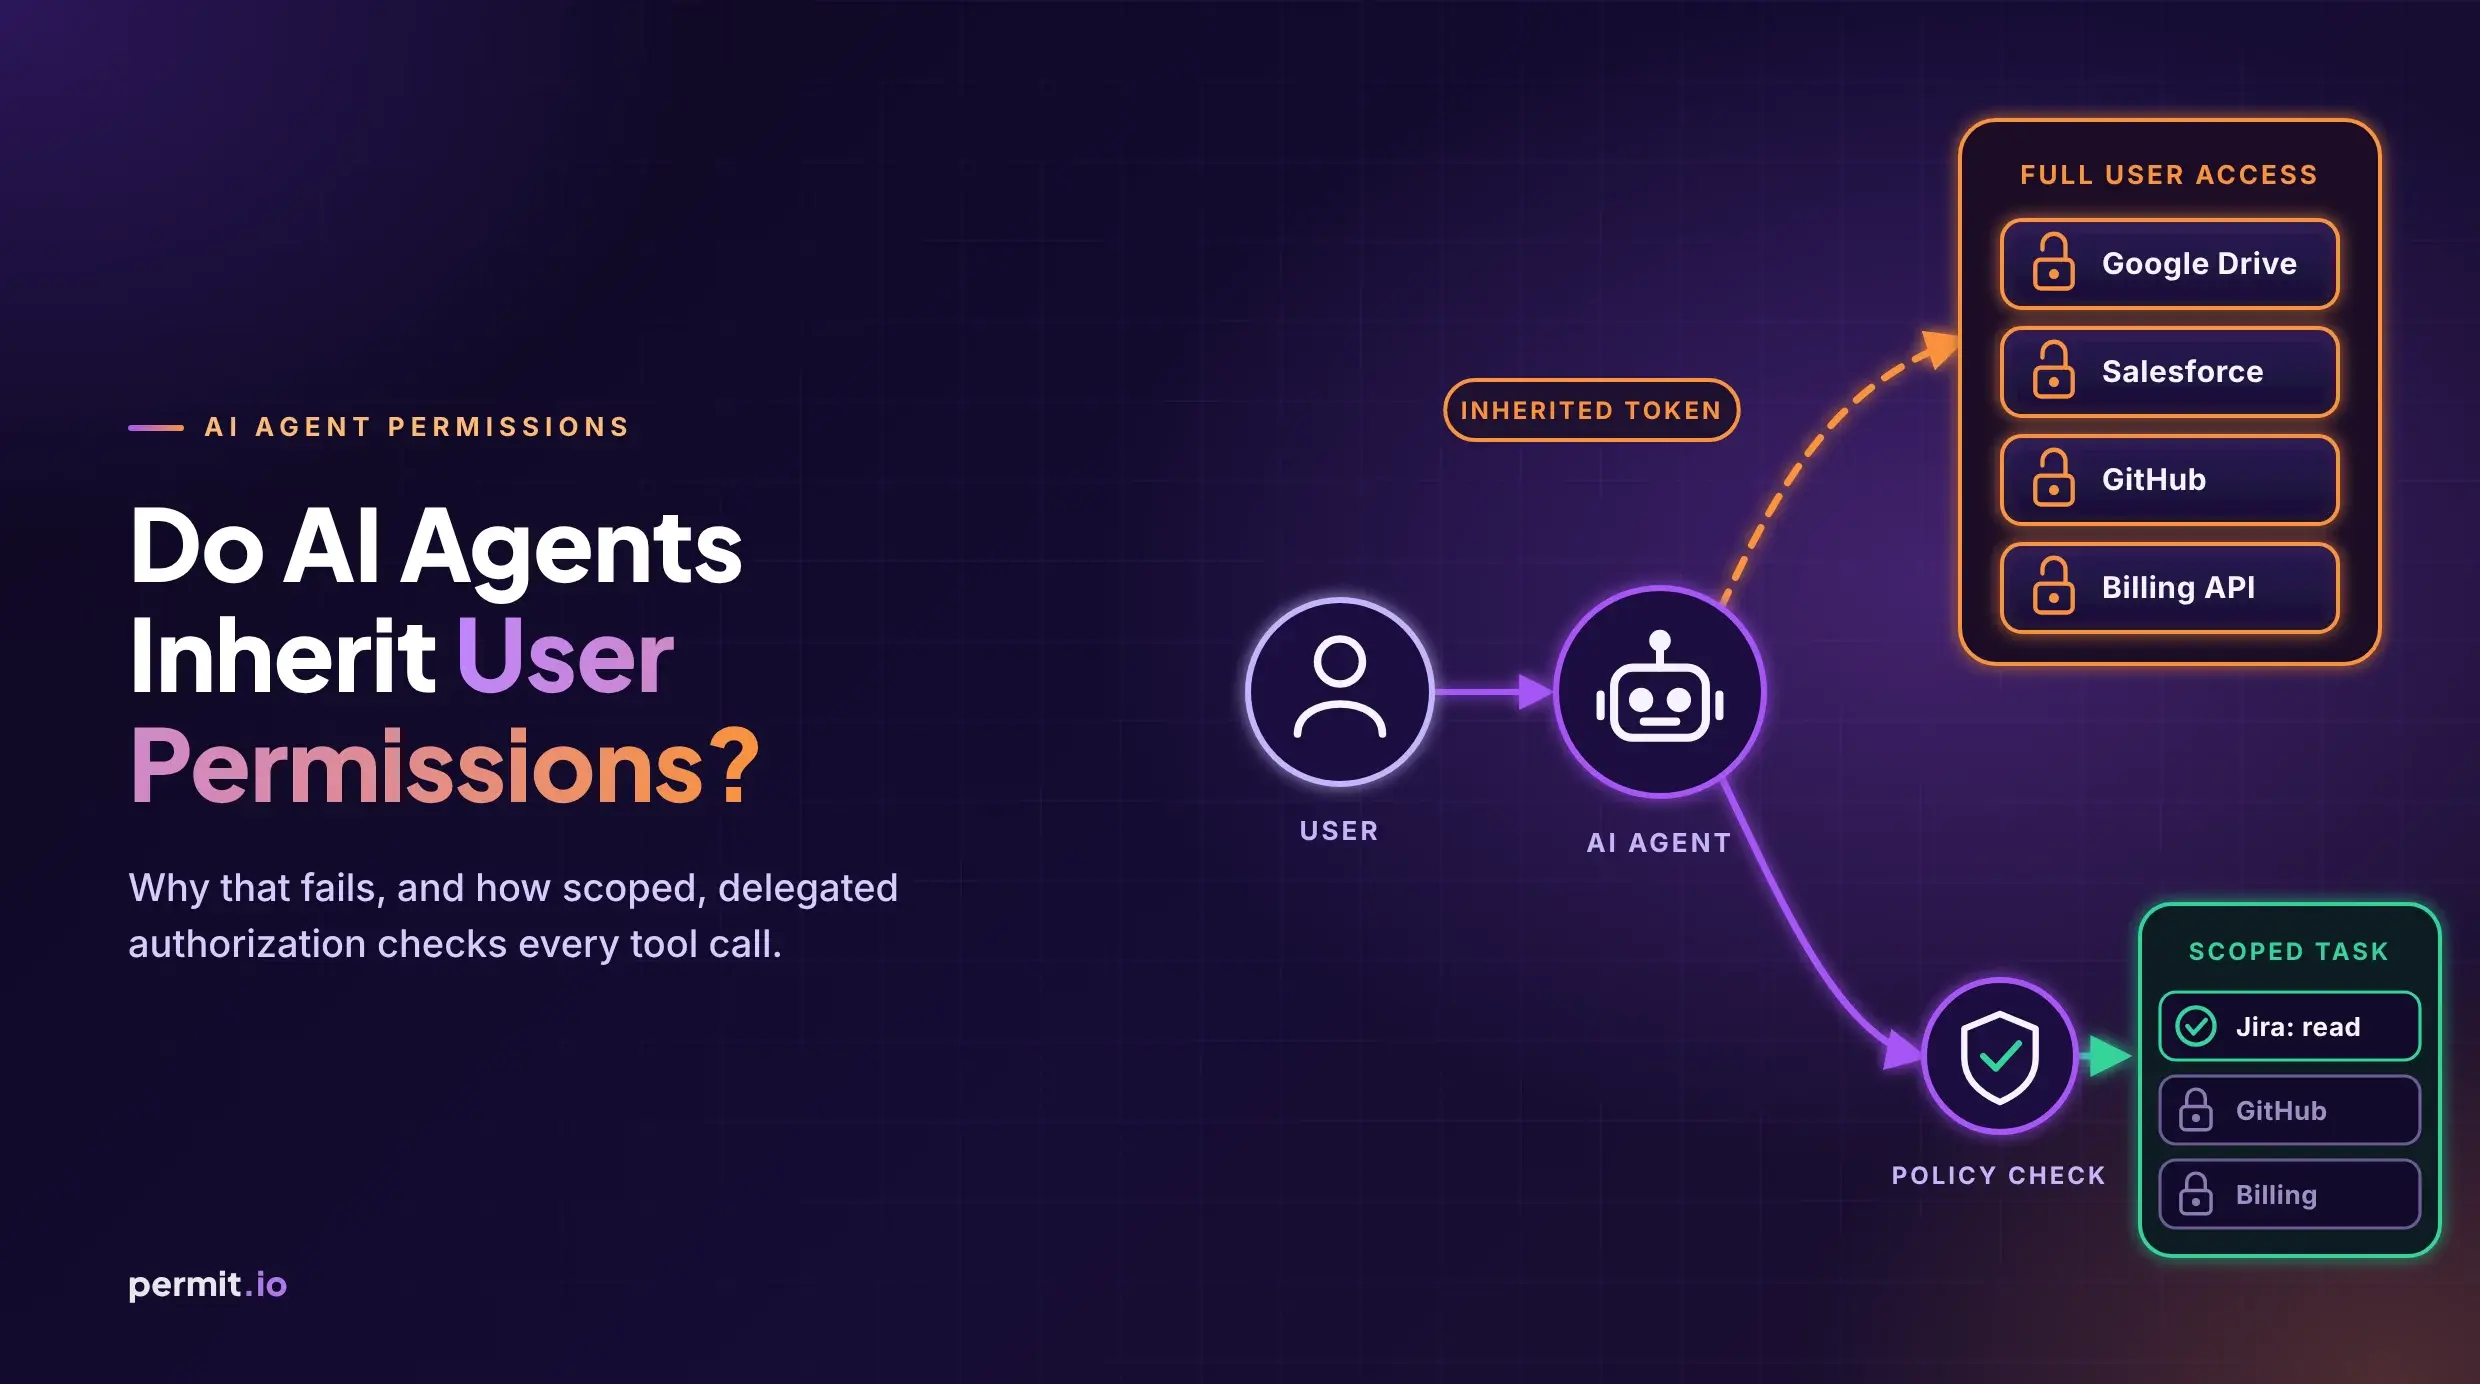
AI agents get their own IdP token, separate from the user session. OAuth scopes are too coarse for resource-level rules; check agent role at each tool call.
Or Weis
Your authorization model shapes least-privilege evidence in access reviews. Role assignments, attribute conditions, and relationship tuples each prove different things.
Or Weis
Hybrid authorization by default: RBAC for org roles, ABAC for context, ReBAC for sharing graphs—one check API across models. How to pick a stack before role explosion, and why least privilege needs explainable entitlements.
Or Weis
AuthN vs AuthZ: authentication (AuthN) checks who a user is, and authorization (AuthZ) decides what they can do. Side by side comparison with real SaaS examples.
Or Weis
SOC 2-style access reviews need more than IdP login events. Explainable allow and deny decision logs — decision provenance from identity to policy to resource — are the authorization evidence that makes application-level access controls concrete.
Or Weis
Every authorization decision should be explainable. Authorization observability is not more logs — it is decision provenance. Here is how to build an audit trail that answers why access was allowed or denied.
Or Weis
Fine-grained authorization belongs in a dedicated control plane—not scattered if-statements. Learn when to externalize authorization and stop rebuilding DIY RBAC in application code.
Or Weis
MCP servers are now operational control surfaces for cloud and API platforms. This article explains the trust model, control stack, and audit architecture enterprises need before AI agents can safely execute infrastructure actions.
Ziv Cohen
Shared coding-agent memory over MCP improves velocity, but every retrieval is a delegated access decision. This guide explains runtime authorization, ReBAC modeling, inheritance boundaries, revocation, and audit design for secure team memory.
Or Weis
The MCP 2026-07-28 spec hardened authentication and routing, but OAuth alone still cannot decide whether a specific tool call should run. This guide explains the authn-vs-authz split and shows how to enforce runtime policy on tools/call.